SShortSingh.
0
ProgrammingDEV Community ·

Google Tests 'Dive Deeper' AI Overviews in Discover, Potentially Diverting Publisher Traffic

Google is experimenting with a 'Dive deeper' feature in Google Discover that inserts an AI-generated topic overview between a content card and the publisher's page a user would normally visit. Google Search VP Robby Stein announced the test on September 18, 2026, noting that the feature opens a short summary with links to related stories, community reactions, and original reporting. The experiment currently applies to video cards, though independent researchers have spotted code flags suggesting possible expansion to article cards — something Google has not confirmed. While publisher links remain visible within the experience, the new design introduces a Google-hosted stop before users reach an external site, raising concerns about reduced referral traffic. Google has not shared click-through data, disclosed affected regions, or provided publishers with an opt-out mechanism, and the test has not been confirmed for wider rollout.
0
ProgrammingDEV Community ·

Developer Shares Lessons from Building XML-to-Markdown Converter for Turkish Legal Docs

A developer has published insights from building a converter that transforms Turkey's UYAP legal document format from XML to Markdown. The project involved writing a DOM tree walker that maps XML elements like paragraphs, tables, and images to corresponding Markdown syntax. Key challenges included handling overlapping bold and italic spans, detecting headings through heuristics such as font size and alignment since UYAP lacks explicit heading tags, and escaping pipe characters inside table cells. The converter also had to manage character encoding issues, as Turkish legal documents may use Windows-1254 encoding rather than standard UTF-8. The full implementation has been made publicly available on GitHub under the repository udf2md.

0
ProgrammingDEV Community ·

JSZip Lets Developers Parse and Create ZIP Files Entirely in the Browser

JSZip is a JavaScript library that enables developers to read and create ZIP archives directly in the browser, eliminating the need for server-side processing. This approach is particularly useful when handling sensitive documents such as legal filings, medical records, or financial data, as the files never leave the user's device. The library supports extracting text, images, and other file types from ZIP archives, as well as generating new ZIP files with DEFLATE compression. For large files exceeding 10MB, JSZip provides a progress callback to monitor processing, with benchmarks showing parse times ranging from around 5ms for 50KB files to roughly 900ms for 50MB files. The technique was applied in a real-world tool called udf2md, which converts Turkish court documents to Markdown in the browser with no backend, aiding compliance with GDPR and Turkey's KVKK data protection regulations.

0
ProgrammingDEV Community ·

GabbyAI Launches as a Platform-First AI Assistant Built on Engineering Principles

A team has launched GabbyAI, an AI assistant designed from the ground up as a platform rather than a simple chat interface bolted onto a language model. The developers prioritised infrastructure control, a clean API, privacy, and the ability to swap underlying AI models without rebuilding the entire application. GabbyAI runs on Swish-controlled infrastructure, giving the team direct visibility into performance from API request through to inference. PostgreSQL serves as the core database, a deliberate choice to avoid unnecessary complexity that often accompanies AI projects. The platform separates the product layer from the model layer via an inference API abstraction, allowing the underlying AI technology to evolve independently of the broader application.

0
ProgrammingDEV Community ·

Fixing AI Agent Failures: Why Retrieval Bugs Beat Reasoning Flaws

A software developer found that many apparent AI agent reasoning failures were actually retrieval failures — moments when the agent simply could not fetch the right fact at the right time. Research from Anthropic shows that Contextual Retrieval reduces failed retrievals by 49%, rising to 67% when reranking is added, suggesting retrieval quality has an outsized impact on agent performance. The author distinguishes between three distinct memory layers — session memory, durable memory, and retrieval — arguing that conflating them makes debugging harder. A key finding is that even when relevant information is technically present in a prompt, models often fail to use it if it is buried mid-context, a phenomenon known as the 'Lost in the Middle' problem. The developer recommends hybrid retrieval combining keyword search, semantic search, and reranking over pure embedding-based approaches, especially when agents need to handle exact strings like order IDs or policy titles.

0
ProgrammingDEV Community ·

How Gaming Platforms Should Manage DNS Cutover with TTL Scheduling and Audit Trails

Gaming platforms that assign unique subdomains to each tenant face a DNS migration challenge: cached resolver answers outlive record updates, making rushed cutover attempts unreliable. A structured workflow should break the process into four distinct idempotent states — TTL lowering, cache drain wait, record switch, and TTL restoration — each with its own deadline and retry policy. If a scheduler starts late, it must not compress the cache-drain interval to meet the original cutover time; instead, it should recalculate a safe cutover window and log the original target as superseded. The restore step is treated asymmetrically, requiring both an authoritative DNS observation and explicit sign-off from the application owner before the TTL is raised back to normal. The control plane must store an immutable plan identity, versioning, before-and-after record states, and a result digest to distinguish safe retries from conflicting in-flight changes.

0
IndiaTimes of India ·

13-Year-Old Long Island Prodigy with IQ of 168 Accepted into NYU Master's Program

Joe Petraro-Hyppolite, a 13-year-old from Long Island, has been accepted into a master's programme at New York University, making him an exceptionally rare student at that level. The teenager reportedly has an IQ of 168 and demonstrated early academic brilliance by scoring 1590 on the SAT at age 10. He completed high school at just 11 years old, years ahead of his peers. His achievements are particularly notable given that he has faced serious health challenges, including leukemia and Tourette syndrome. Joe plans to pursue studies in sports management and biology as he continues his extraordinary academic path.

0
ProgrammingDEV Community ·

JFrog Artifactory Flaws Actively Exploited, Enabling Full Supply-Chain Compromise

JFrog disclosed and patched three authentication and authorization vulnerabilities in self-hosted Artifactory in September 2026, with CVSS scores ranging from 7.5 to 9.8. The most critical flaw, CVE-2026-82329, allows attackers to forge a cluster join token via an empty default join key and escalate to platform administrator. Security vendors reported that attackers were chaining these flaws to create persistent admin accounts, install malicious plugins, and export credentials and repository configuration. Because Artifactory acts as a central credential store for CI/CD pipelines, a compromised instance can expose every downstream build system that trusts it, including cached packages. CISA added the vulnerabilities to its Known Exploited Vulnerabilities catalog on September 12, 2026, setting a federal remediation deadline of September 25, with JFrog recommending upgrades to fixed versions 7.161.20 or 7.133.11 depending on the branch.

0
ProgrammingDEV Community ·

AI Agent Workflow Proposed to Manage Full Software Feature Development End-to-End

A new workflow has been proposed on DEV Community to help engineering teams use AI agents to implement entire software features, not just individual tasks. The system breaks a high-level 'Epic' into a dependency graph of smaller tasks, each processed through dedicated Planner, Builder, and Reviewer agents running in parallel where possible. A shared Epic document provides agents with objectives, constraints, and acceptance criteria, while the codebase itself supplies the technical ground truth. All task branches are ultimately merged into a single integration pull request that passes CI checks before requiring human approval. The approach aims to minimize manual intervention while preserving oversight controls proportional to the risk level of each change.

0
SpaceNASA ·

Spring or Fall, Equinoxes Have Guided Human Astronomy for Millennia

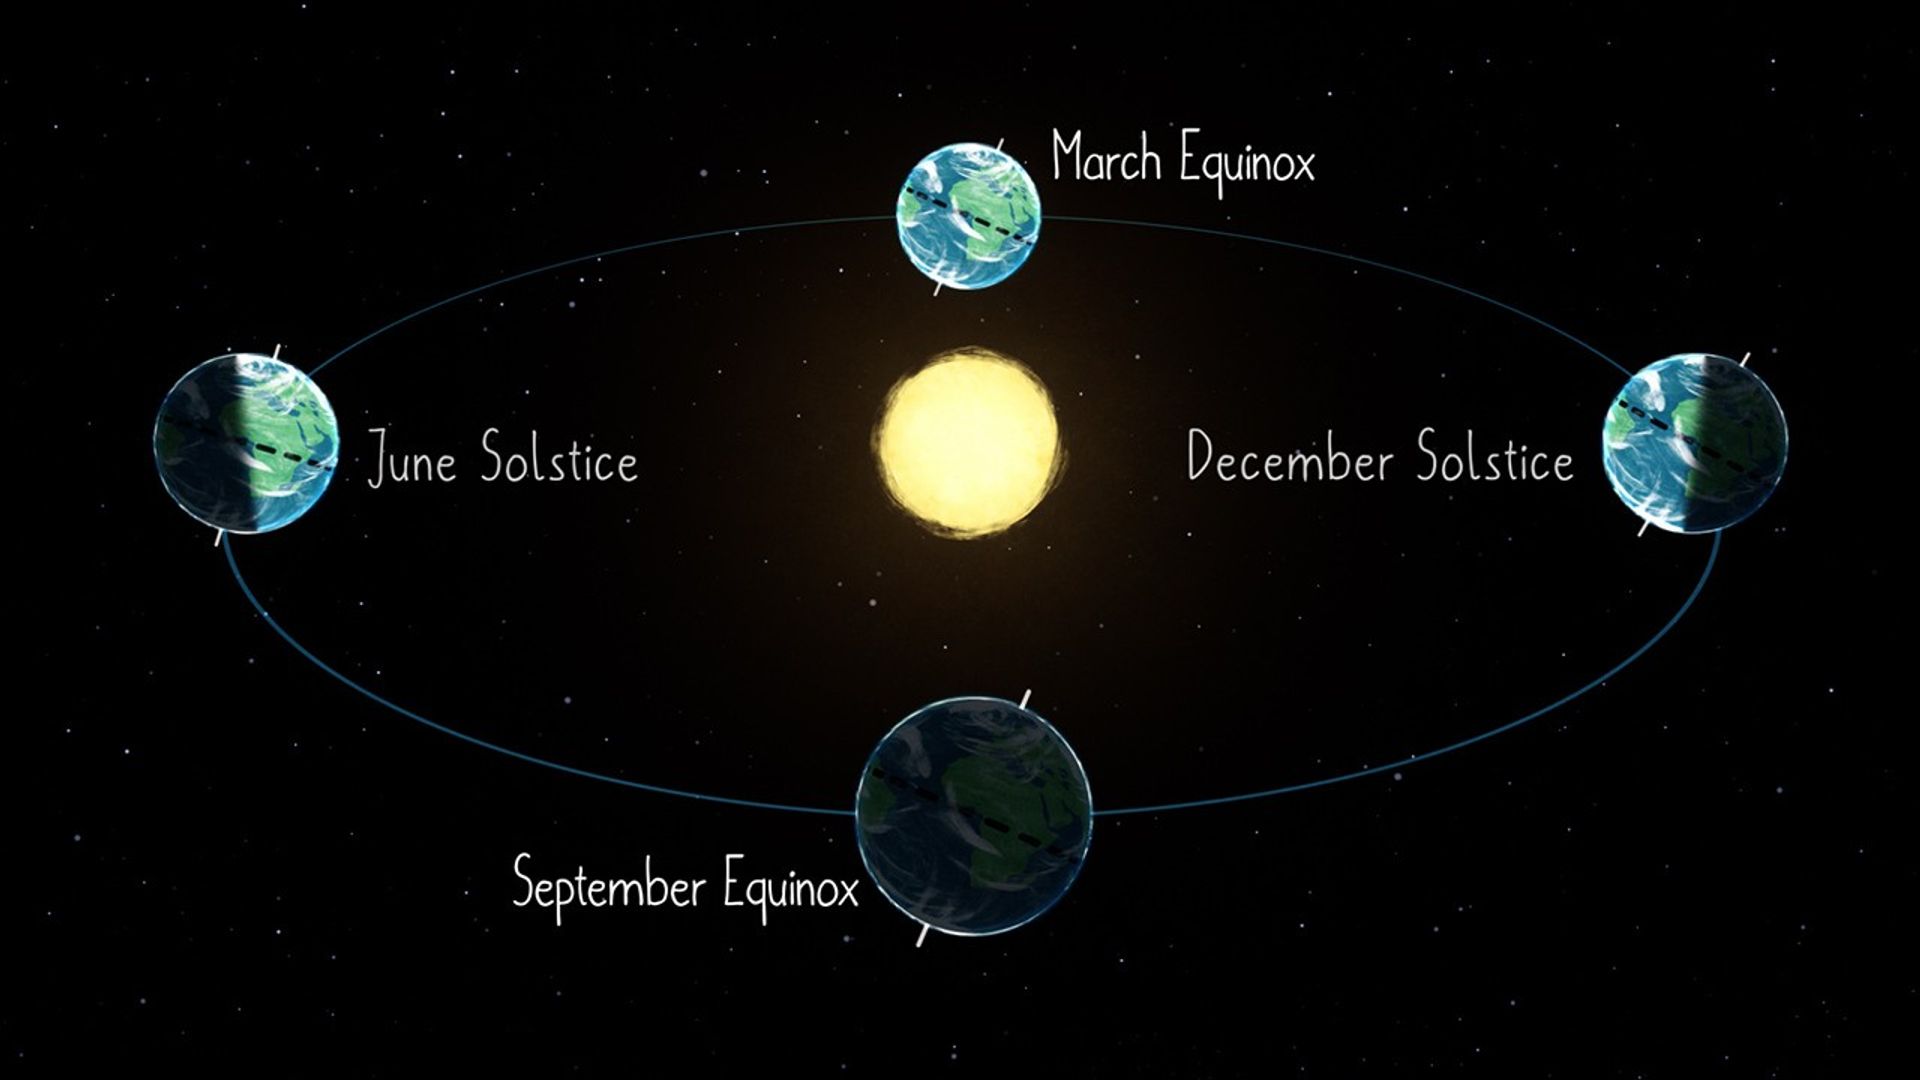
An equinox marks the point in Earth's orbit when day and night are roughly equal in length, occurring twice each year. The significance of equinoxes varies by region, with some cultures associating them with the arrival of warmer weather and others with longer, darker nights. Tracking and predicting equinoxes is considered one of the oldest practices in human astronomy. Ancient observatories across the world were built or used to monitor equinoxes alongside the more visually dramatic solstices. NASA highlights this long astronomical tradition as humanity continues to observe these celestial events today.

0
ProgrammingDEV Community ·

Turkish Dev Team Launches Open Source Toolkit for E-Signature and E-Transformation

The E-İmza.plus team has released an open source project called 'awesome-turkiye-e-donusum', aimed at supporting Turkey's digital transformation ecosystem. The project provides libraries, tools, and guides covering e-signature, fiscal seal, KEP (registered email), e-invoice, UYAP, and related systems. It is designed to make life easier for both developers and end users working with electronic document processes in Turkey. The project carries no license restrictions and can be self-hosted, tested locally, or integrated into other projects. The source code is publicly available on GitHub, and the team is actively welcoming community contributions via pull requests.

0
ProgrammingDEV Community ·

Dev Blog: How FoxyInvoice Set Up Domain, Hosting, DNS, and Email From Scratch

A developer building FoxyInvoice in public has published Chapter 6 of their series, detailing the full infrastructure setup required to take a local codebase live on the web. The guide covers purchasing a domain, configuring Cloudflare DNS, provisioning a single Linux VPS, and wiring up services including AWS SES for email, S3-compatible object storage, and Stripe for payments. A key technical warning is highlighted: Cloudflare's proxy must be disabled for certain DNS records so that Caddy's automatic TLS certificate provisioning can work correctly. The post also documents real mistakes encountered, such as an unverified email destination triggering a mailer-daemon storm and Docker Compose environment file mix-ups causing database authentication failures. The series is maintained in a public GitHub repository, with Chapter 7 set to cover CI/CD automation.

0
ProgrammingDEV Community ·

Open-Source Browser Tool Lets Turkish Users Edit UYAP Legal Docs Without Java

A Turkish team called E-İmza.plus has released an open-source, browser-based editor for the UYAP UDF document format used in Turkey's official judicial system. The tool runs entirely on the client side, meaning no data is sent to any server, and it works offline once loaded in a browser. It eliminates the longstanding requirement to install Java and supports Windows, macOS, and Linux without compatibility issues. Users can import Microsoft Word (DOCX), text-based PDF, and scanned TIFF files — with the latter processed via Tesseract.js OCR entirely within the browser. The project is freely available on GitHub and welcomes community contributions including additional templates and e-signature integration.

0
ProgrammingDEV Community ·

API Security Risks Grow as Authorisation Gaps Outpace Firewall Protections

APIs have become the dominant interface for mobile, partner, and internal systems, but their reliance on long-lived tokens rather than network-level protections creates an expanding attack surface. Security experts identify broken object-level authorisation and excessive data exposure as the two most prevalent failure patterns, both catalogued in the OWASP API Security Top 10. A notable 2021 Peloton incident illustrated the risk, where an unauthenticated endpoint exposed user profile data due to missing authorisation checks. Recent breaches at identity and data providers have similarly involved token theft and API misuse rather than traditional software vulnerabilities. Security practitioners recommend maintaining a live API inventory, enforcing per-request authorisation, minimising data returned by endpoints, and monitoring for enumeration patterns to reduce exposure.

0
ProgrammingDEV Community ·

Workflow Separates Auto-Generated Config Docs from Human-Signed Operational Facts

A documentation workflow proposed for software teams splits configuration reference generation into two distinct lanes: parser-extracted facts and human-signed operational data. Automated tools can reliably pull flag names, environment variables, and help text directly from source code, but production defaults, secret classifications, and deprecation windows cannot be safely inferred this way. AI drafting models often produce config tables that appear complete but silently embed laptop-environment defaults or expose credential names copied from example files. The proposed method uses a signed-cell grid where operational fields must remain empty or marked UNSIGNED until a named reviewer explicitly approves them, with CI configured to block publication if any UNSIGNED markers remain. This approach treats unsigned operational cells as a reviewable defect rather than a philosophical debate about AI tooling.

0
ProgrammingDEV Community ·

Five CI/CD Pipeline Audit Checks That Can Prevent Costly Outages

CI/CD pipelines often grow organically over time, accumulating workarounds and undocumented steps until they become fragile and poorly understood. A practical audit checklist highlights five key risk areas: deploy access accountability, actual rollback timing, environment parity between staging and production, test suite health, and deployment-correlated monitoring. Teams are advised to physically time rollbacks in staging rather than relying on assumptions, as manual database or cache steps are frequently overlooked. Skipped tests and slow pipelines are flagged as warning signs that warrant investigation rather than workarounds. The audit requires no specialized tooling — only a willingness to challenge long-held assumptions before an incident forces the issue.

0
ProgrammingDEV Community ·

Hidden Architecture Traps That Can Derail Your SaaS MVP Later

Many decisions made during MVP scoping appear to be minor feature choices but are actually foundational architecture decisions with long-term consequences. Key areas include multi-user account structures, permissions systems, subdomain-based tenancy, data isolation, and billing logic — each of which becomes significantly harder to retrofit after launch. For example, adding flexible user roles or subdomain routing after customers are already live often requires complex migrations rather than simple configuration changes. Similarly, designing data models without clean tenant boundaries makes tasks like deleting a single customer's data unexpectedly difficult down the line. Experts advise that acknowledging these architectural implications early — even if full functionality ships later — can save SaaS teams costly rebuilds as the product scales.

0
ProgrammingDEV Community ·

How WiFi QR Codes Work and How to Create a Reliable One

A WiFi QR code is simply a standardized text string encoding a network name (SSID), security type, and password, which modern iPhones and Android devices can read natively without any third-party app. When a camera scans the code, the device automatically prompts the user to join the corresponding network. To generate one, users enter their network name (case-sensitive), password, and security type — almost always WPA/WPA2 — into any QR code generator. Security best practices recommend using a guest network rather than a primary one, so that scanned devices are kept separate from personal computers. The encoded password means any change to WiFi credentials instantly invalidates the old QR code, so regenerating and testing on both iOS and Android before printing is essential.

← NewerPage 1444 of 6013Older →