SShortSingh.
0
Crypto & Web3CoinDesk ·

Layer-2 and DeFi tokens surge as markets calm after Fed rate hike fears

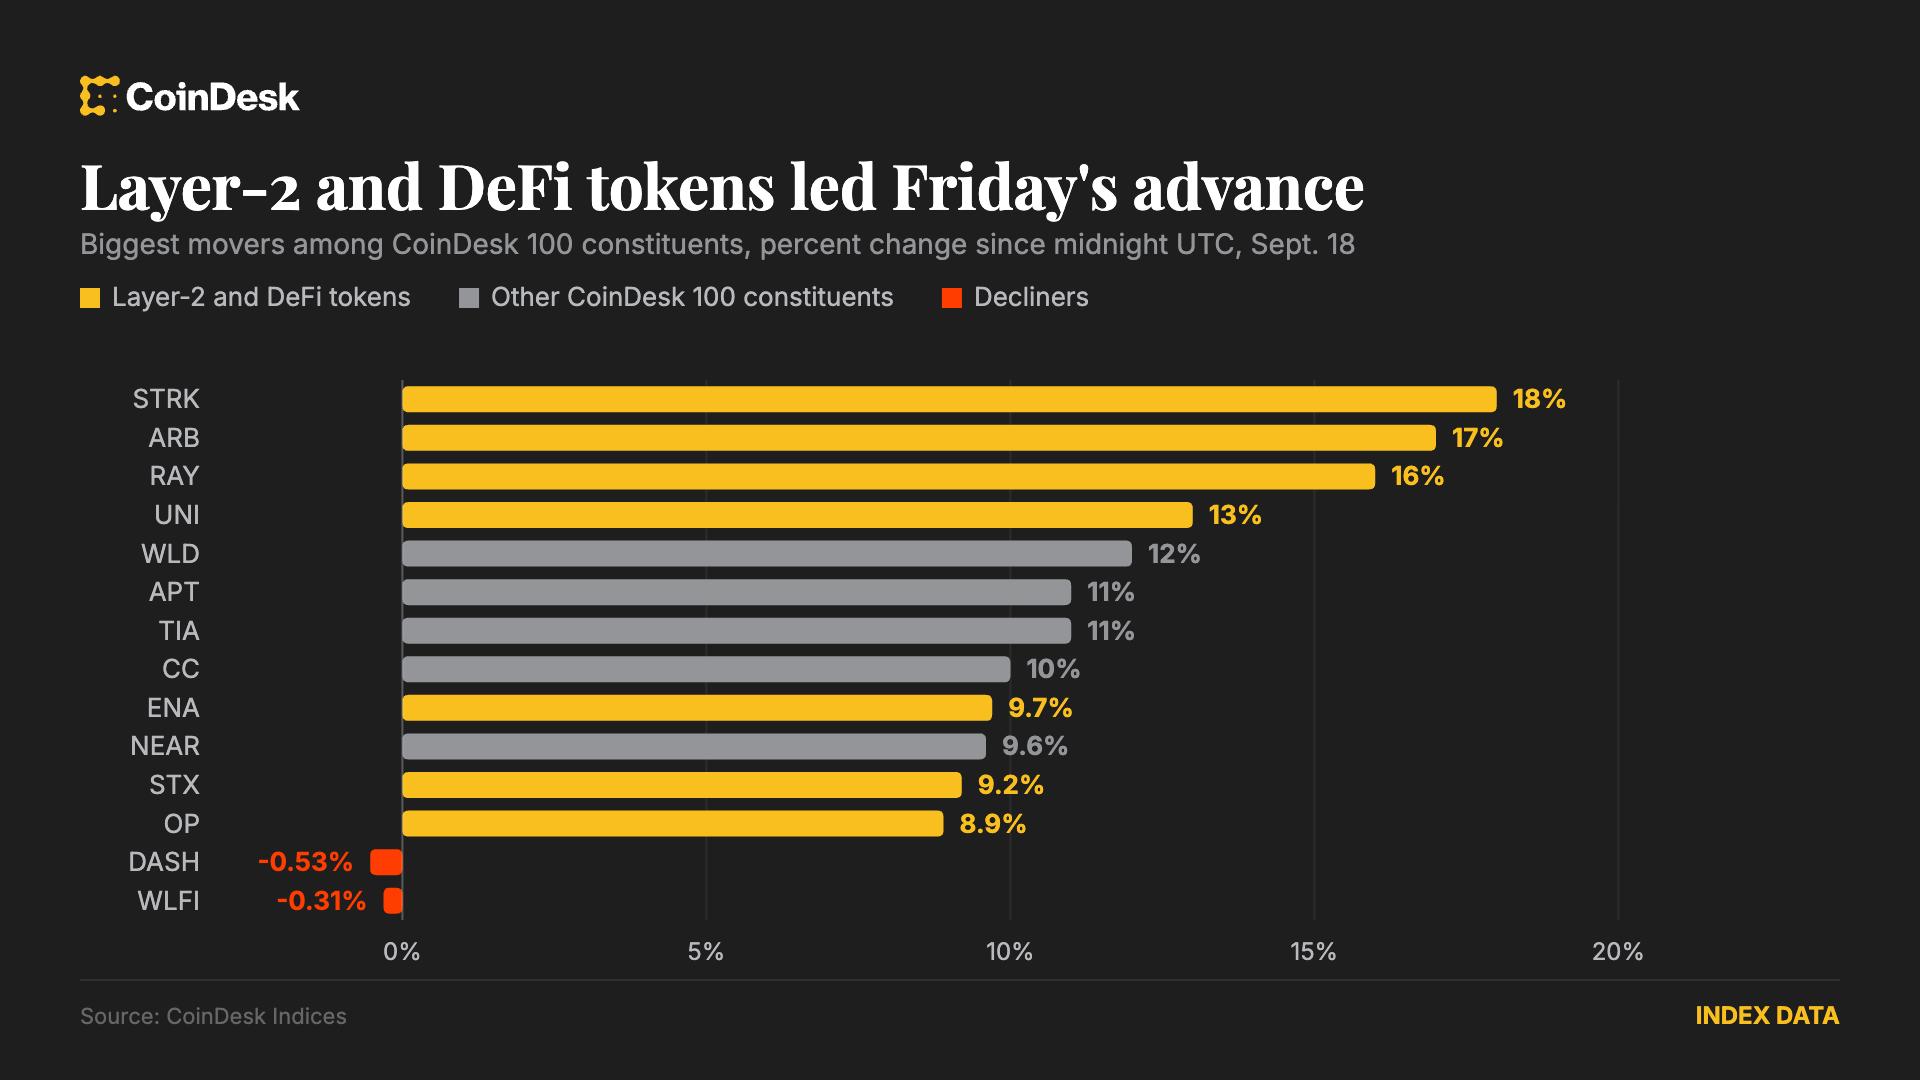
Cryptocurrency markets staged a broad recovery as post-Federal Reserve rate hike anxiety eased. Layer-2 blockchain tokens Starknet and Arbitrum were among the top performers, each gaining over 17%. The rally was widespread, with 98 out of 100 tokens in the CoinDesk 100 index recording gains. Adding to the positive sentiment, the 10-year US Treasury yield retreated to below the 5% mark, signaling reduced pressure on risk assets.
0
ProgrammingDEV Community ·

Node.js 26.9 enables FFI by default, benchmarks show 37ns per call

Node.js 26.9.0, released on 16 September, makes the node:ffi module available by default, removing the need for the --experimental-ffi flag that was previously required in earlier 26.x versions. The change inverts the flag logic: --no-experimental-ffi is now needed to disable the feature, marking a genuine behavioral shift rather than a documentation update. Benchmarks comparing node:ffi against N-API addons show FFI is roughly 7-8% slower per call at around 37 nanoseconds, meaning it does not offer a performance advantage over existing native addons. However, FFI outperforms N-API by 15-20% in bulk buffer operations, where a single call processes large datasets, making it better suited to high-volume data transfers than frequent small calls. The key practical benefit of node:ffi remains convenience — it eliminates the need for a compiler toolchain, node-gyp, or per-ABI rebuilds in deployment environments.

0
ProgrammingDEV Community ·

Developer fixes hidden UX flaw that drove 80% of users away before first run

A developer noticed a sharp drop-off in usage for one of their Apify data-fetching tools, where only 1 in 5 users who opened the input page actually ran the actor. The culprit turned out to be a raw JSON textarea field requiring users to manually enter a structured array of objects — an unintuitive barrier for casual users. The fix involved adding simple, flat individual input fields that internally map to the existing array format, making the tool accessible without breaking advanced multi-item functionality. After spotting the pattern in one tool, the developer audited their entire portfolio and found four more actors with the same issue, applying the same fix across all of them. The incident highlighted that UX friction invisible in code reviews can only be detected by analyzing where real users abandon a product.

0
IndiaTimes of India ·

Chinese Coast Guard Ship Rams Philippine Fisheries Vessel in South China Sea

A Chinese Coast Guard vessel collided with a Philippine Bureau of Fisheries and Aquatic Resources boat in the South China Sea. The Philippine vessel was engaged in refueling local fishermen at the time of the incident. The collision caused structural damage to the Philippine boat, though no injuries were reported. China has claimed that the Philippine vessel disregarded warnings and altered its course before the collision. The incident has further heightened tensions between the two countries in the disputed waterway.

0
ProgrammingDEV Community ·

Proxmox VE Auth Bypass Flaw Exposes Tens of Thousands of Instances Online

A critical authentication bypass vulnerability, tracked as PSA-2026-00043-1, affects Proxmox Virtual Environment versions 7.x through 8.0.3, allowing attackers to gain passwordless root access by exploiting a flaw in the tfa-challenge parameter handling. Internet scans using application fingerprints identified roughly 34,000 to 400,000 Proxmox instances publicly reachable online, depending on the query method used. Security researchers cautioned that a raw port 8006 count of over four million is misleading, as it reflects all services on that port rather than confirmed Proxmox deployments. One affected version branch lacks a vendor patch, meaning some exposed systems cannot be fully remediated through upgrades alone. Administrators are advised to enable two-factor authentication on all accounts, restrict public access to port 8006, and audit logs for unauthorized root logins.

0
ProgrammingDEV Community ·

Developer shares key lessons from 22-day hands-on AI systems building sprint

A software developer documented a 22-day self-directed learning sprint focused on building practical AI systems, covering topics from LLM fundamentals to retrieval-augmented generation (RAG) and automated evaluation. The experiment corrected several common misconceptions, including the true purpose of RAG — retrieving relevant facts at request time rather than serving as a privacy tool — and clarified how embeddings differ from next-token prediction mechanisms. Using tools like Ollama and local models, the developer demonstrated that LLMs are stateless by design, with apparent memory in chat apps being the result of deliberate state management by the application layer. Tokenization tests revealed that prompt costs and latency vary significantly by language, with Hindi requiring roughly 2.5 times more tokens per word than English. The overall takeaway was that a useful AI feature requires the same engineering discipline as any production software: defined inputs, constrained behavior, observability, and measurable evaluation criteria.

0
ProgrammingDEV Community ·

Engineer Uses Azure Policy and Custom RBAC to Block Unauthorized Cloud VM Deployments

A DevSecOps engineer has detailed how they implemented automated guardrails on Microsoft Azure to prevent unexpected cloud cost spikes caused by human error. Using Azure Policy and custom RBAC least-privilege roles, they configured the Azure Resource Manager API to automatically intercept and deny any virtual machine deployment requests that fall outside a pre-approved list of low-cost B-Series SKUs. The policy was deployed via Azure CLI to a sandbox resource group in the Southeast Asia region, blocking higher-cost SKU families such as D-Series nodes at the point of request. To further tighten access controls, a custom VM Restart Operator role was created, restricting user permissions strictly to visibility and reboot actions while sealing off write, configuration, and deletion capabilities. The approach shifts cloud cost governance from reactive cleanup and policy handbooks to proactive, programmatic enforcement at the infrastructure level.

0
Crypto & Web3CoinDesk ·

Bitcoin Climbs Back Toward $78,000 for Third Consecutive Day of Gains

Bitcoin has extended its recovery for a third straight day, rising from an overnight low of $75,972 to just under $78,000. The rebound signals renewed buying momentum in the broader crypto market. Altcoin HYPE emerged as a standout performer, leading gains across the alternative cryptocurrency segment. The recovery comes amid broader market volatility that had previously pushed Bitcoin to lower price levels.

0
ProgrammingDEV Community ·

Audioproxy Gem Enables On-Demand Audio Transcoding in Rails Without Background Jobs

A Ruby gem called Audioproxy allows Rails developers to generate signed, cached audio preview URLs directly from Active Storage attachments without needing a job queue. The tool encodes format options, bitrate, and source URI into a signed URL path, with the first page load triggering transcoding and all subsequent requests served from a variant cache. It supports a range of processing options including trimming, fading, normalization, and expiry, all baked into the signed URL. Waveform peak data can also be generated as a format type, ensuring the visual waveform always matches the processed audio variant. The gem raises descriptive errors for unattached files or unknown options, reducing the risk of silent failures in production.

0
IndiaTimes of India ·

NC Girl, 12, Repairs 114 Stuffed Animals for Kids Displaced by Home Fires

A 12-year-old girl from North Carolina launched a personal initiative to help children who lost their homes in fires. She sourced discarded stuffed animals from local thrift stores, then cleaned and restored each one. In total, she repaired and donated 114 toys to affected children. The project provided emotional comfort to displaced kids while also promoting the value of recycling and reusing toys.

0
ProgrammingDEV Community ·

Developer traces HP laptop mute LED bug from Reddit hack to upstream kernel fix

A software developer discovered that the mute LED on their HP Omen 16-wd0xxx laptop failed to illuminate under Linux, despite audio muting correctly and the LED working normally on Windows. Initial investigation using evtest and /sys/class/leds/ ruled out hardware failure and pointed to a missing driver-level signal. A Reddit workaround involving direct hex writes to Realtek ALC245 codec registers resolved the symptom, but the developer found the approach unsatisfying for a problem likely already solved upstream. By cross-referencing the laptop's PCI subsystem ID against entries in the kernel's alc269.c quirk table, they identified and verified the correct fixup — ALC245_FIXUP_HP_MUTE_LED_V1_COEFBIT — through manual codec register testing. The fix was subsequently merged upstream and later proved useful in diagnosing the identical bug on a different user's laptop.

0
ProgrammingDEV Community ·

How Diffusion Models Turn Noise Back Into Data Using Reverse Learning

Diffusion models generate data by first defining a forward process that gradually corrupts real samples with Gaussian noise over many steps until only pure noise remains. This stepwise corruption simplifies the complex original data distribution into a manageable Gaussian endpoint, making it easier to work with mathematically. The model then learns a reverse diffusion process, training probabilistic transitions that move from noisy states back toward clean, structured data. During generation, the model starts from random Gaussian noise and repeatedly applies these learned reverse steps to produce realistic outputs. The key distinction is that while the forward corruption process is mathematically defined, the reverse generative process must be learned entirely from data.

← NewerPage 1 of 4384Older →