SShortSingh.
0
ProgrammingDEV Community ·

Critical MikroTik RouterOS Flaws Actively Exploited to Hijack Routers

Attackers are actively exploiting two critical vulnerabilities in MikroTik RouterOS, tracked as CVE-2026-67276 and CVE-2026-86060, to take full administrative control of internet-exposed routers. The attack chain first bypasses SSH authentication by exploiting incomplete RSA public key validation, requiring only the target username and public key modulus, then escalates privileges to full admin access via a crafted username. Once inside, attackers add administrative accounts and can alter DNS, VPN, routing, and firewall configurations, potentially enabling traffic interception and lateral movement into internal networks. CERT Polska published its advisory on September 5, 2026, warning that the absence of visible indicators does not confirm a device is clean. Administrators are urged to update RouterOS to versions 7.24.2, 7.23.4, 6.49.21, or later, restrict or disable exposed services, and fully rebuild any suspected compromised devices while rotating all credentials and keys.

0
TechnologyBBC Tech ·

Companies Begin Linking Employee Promotions to AI Tool Usage

A growing number of companies are making artificial intelligence adoption a factor in employee career advancement decisions. Workers who embrace and effectively use AI tools may find themselves on a faster track to promotion. This trend raises questions about fairness, particularly for employees who may lack access to or training in these tools. Critics argue that tying progression to AI use could disadvantage certain groups of workers. The debate reflects broader tensions as businesses push for AI integration across their workforces.

0
ProgrammingDEV Community ·

North Korean Hackers Embed Linux Backdoor Inside HAProxy to Spy on South Korea

A North Korea-linked threat actor, assessed with medium confidence, has deployed a Linux surveillance toolkit targeting South Korean sectors, according to a Rapid7 report published on September 4, 2026. The campaign uses a backdoor called 'ted' embedded directly inside HAProxy 2.8.12 as an internal filter, allowing attackers to intercept, tamper with, and exfiltrate web traffic while hiding activity from logs and counters. A second tool, curlRAT, provides persistent remote shell access and additional payload delivery under disguised process names, while an SSH keylogger harvests plaintext credentials from administrators. The attackers operate with root-level privileges on internet-facing Linux servers, replacing system binaries such as cron and OpenSSH and clearing logs to cover their tracks. Defenders are advised to verify binary integrity against known-good baselines, rely on independent network logs such as upstream proxies and TAPs, and rebuild compromised systems after preserving forensic evidence.

0
ProgrammingDEV Community ·

React 18 Quiz: How Stale Closures Inside Intervals Affect State Updates

A React 18 code snippet is being used to test developers' understanding of closure mechanics and state synchronization. The example features a Counter component that runs a setInterval inside a useEffect hook, calling setCount twice per tick using two different update patterns. One call uses the functional updater form while the other references a stale closure value, leading to a subtle but impactful bug. The scenario was encountered during a real architecture refactoring session involving a principal frontend engineer. Readers are challenged to predict the displayed value after three seconds before verifying their answer in CodeSandbox.

0
ProgrammingDEV Community ·

BigBear 2.0 AiTM Service Bypasses Microsoft 365 MFA by Stealing Session Cookies

CloudSEK researchers published findings on September 7, 2026, detailing BigBear 2.0, a high-severity Adversary-in-the-Middle phishing service targeting Microsoft 365 users. The service uses Evilginx2 to clone Microsoft login pages and injects JavaScript to disable WebAuthn and FIDO2 authentication, nudging victims toward weaker MFA methods like TOTP, SMS, or push notifications. Acting as a real-time proxy, it relays stolen credentials and MFA responses to legitimate Microsoft servers, then captures session cookies to maintain persistent unauthorized access. Attackers reuse these cookies via residential proxies to access emails, files, and accounts, and may follow up with inbox rule creation, OAuth consent abuse, or internal phishing. Organizations can defend against this threat by enforcing phishing-resistant MFA policies, applying device-based Conditional Access controls, and immediately revoking sessions and tokens upon detecting a compromise.

0
ProgrammingDEV Community ·

HTB Funnel: SSH Tunneling Used to Access Internal PostgreSQL Service

A Hack The Box challenge on a Linux machine exposed two open ports — FTP and SSH — with the FTP server permitting anonymous login. Files retrieved via FTP revealed a default password and a list of new employees, one of whom, Christine, had not changed her credentials, allowing SSH access. Once logged in, a locally running PostgreSQL service was discovered on port 5432 using the ss -tl command, but direct access was blocked as the psql client was not installed. SSH local port forwarding was then used to tunnel traffic from a local Kali machine port to the target's PostgreSQL port, bypassing the restriction. This tunneled connection allowed successful database access as Christine, ultimately yielding the challenge flag.

0
IndiaNDTV ·

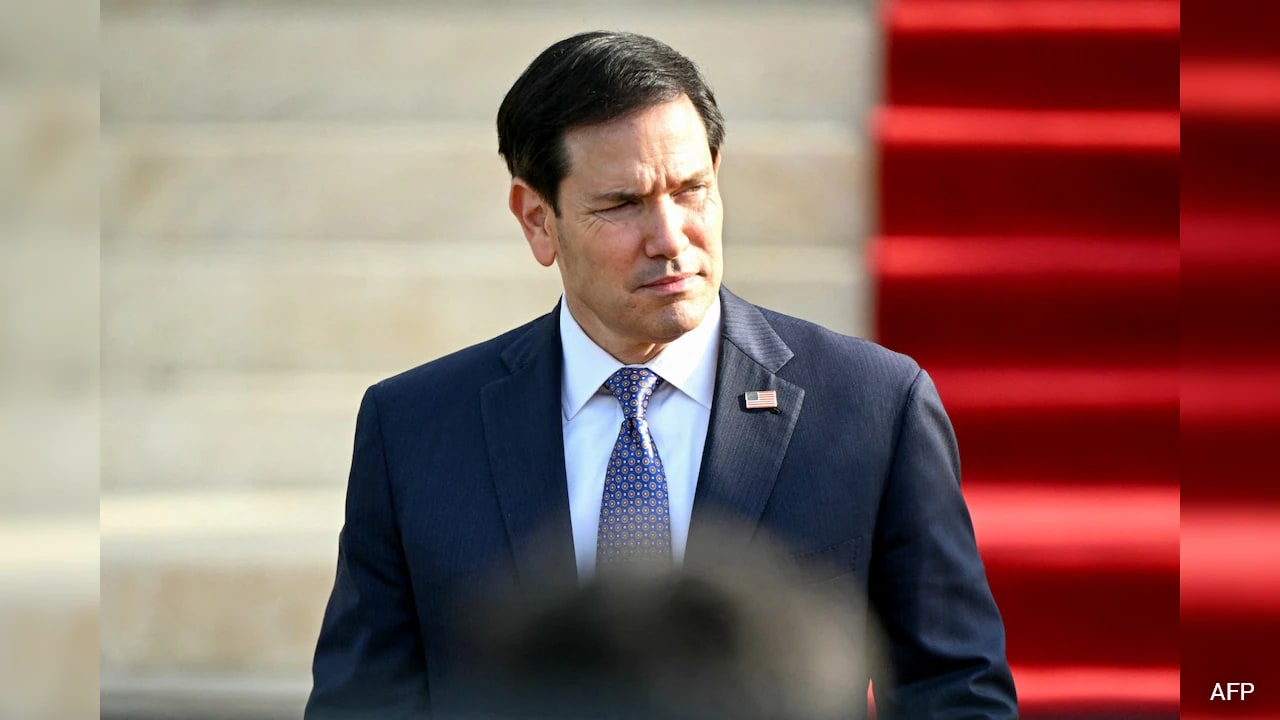
Rubio Vows Continued US Strikes on Iranian Tankers Amid Rising Tensions

US Secretary of State Marco Rubio announced on Tuesday that the United States will keep targeting Iranian tankers as part of retaliatory military action. The statement came as American authorities confirmed that five Iranian vessels had already been struck. Rubio's remarks signal a firm US stance as tensions between Washington and Tehran continue to escalate. The ongoing strikes represent a significant development in the broader confrontation between the two nations.

0
IndiaTimes of India ·

World's Longest 371-Day Cruise Departs Rome, Covering 62 Countries

A cruise ship named Regatta has departed from Rome on what is being called the world's longest cruise voyage. The journey will last 371 days, taking passengers across six continents and through 62 countries. During the trip, the ship is scheduled to dock at 220 ports worldwide, offering a comprehensive global itinerary. The cruise is marketed as a year-long adventure for travelers seeking an extended international experience.

0
ProgrammingDEV Community ·

XRP Ledger Batch Transactions Pass QA: 164 Tests Cover Atomic Multi-Step Flows

A QA test report dated September 8, 2026, documents results for Batch (XLS-56) Transactions on the XRP Ledger, prepared by sgramkumar in a GitLab CI environment running on xrpld devnet. The feature allows accounts to bundle up to eight inner transactions into a single atomic unit, eliminating the risk of partial completion that existed when transactions settled independently. Testing covered the BatchV1_1 amendment, which tightened BatchSigner authorization and signing semantics over the original Batch amendment. A total of 164 tests were executed across three categories: 106 core functional tests, 56 adversarial and security tests, and 2 cross-feature interaction tests involving Permission Delegation, Sponsored Fees, and Confidential MPT. All four execution modes — AllOrNothing, OnlyOne, UntilFailure, and Independent — along with multi-account signing, fee rules, and metadata reporting were validated against the XLS-56 specification.

0
ProgrammingDEV Community ·

Kestra 2.0 Launches With Rewritten Engine and Decoupled Worker Architecture

Workflow orchestration platform Kestra has released version 2.0, featuring a major rewrite of its core engine four years after its initial public introduction. The update splits the system into a control plane and a data plane, allowing workers to run anywhere — including on-premises, in separate cloud regions, or inside outbound-only networks — without requiring database credentials or inbound connections. Workers now communicate with the control plane via a single persistent gRPC stream, with support for TLS encryption and certificate or JWT-based authentication. The release also consolidates what were previously two separate engine implementations into one unified executor and scheduler, reducing duplicated maintenance overhead. Kestra 2.0 remains licensed under Apache 2.0, continuing the project's open-source commitment.

0
ProgrammingHacker News ·

Interactive Topological Picture Book Brings Abstract Math to Life Online

A digital project titled 'A Topological Picture Book, Rendered' has been published at e-infinity.space. The work appears to be an online visual rendering inspired by geometric and topological concepts. It was shared on Hacker News, where it received early attention from the community. The project offers an accessible, visual approach to exploring complex mathematical ideas. Limited discussion has taken place so far, suggesting it is a newly surfaced resource.

0
ProgrammingDEV Community ·

How to Deploy Your AI-Built App: A Practical Guide for First-Time Builders

Developers who build apps using AI assistants often hit a wall when trying to share their work beyond a local environment, because deployment involves infrastructure decisions that code generation tools do not handle. The article distinguishes between static front-end apps, which can be hosted for free on platforms like Vercel, Netlify, or Cloudflare Pages within minutes, and backend apps, which are better served by managed platforms like Railway, Render, or Fly before considering a dedicated server. A self-managed server is recommended only when platform costs exceed a basic VPS, or when persistent storage, background jobs, or data residency requirements arise. AI-generated code commonly embeds API keys directly in source files and relies on local file storage, both of which cause serious problems in production environments — including security breaches and data loss on redeployment. Developers are advised to use environment variables for secrets, managed databases instead of SQLite, and object storage services like Cloudflare R2 or Amazon S3 for user-uploaded files.

0
ProgrammingDEV Community ·

JavaScript Promises: A Cleaner Fix for Callback Hell in Async Code

Asynchronous JavaScript is commonly handled using callbacks, but deeply nested callbacks — known as callback hell or the Pyramid of Doom — make code hard to read, debug, and maintain. JavaScript Promises offer a cleaner alternative by representing the eventual result of an asynchronous operation through three states: pending, fulfilled, or rejected. Once a Promise settles into either fulfilled or rejected, its state cannot change again. Developers use .then() to handle successful results, .catch() to manage errors, and .finally() to run code regardless of outcome. Promise chaining allows multiple asynchronous steps to be written sequentially, significantly improving code readability and error handling compared to nested callbacks.

0
ProgrammingDEV Community ·

.NET 10 Changes Shift Behavior for Small Integer Types in Generic Math

Microsoft's .NET 10 has altered how oversized bit-shift operations behave for small integer types like byte and short when dispatched through generic math interfaces such as IShiftOperators. Unlike concrete C# expressions that promote operands to int, generic methods constrained by IShiftOperators return the original type T, meaning shift counts equal to or exceeding the type's bit width now produce different results than in .NET 9. Developers maintaining libraries that target multiple runtimes should add cross-runtime tests covering shift counts at and beyond the type width to catch behavioral differences. Two mitigation strategies are available: rejecting out-of-range counts via ArgumentOutOfRangeException for inputs like parsers or authorization bitsets, or applying a modulo operation on the count where wrapping behavior is an intentional part of the contract. Microsoft recommends keeping cross-runtime assertions in place until all affected older runtime targets reach end of support.

← NewerPage 907 of 4769Older →