SShortSingh.
0
ProgrammingDEV Community ·

PII Guardrail Studio Offers Local Privacy Gateway for LLMs Under 25ms

PII Guardrail Studio is a local, air-gapped privacy gateway designed to strip and restore personally identifiable information before and after calls to external LLM APIs like OpenAI or Claude. The tool intercepts sensitive data such as names, SSNs, and dates of birth, replacing them with tokens that are only restored locally after the model responds. All PII mappings are stored in an AES-256 encrypted SQLCipher database, secured with SHA-256 digests and Ed25519 node-locking, making the data unreadable without the local node key. The gateway can be deployed via a PyPI package or Docker container and integrates with existing Python pipelines using standard HTTP libraries. To mark its v2.0 release, the developers are offering a free six-month enterprise evaluation key valid through March 2027, unlocking unlimited throughput and over 30 entity recognizers.
0
IndiaTimes of India ·

Allahabad HC: Creating email ID in another's name may not be identity theft

The Allahabad High Court has stayed an FIR filed against two individuals accused of creating an email account using another person's name. The court questioned whether such an act qualifies as identity theft under the Information Technology Act. It observed that the relevant provision of the IT Act specifically refers to electronic signatures and passwords, with no explicit mention of email IDs. The FIR has been put on hold pending further judicial review and orders from the court.

0
ProgrammingDEV Community ·

MCP Protocol Drops Sessions in July 2026 Update, Raising Prompt Injection Risks

The July 28, 2026 revision of the Model Context Protocol eliminates the initialize handshake, Mcp-Session-Id header, and server-side session state, making every request fully stateless. The change allows MCP servers to run behind standard load balancers without sticky sessions or shared session stores, simplifying scaling significantly. In place of session-based continuity, the spec introduces explicit handles — strings the model carries in its context window and passes as arguments on subsequent calls. However, security concerns have emerged because these handles are ordinary strings that can be read, copied, or injected by anyone able to plant text the model trusts, effectively turning a planted prompt into a stolen credential. Server authors are advised to implement per-request validation checks, as the assumption that credentials are tied to transport-level session metadata no longer holds under the new spec.

0
IndiaNDTV ·

MCD Seals Adjacent Building After Delhi Structure Collapse

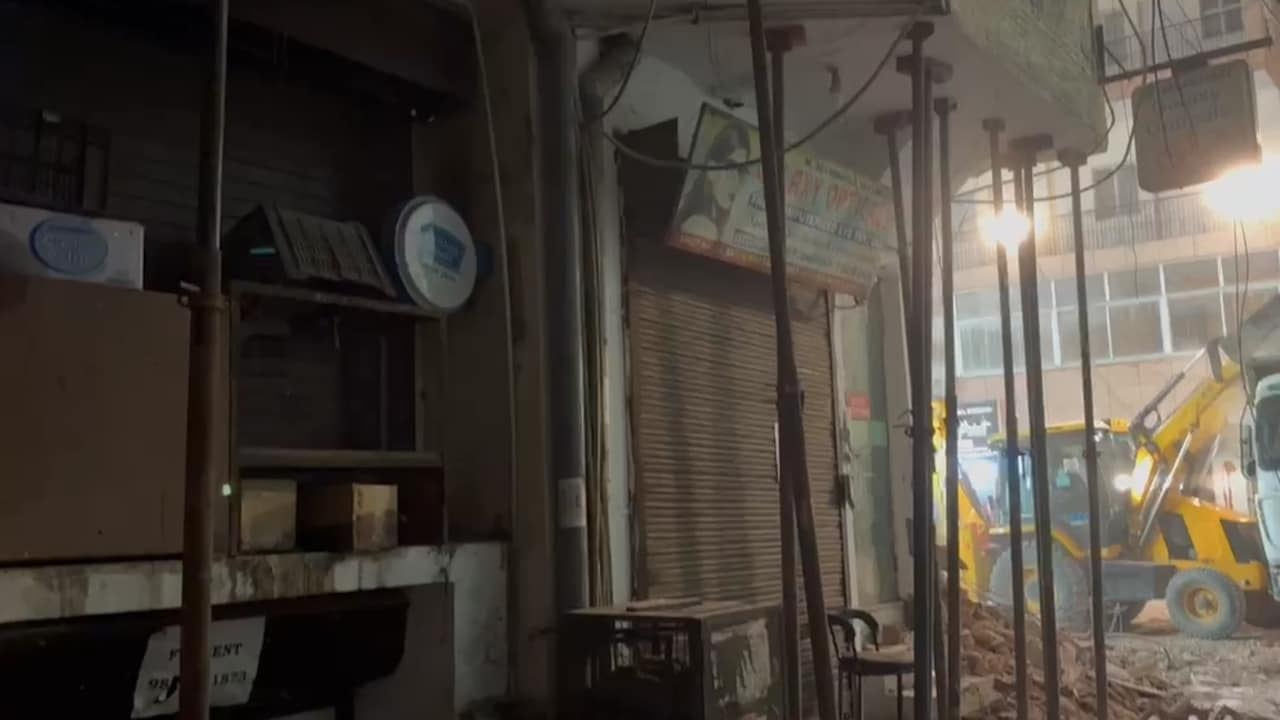
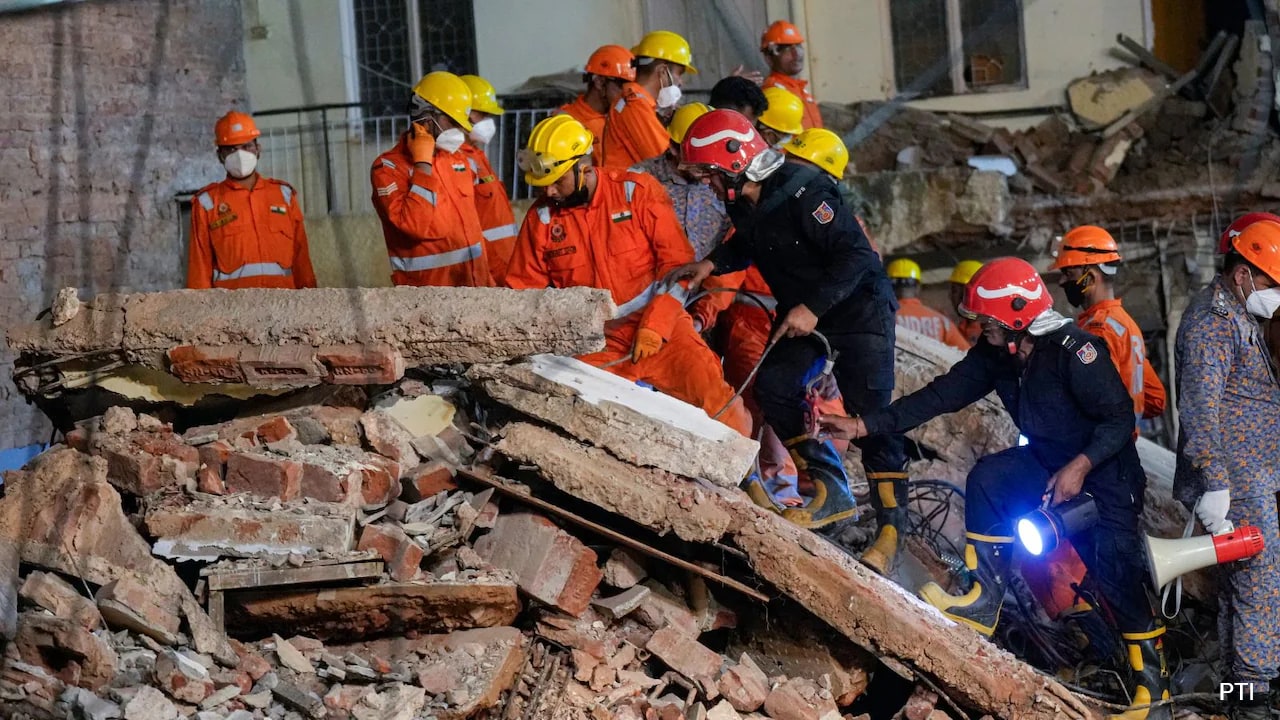
Following a building collapse in Delhi, the Municipal Corporation of Delhi (MCD) has taken swift preventive action on a neighbouring structure. The adjoining building, which housed a girls' paying guest accommodation, has been fully evacuated by authorities. Officials confirmed that all tenants were removed from the premises before it was sealed. The move aims to prevent any further risk to residents in the vicinity of the collapsed structure.

0
ProgrammingDEV Community ·

Two Critical CVSS 9.8 Flaws Found in AI Agent Sandboxes Cua and AutoAgent

Two critical vulnerabilities, CVE-2026-86121 and CVE-2026-86124, were publicly disclosed on September 5 by the same security researcher, targeting the open-source AI agent tools Cua and AutoAgent respectively. Both flaws stem from sandbox servers that bind to all network interfaces by default while skipping authentication, allowing any network-reachable attacker to execute arbitrary shell commands without credentials. In Cua, the conflict between its local-mode auth bypass and its default 0.0.0.0 bind address exposed a shell execution endpoint, file read/write access, and an interactive PTY on TCP port 8000. Cua has already merged a fix in version 0.3.42, changing the default bind address to 127.0.0.1 and requiring an explicit opt-in for insecure exposure. AutoAgent's vulnerability remains unpatched as of the disclosure date, with its Docker setup running containers as root and mounting host directories, meaning a remote attacker could gain root-level access to real files on the host machine.

0
IndiaNDTV ·

Delhi Building Collapse: Nearby Structure Raises Safety Fears as Rescue Ops Continue

Rescue operations are ongoing at the site of a collapsed paying guest accommodation in Delhi, where workers are digging through rubble to find survivors. Authorities have now turned their attention to an adjacent building, which is causing concern over its structural stability. Officials are working to install a support system to stabilise the neighbouring structure and prevent further danger. The situation remains active as emergency teams manage both the rescue effort and the potential risk posed by the at-risk building.

0
ProgrammingDEV Community ·

Cursor Terminal Allowlist Bypass Lets Malicious Project Files Hijack AI Commands

A vulnerability tracked as CVE-2026-22708 affects Cursor's terminal allowlist, allowing a maliciously named file in a project directory to intercept and replace trusted shell commands. The flaw stems from the allowlist checking only the command name rather than the binary the shell actually executes, meaning a local script named 'curl' can run instead of the system binary. AI coding agents are particularly at risk because they frequently execute shell commands inside directories they did not create. A developer has extended an open-source defensive toolkit, secops-toolkit-mcp, with a static analysis check that flags relative command names vulnerable to this path-shadowing pattern. The check cannot catch all edge cases through static analysis alone, but it correctly identifies the core CVE-2026-22708 exploit pattern and recommends using absolute binary paths as a mitigation.

0
ProgrammingDEV Community ·

Key Security and Safety Checks Teams Should Run Before Releasing an AI Agent

Before deploying an AI agent to production, development teams must define which failure types should block a release entirely. Critical red lines include the agent accessing records belonging to other customers, following unauthorized instructions embedded in retrieved documents, or performing actions like issuing refunds without required approvals. Testing should cover the full connected workflow using controlled data, verifying both the agent's response and actual backend outcomes to catch silent failures. Any critical action that cannot be verified should be flagged for manual review, with evidence retained and failed cases retested in subsequent builds. This structured approach forms the basis of a release checkpoint framework aimed at helping teams make confident approve, block, or review decisions for AI agent deployments.

0
ProgrammingDEV Community ·

Developer builds BandwidthGuard to catch bloated API payloads AI agents generate

A developer noticed that AI coding assistants like Cursor and Claude were generating API endpoints that returned far more data than frontend clients actually needed. Despite responses appearing small after Gzip compression, the underlying JSON payloads contained unused fields, repeated objects, and unnecessary whitespace — with one sample scoring only 52/100 and carrying roughly 54% optional bytes. To address this, the developer built BandwidthGuard, a free browser-based tool that analyzes JSON payloads, HAR files, or cURL output without uploading any data. The tool scores payload efficiency, breaks down fields by necessity, compares compression formats, and categorizes suggested fixes as either safe or contract-changing. It also provides ready-made prompts for popular AI coding tools so developers can ask the same agent that wrote the endpoint to review and slim its own output.

0
IndiaNDTV ·

Singapore PM Condemns Xenophobic Online Attacks Targeting Indian Community

Singapore has launched an investigation into a wave of xenophobic remarks directed at Indians circulating online. Prime Minister Lawrence Wong publicly condemned the abuse, calling it shameful and unacceptable. He stressed that Singapore must never allow prejudice against any community to become normalised. The incident has sparked a broader national conversation about tolerance and social cohesion in the multicultural city-state.

0
IndiaNDTV ·

Managing Irregular Income: Key Financial Tips for Freelancers

Freelancers and independent contractors face unique financial challenges due to the absence of a fixed monthly income. Unlike salaried employees, they do not receive benefits such as paid leave, social security contributions, or employer-provided health insurance. This unpredictability makes budgeting and financial planning significantly more complex for self-employed individuals. Without a structured payday, freelancers must develop their own strategies to manage cash flow and build financial security. Proactive planning and disciplined saving are considered essential tools for navigating the uncertainties of freelance work.

0
IndiaTimes of India ·

Temu Spent $962M on Meta Ads in Europe Amid Fake Influencer Concerns

Chinese e-commerce giant Temu has allegedly spent close to one billion dollars on Meta advertising across Europe. Research suggests that a significant number of influencer accounts promoting Temu's products may be fake, with one account named Ya Lili being a notable example. The findings have raised serious concerns about advertising ethics and regulatory compliance in the region. The matter has drawn the attention of the EU's Digital Services Act regulator, which has launched an assessment into the platform's practices.

0
ProgrammingHacker News ·

Trail of Bits Releases Coop: Isolated VM Tool for AI Coding Agents

Trail of Bits has open-sourced a tool called Coop, designed to run AI coding agents like Claude Code and OpenAI Codex inside isolated virtual machine environments. The project is hosted on GitHub and aims to provide a safer execution context for AI-driven code generation and automation. Isolated environments help contain potential risks associated with running autonomous AI agents that can execute code. The release has garnered early attention on Hacker News, reflecting growing developer interest in secure AI agent infrastructure.

0
ProgrammingDEV Community ·

How AI Agents Help Engineers Recover Hidden Logic in SAP-to-Cloud Migrations

Migrating data from SAP to cloud platforms is technically straightforward, but preserving the business knowledge embedded in legacy systems — such as join logic, status mappings, and ownership — is far more complex. A synthetic case study involving over 5,000 SAP HANA calculation views, thousands of cloud tables, and parallel BI tools like Qlik and Spotfire illustrates the scale of this challenge. To address it, engineers have designed an Enterprise Data Discovery Assistant built on a bounded Snowflake Cortex Agent that queries four evidence layers: HANA repository code, BI artifacts, a reporting metadata catalog, and schema and lineage metadata. The assistant is read-only and does not modify source systems; instead, it surfaces recovered logic, ownership details, and dependencies to help engineers draft grounded SQL for validation. This approach reframes migration as an evidence-discovery problem rather than a pure code-conversion task.

0
ProgrammingDEV Community ·

NeedFeed Launches Hyperlocal In-Kind Aid Platform to Replace Cash Charity

NeedFeed is a new mutual aid platform designed to connect neighbors through physical donations — such as food, clothing, and medical supplies — without involving cash transactions. The platform addresses three common failures in charity tech: cash diversion, involuntary public tagging of vulnerable people, and unverified generosity badges. Instead of tagging individuals in need, NeedFeed uses a steward system where a representative posts on a beneficiary's behalf only after recording verbal consent. Donations are verified through a two-party handoff process, meaning trust badges are earned through confirmed real-world exchanges rather than self-reporting. Built with Google Gemini AI and Snowflake integrations, the open-source project was submitted to the DEV Community Weekend Challenge: Generosity Edition.

0
ProgrammingDEV Community ·

Developer finds 93% of fully-signed Safe multisig transactions are permanently unexecutable

A developer building an automated executor for Safe multisig transactions ran a read-only detector against 1,299 Base mainnet Safes before writing any code, scanning blocks from Base's early history through block 50,776,046. The scan identified 366 fully-signed but unexecuted transactions, yet 339 of them turned out to be permanently dead — roughly 93% of the total. The root cause is that Safe executes nonces strictly in order, so if a different transaction consumes a given nonce, the original remains in the queue indefinitely with no indication it can never run. The naive one-line detector missed this entirely because it never compared queued nonces against the Safe's live on-chain nonce, a gap only exposed by an additional RPC call. This finding shifted the project's focus: instead of an execution engine, the core product became a structured refusal system that explains precisely why a transaction cannot or should not be submitted.

0
WorldBBC World ·

AfD's Historic Regional Gains in Germany Rattle EU and Mainstream Parties

Germany's far-right Alternative für Deutschland (AfD) has secured significant gains in regional elections, marking a historic milestone for the party. The results in Saxony-Anhalt have sent shockwaves beyond Germany's borders, drawing concern from European Union officials and established political parties. BBC Europe editor Katya Adler notes the outcome is being viewed as a serious warning signal across the continent. The rise of the AfD reflects growing support for far-right politics in a key EU member state, raising questions about the broader direction of European politics.

← NewerPage 837 of 4600Older →