SShortSingh.
0
ProgrammingDEV Community ·

Domain Watchlists, WHOIS Checks, and Drop-Catchers Serve Three Different Needs

Many domain hunters use the wrong tool because they conflate three distinct tasks: one-off lookups, ongoing availability monitoring, and competitive drop-catching at deletion. A simple RDAP or WHOIS check answers whether a domain is registered right now, but manually repeating that check over weeks is not reliable monitoring. A watchlist service automates scheduled checks and sends alerts when a domain's status changes, but does not compete at the registry level to secure the name. Drop-catching platforms are built for high-stakes races on expiring domains and often charge fees regardless of whether the user wins. Matching the right tool to the right goal can save founders and investors from wasted backorder fees or missed opportunities.
0
ProgrammingHacker News ·

MathKernel: Open-Source Multi-Engine Math Kernel with MCP Server Support

MathKernel is a newly released open-source mathematics kernel that combines multiple computational engines with evidence-aware processing. The project, hosted on GitHub under the repository Staatsgeheim/MathKernel, also functions as a Model Context Protocol (MCP) server. It appears designed to handle mathematical computations while tracking or citing the reasoning behind results. The release was shared on Hacker News, where it received minimal early engagement with five points and no comments.

0
IndiaTimes of India ·

Imran Khan's sons accuse Pakistan authorities of endangering his life in prison

The sons of former Pakistan Prime Minister Imran Khan, Sulaiman and Kasim Khan, have raised serious concerns about their father's health and treatment in custody. The brothers also strongly criticised PCB chairman Mohsin Naqvi following allegations that the board threatened to pull out of the ongoing Lord's Test against England. The sons claimed Pakistani authorities are deliberately trying to silence Imran Khan through his prison conditions. Their statements come amid heightened tensions surrounding both the cricket series and the imprisoned former leader's wellbeing.

0
ProgrammingDEV Community ·

Why Developers Are Choosing TypeScript Over JavaScript for Large Codebases

TypeScript is increasingly preferred over JavaScript for larger projects because it catches type-related errors during development rather than at runtime. By allowing developers to explicitly define variable types, function parameters, and data structures, TypeScript reduces the risk of unexpected values causing bugs in complex applications. It also significantly improves editor support, offering more reliable autocomplete and making it easier to navigate large codebases without memorizing every object structure. Refactoring becomes safer too, as the TypeScript compiler flags all references to renamed or restructured properties across a project. That said, TypeScript compiles down to plain JavaScript for browsers, meaning it adds a development-time layer rather than a new runtime — and for very small scripts, plain JavaScript often remains the more practical choice.

0
ProgrammingDEV Community ·

Client-Side Validation Improves UX But Cannot Replace Server-Side Security

Client-side validation in browsers enhances user experience by providing instant feedback, but it cannot be considered a security control since users can bypass it using tools like curl, Postman, or browser developer tools. Every piece of incoming data — including form fields, cookies, headers, and API payloads — must be independently validated on the server, which should treat all client input as untrusted by default. Developers are advised to use strict allow-list validation where possible, as it is more reliable than attempting to sanitize arbitrary input after the fact. Server-side validation also works alongside other security measures such as parameterized queries, output encoding, authentication, and rate limiting, none of which can be replaced by it alone. The core principle is straightforward: client-side validation protects usability, while server-side validation protects the application.

0
SportsESPNcricinfo ·

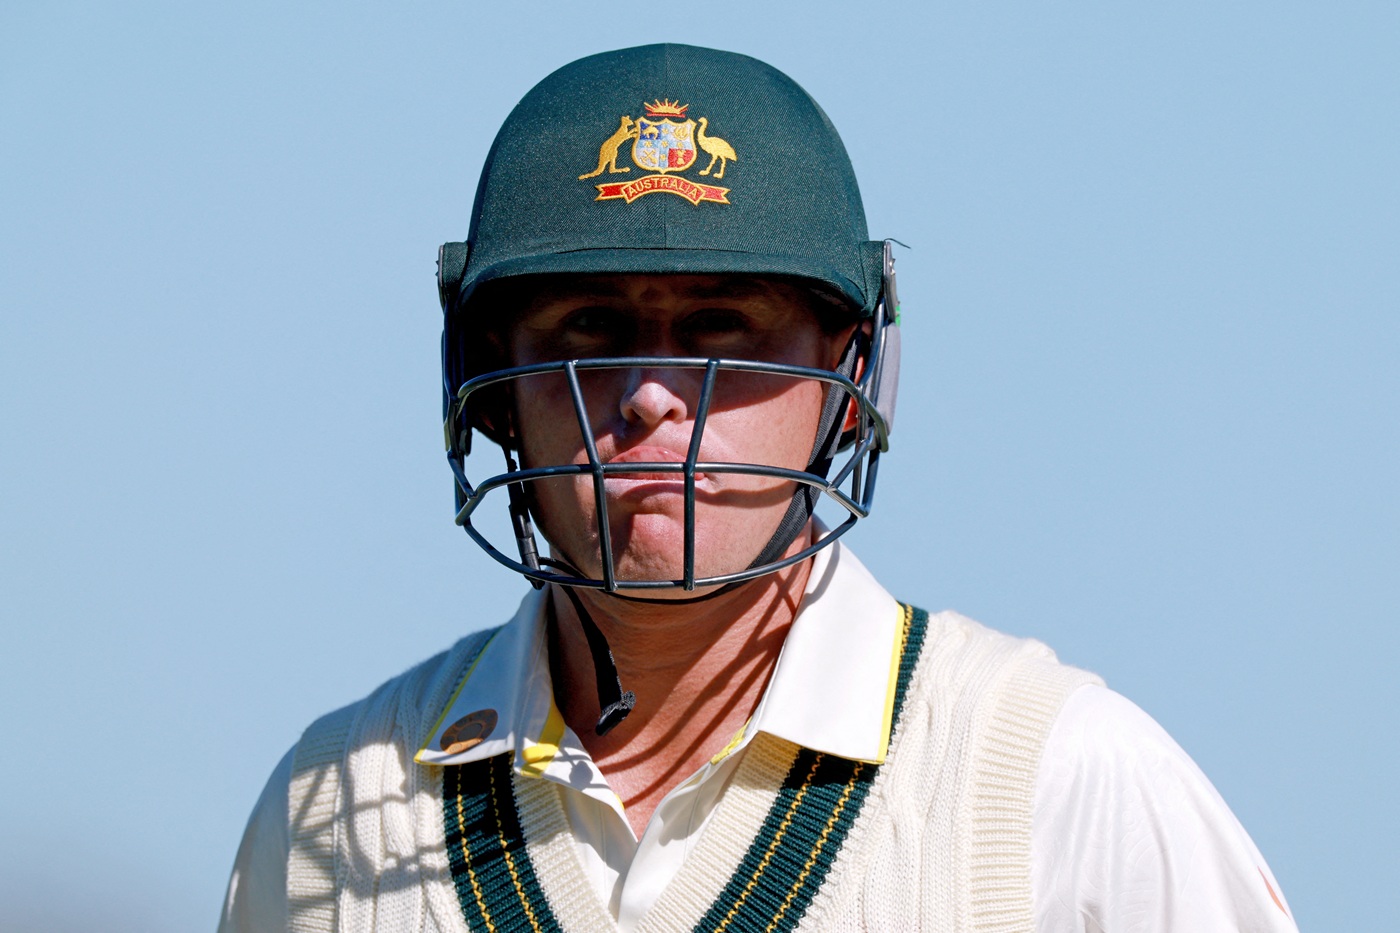
Australia retain Labuschagne, add Connolly for South Africa Test series

Australian selectors have named their squad for the upcoming three-Test series against South Africa, retaining Marnus Labuschagne despite his prolonged poor run of form. The decision reflects continued faith from selectors in the experienced batter, who has struggled to find consistency in recent times. Spinner Matthew Kuhnemann and all-rounder Michael Neser have also earned places in the squad. Pacer Xavier Connolly receives a call-up, marking a notable inclusion in the Test setup for the series.

0
ProgrammingDEV Community ·

MIT-Licensed F.I.N.E. Framework Turns Raw Emotional Text Into Structured Outputs

F.I.N.E. (Framework for Interpreting Nonliteral Expression) is an open-source, MIT-licensed tool published on GitHub by The Fort That Holds. It accepts unstructured emotional input from users and processes it through four internal passes — LOOK IN, SPIRAL UP, FLOW OUT, and RETURN — to generate useful artifacts such as poems, prose, songs, or boundary-conversation scripts. Unlike a chatbot, the tool does not ask follow-up questions; it takes a single input and produces a structured output based on 32 emotional voice families defined in plain JSON. The framework supports both OpenAI and local language models such as Ollama or LM Studio via configurable environment variables. The complete tool is available at the project's GitHub repository, with no additional paid components required.

0
ProgrammingDEV Community ·

Chrome DevTools Protocol sessions share active tab, causing automation jobs to read wrong pages

A developer discovered that multiple scheduled automation jobs sharing a single Chrome instance via the DevTools Protocol can silently read each other's pages without any errors or exceptions. The root cause is that named client sessions do not correspond to specific browser tabs — instead, every read targets whichever tab is currently active in the browser. When two jobs overlap, the last one to navigate claims the active tab for all sessions, causing other jobs to receive valid but incorrect page data. Two fixes exist: each job must explicitly re-assert its target tab before every command, or jobs must acquire an exclusive lock on the debugging port to prevent concurrent browser access. Both approaches have trade-offs, as the re-assertion method requires discipline across every command, while serialisation introduces idle wait time and lock-recovery complexity.

0
ProgrammingDEV Community ·

Fort Card lets developers issue scoped, capped API credentials instead of raw keys

Fort Card is an open-source tool that applies a credit-card-like model to API key management, addressing the security risk of sharing unrestricted API keys with AI agents. Instead of exposing a master key, the system stores it inside a Cloudflare Worker called a lockbox, which is the only component that ever handles the plaintext credential. Agents receive a 'card' that is restricted to a specific host, limited to a set number of uses, and can be frozen instantly if needed. When an agent makes a request, the lockbox injects the real key server-side and returns only the response, so the agent never sees the underlying credential. The project is released under the MIT license and can be self-hosted via GitHub, with an optional hosted version available at $8 per month.

0
WorldBBC World ·

Austria enforces Islamic headscarf ban for girls under 14 in schools

Austria has introduced a law banning girls under the age of 14 from wearing Islamic headscarves in schools, which came into effect as the new school term began. The government argues the measure is designed to protect the rights and freedoms of young girls. However, critics and Muslim communities have pushed back against the legislation, warning it is stoking anti-Muslim sentiment in the country. The ban has sparked a broader debate about religious freedom, integration, and discrimination in Austria.

0
ProgrammingDEV Community ·

SQL Query Across 2.9M Charity Pairs Exposes Limits of Spelling-Based Name Matching

Researchers at tamiz.pro ran a vector similarity analysis across 2,889,151 pairwise combinations drawn from a registry of roughly 1,700 charitable organizations to compare spelling-based and meaning-based matching methods. Traditional fuzzy matching tools like Levenshtein distance and Jaro-Winkler scoring measure character-level differences between strings, but fail to detect when two differently spelled names refer to the same entity. By contrast, sentence-transformer embeddings — specifically the all-MiniLM-L6-v2 model — placed semantically related charity names in the same region of vector space regardless of how different they looked in text. For example, 'Doctors Without Borders' and 'Médecins Sans Frontières' scored low on lexical similarity yet ranked as near-identical in semantic space. The experiment highlights a fundamental gap between edit-distance algorithms and embedding-based approaches when matching real-world organization names across languages and jurisdictions.

0
ProgrammingDEV Community ·

Developer Builds Stop Hook to Skip Audit Nags During Unattended Claude Code Sessions

A developer using Claude Code's autonomous setup discovered that audit notification hooks designed for interactive sessions were also firing during unattended automated runs, generating 19 stacked error logs overnight on July 12, 2026. The Stop hook — a shell script that checks whether Claude performed a self-audit after modifying files — was blocking CLI runs launched via launchd with an exit 2 error, degrading pipeline execution. The root cause was that Claude Code uses a single Stop hook primitive for both human-facing and machine-facing sessions, with no built-in distinction between the two contexts. The developer identified that the session transcript file contains an 'entrypoint' field — 'cli' for interactive use and 'sdk-cli' for Agent SDK runs — which the hook itself can read to determine whether a human is present. By parsing this field from the transcript at runtime, the hook can silently skip audit nags during unattended automation while still enforcing them in interactive sessions.

0
ProgrammingHacker News ·

Hard-Chat: Open-Source Serverless P2P Terminal Chat That Runs Entirely in RAM

Hard-Chat is a newly released open-source project hosted on GitHub by developer mrhardlint. It is a peer-to-peer terminal-based chat application that operates without any central server. The tool runs exclusively in RAM, meaning no data is written to disk during use, which enhances privacy. The project was shared on Hacker News, where it received modest early attention with 8 points and one comment.

0
ProgrammingDEV Community ·

Dev Builds App That Turns Acts of Generosity Into Shareable Digital Receipts

A developer has built 'Proof of Good,' a web app that documents charitable acts by letting users describe what they gave, who benefited, and attach supporting evidence like photos or receipts. The app uses Google Gemini to assess submitted evidence through structured AI analysis, deliberately avoiding language that implies verified truth. Each documented act can be permanently recorded as a memo on the Solana Devnet blockchain, creating a publicly checkable record. ElevenLabs text-to-speech integration converts the proof into a short spoken narration, making the record feel more personal. The project was submitted to a DEV Community weekend hackathon and is built using Next.js, TypeScript, and Tailwind CSS.

← NewerPage 830 of 4586Older →