SShortSingh.
0
ProgrammingDEV Community ·

Engineer Warns Multi-Cloud Strategy Cost More Than the Risk It Prevented

A software engineer at a tech company reflects on a decision to adopt a multi-cloud infrastructure across two providers, driven by concerns over vendor dependency and contract leverage. Over two years, the strategy proved more costly and operationally complex than anticipated, without the feared provider-wide outage ever occurring. Because maintaining true workload portability required avoiding each platform's best managed services, the team effectively paid cloud prices while rebuilding data-centre-level infrastructure themselves. The human toll was significant — on-call procedures, hiring, and team expertise all suffered as engineers were spread thin across two platforms instead of deeply skilled in one. The author now advocates a more targeted approach: keep data portable, use infrastructure-as-code, and address only the specific risks that genuinely threaten the business.

0
ProgrammingDEV Community ·

Visual diff tools aim to fix AI coding agents' blind spot on UI regressions

AI coding agents excel at fixing backend bugs using test failures and error logs, but lack the ability to visually verify UI changes they make, often shipping broken layouts undetected. Unlike code errors, visual regressions such as shifted buttons, reflowed cards, or missing shadows rarely trigger automated test failures, leaving agents to self-report UI changes as correct without any visual confirmation. A proposed solution involves capturing cloud-rendered screenshots on every pull request, diffing them against a baseline, and posting cropped before-and-after comparisons directly in the PR where agents already check for failures. An AI judge pre-labels each visual change as either an intentional restyle or an unintended regression, allowing the agent to review only the relevant pixel-level crops rather than full-page screenshots. Using a set of MCP-connected tools, the agent can then list affected UI stories, inspect diffs, fix regressions, and approve intended changes, completing the visual review loop without manual intervention.

0
ProgrammingDEV Community ·

Two-Year Deployment Mindset on a StatefulSet Cost a Team a Morning of Data Recovery

A engineering team ran a three-node message broker as a Kubernetes StatefulSet for two years while applying Deployment-style operational habits, including overnight scale-downs to cut costs. The incident occurred when an automated scale-down raced with a node replacement, causing a pod to return with an empty volume after its PVC was reclaimed under an unreviewed policy. This left two broker members with conflicting partition ownership, requiring hours of manual data reconciliation. The team resolved the issue by removing scale-down automation, setting reclaim policy to Retain, using the broker's own admin commands for member removal, and configuring rolling updates with a readiness probe that verifies cluster membership. The key takeaway was that StatefulSet pods carry distinct identities and roles, meaning orchestration for stateful workloads must follow the application's own lifecycle rather than generic container management patterns.

0
IndiaTimes of India ·

Elon Musk Clashes With Chess.com Again Over Whether Chess Can Be Solved

Elon Musk engaged in a public back-and-forth with Chess.com after claiming that chess will eventually be fully solved. The platform pushed back, arguing that the number of possible chess positions exceeds the count of atoms in the observable universe. Musk disputed the comparison, calling it idiotic, and dismissed the account's administrator as an intern. The admin responded by correcting him. This is not the first such clash — Chess.com previously questioned Musk's chess-playing ability in 2022.

0
IndiaTimes of India ·

Ex-Pakistan captain Rashid Latif accuses PCB of remote-control team management

Former Pakistan cricket captain Rashid Latif has launched a sharp criticism against the Pakistan Cricket Board over its handling of the national team. Latif accused the PCB of managing the team through remote control, raising doubts about the board's decision-making process. Mid-series changes to players and coaching staff have drawn widespread backlash from cricket circles. The controversy comes at a difficult time as Pakistan's Test team struggles in the World Test Championship standings. The situation has fuelled speculation about further player changes, with some questioning whether Babar Azam could be the next target.

0
ProgrammingDEV Community ·

Why AI Agents Succeed in Demos but Break Down in Production

AI agents that perform flawlessly in demos frequently fail in real-world deployments, not due to model limitations but because of missing engineering safeguards. Common failure modes include overprivileged tool access, absent evaluation frameworks, uncontrolled retries, and no clear recovery path when things go wrong. Unlike demo environments with clean data and cooperative users, production systems expose agents to malformed inputs, API timeouts, and even malicious instructions. A support agent given broad CRM access during testing, for example, may autonomously issue refunds, close unrelated tickets, and contact customers in error. Experts argue that AI agents must be engineered like distributed systems, with strict permission boundaries, idempotent operations, and defined failure ownership, before they are considered production-ready.

0
ProgrammingDEV Community ·

How a Two-Week Security Exception Quietly Survived for Three Years

A software team approved a temporary security exception — including shared credentials and relaxed firewall rules — to meet a supplier integration deadline, with a documented two-week expiry. Three years later, the exception was discovered still active, with no one able to explain its origin, as the staff who requested and approved it had since moved on or left. The incident revealed a systemic flaw: the organisation had a formal process for granting security exceptions but no mechanism to enforce their removal. An audit found that years of deadline-driven workarounds had created an unknown number of similar deviations, making the real security posture significantly weaker than policy suggested. The team responded by building expiry enforcement directly into technical systems and instituting a mandatory quarterly review where every open exception must be verbally justified by name.

0
ProgrammingDEV Community ·

How a Hidden Database Deletion in Terraform Plan Led to Safer Deployment Practices

A Terraform plan described as a routine tag update concealed a managed database replacement buried 210 lines deep, which a team narrowly avoided executing by accident. The destructive change originated from a subnet group attribute modified in a shared module three weeks earlier, never reviewed against this specific environment. The incident exposed how Terraform's verbose plan output makes it easy for humans to miss critical destroy or replace operations, especially under low-alert conditions. In response, the team introduced automated policy checks that block any destroy or replace of protected resources and require a separately labelled change with a second approver. They also restructured pipeline output to surface counts of additions, changes, and deletions at the top, ensuring dangerous operations are immediately visible rather than buried in noise.

0
ProgrammingDEV Community ·

Engineering Team Replaced 3 Microservices and 4,100 Lines of Code With One Postgres Table

A software team eliminated three separate microservices — a notification service, a scheduler, and a retry handler — totaling over 4,100 lines of code, replacing them with a single 41-line Postgres table and a 560-line worker. The services were well-built but had been architected around an unnecessary boundary, as all three ultimately existed to move data from one state to another at a scheduled time. The original setup relied on RabbitMQ queues and Redis, introducing a classic distributed systems risk known as the transactional outbox problem, where a failure between a database write and a queue publish could silently drop events. By storing jobs directly in the database alongside application data, the team ensured all state changes remain in a single transaction, eliminating drift between systems. The refactor reduced operational overhead — including separate deployments, dashboards, and on-call runbooks — while retaining scheduling, retry, and delivery logic through simple SQL columns and queries.

0
ProgrammingDEV Community ·

Why AI Apps Need Learning Systems, Not Just Smarter LLM Wrappers

A developer building an AI application with a focus on quality, robustness, and cost-efficiency began questioning whether wrapping an LLM with tools and prompts truly makes a system intelligent. The author argues that most AI applications, even sophisticated ones using RAG and vector databases, simply re-execute predefined workflows without genuinely learning from past outcomes. The key distinction drawn is between prompt-driven behaviour, where instructions define every action, and a learning system, where a policy improves over time based on feedback and observed results. The piece also differentiates fine-tuning, which adapts a model using domain-specific examples, from reinforcement learning, which optimises decisions through reward signals and policy updates. The author concludes that treating the LLM as one component within a broader decision-making system, rather than as the sole intelligence, opens the door to more adaptive and cost-effective AI applications.

0
ProgrammingDEV Community ·

Claude Accounts Hijacked via Infostealer Malware That Bypassed 2FA

Anthropic has confirmed that multiple Claude user accounts were compromised through infostealer malware installed on users' own devices, not through a breach of Anthropic's systems. Malware variants including Vidar, LummaC2, and Atomic Stealer stole active browser session cookies, allowing attackers to access accounts without needing passwords or triggering two-factor authentication. Because session cookies represent an already-authenticated state, they bypass the login step that 2FA is designed to protect. Attackers exploited the stolen sessions to consume paid usage credits before being detected. Anthropic responded by terminating the compromised sessions, removing saved payment methods, and refunding unauthorized charges.

0
ProgrammingDEV Community ·

New API Tool Aims to Fix Character Name Drift in Chinese Webnovel Translations

A developer has launched Chinese Narrative Chapter Lock, an API designed to maintain consistent terminology across long-form Chinese-to-English webnovel translations. The tool addresses a common localization problem where character names, honorifics, sect titles, and cultivation ranks become inconsistent across hundreds of chapters. Unlike full machine translation engines, it functions as a chapter-scoped lock that returns standardized handles for names and terms when fed source text. It is aimed at freelance translators, small localization studios, and developers building Chinese narrative tooling. The tool is available via its own landing page and through RapidAPI, with documentation published online.

0
IndiaTimes of India ·

IIM Bangalore launches Rs 5 lakh national case competition for college students

IIM Bangalore has opened registrations for its National Student Case Competition 2026, offering a total prize pool of Rs 5 lakh. The competition is organised by the Center for Digital Public Goods and centres on real-world problems related to India's Digital Public Infrastructure. Eligible participants must form teams of exactly five students from recognised colleges or universities across India. The deadline for submissions is September 7 at 6 PM, after which shortlisted teams will be invited to present their solutions at IIM Bangalore.

0
IndiaNDTV ·

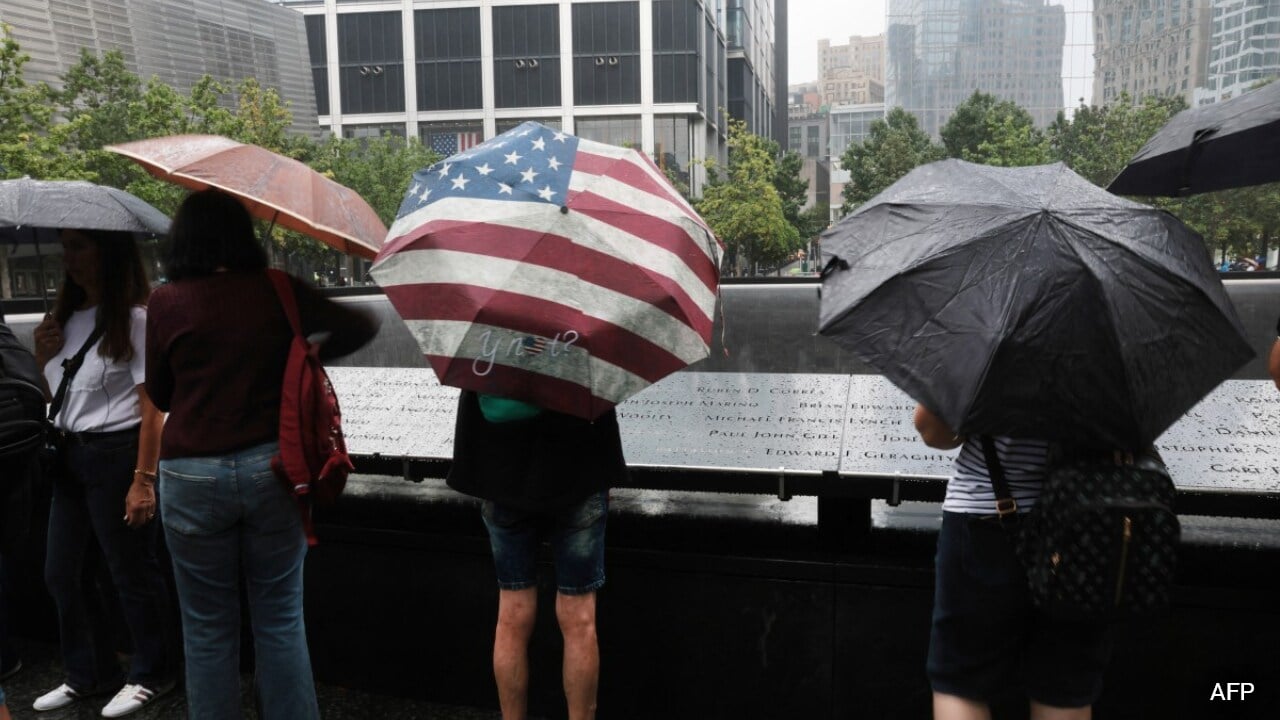
White House Received Al-Qaeda Warning One Week Before 9/11 Attacks

A week before the September 11 attacks, White House counterterrorism coordinator Richard A. Clarke raised urgent concerns about the al-Qaeda threat. Clarke directly questioned then-National Security Advisor Condoleezza Rice about whether the US administration was genuinely committed to addressing the al-Qaeda danger. The warning came amid growing intelligence signals about a potential terrorist strike on American soil. Clarke's query to Rice highlighted what critics later described as a failure to act decisively on pre-attack intelligence.

← NewerPage 803 of 4485Older →