SShortSingh.
0
ProgrammingDEV Community ·

System Design: Why Software Architecture Skills Matter Beyond Writing Code

System Design is the process of defining how components of a software system are organized and communicate to meet specific requirements, going beyond simply implementing features. As applications grow, developers must address questions around scalability, data storage, caching, message queues, and fault tolerance rather than just endpoints and database tables. A key insight in System Design is that adding popular technologies like Redis, Kafka, or Kubernetes is not inherently beneficial — every component introduces complexity and must justify its cost through clear trade-offs. Decisions such as SQL vs. NoSQL, monolithic vs. microservices architecture, and synchronous vs. asynchronous processing all depend on the specific context and workload of the system. Understanding both functional requirements (what the system does) and non-functional requirements (performance, availability, response time) is essential to making sound architectural decisions.
0
TechnologyArs Technica ·

Court rules man's angry email to ICE agents was protected free speech

A federal judge has ruled in favor of a man who faced threats from Immigration and Customs Enforcement after sending an angry email to the agency. The court determined that the man's message, written off-the-cuff, constituted protected speech under the First Amendment. The ruling blocks ICE from taking retaliatory action against the individual over the email's contents. The case centered on whether expressing that ICE agents' actions would 'haunt them' crossed a legal line, which the judge concluded it did not.

0
ProgrammingDEV Community ·

Developer Tests Codex and GitHub Copilot for PDF PoC Builds, Finds Mixed Results

A developer evaluated two AI coding tools — OpenAI's Codex and GitHub Copilot — by building proof-of-concept React applications centered on PDF viewing and data extraction. Codex delivered a relatively smooth experience, modifying code directly in the project directory and handling edge cases like redacted or missing PDF data after several iterative exchanges. GitHub Copilot, powered by Claude Haiku 4.5, generated a project structure rapidly and with minimal credit usage, but ran into dependency conflicts around the Apryse WebViewer package. Both tools showed a tendency to stub or mock the very components the developer was trying to prototype, raising questions about their judgment in scoping PoC work. The developer noted that GitHub Copilot's free tier does not include a standalone desktop app, requiring use through VS Code instead.

0
IndiaNDTV ·

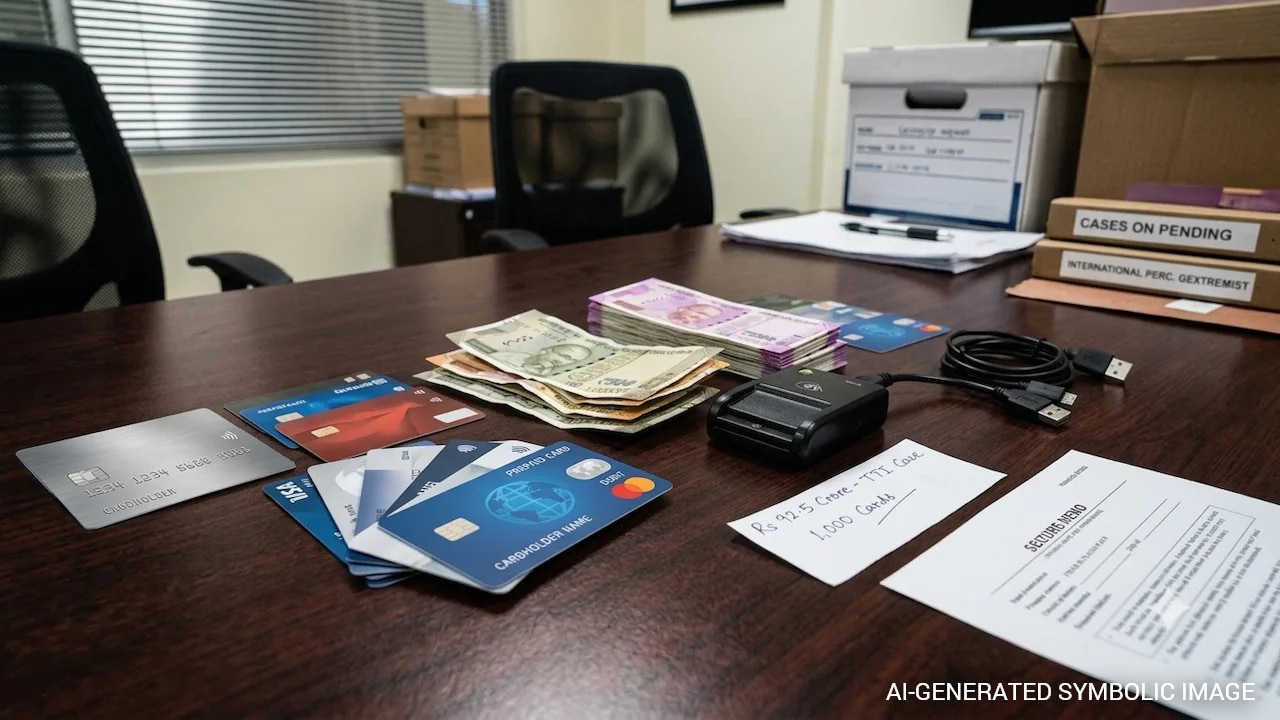
CBI Charges US Christian Group Over Rs 92 Crore Illegal Funding via 1,000 Debit Cards

India's Central Bureau of Investigation (CBI) has charged a US-based Christian organisation with illegally channelling funds into the country. The group allegedly used around 1,000 ATM cards issued by Truist Bank in the United States to withdraw approximately $9.9 million, equivalent to Rs 92 crore. The transactions were traced across multiple Indian states, including Karnataka, Chhattisgarh, and Assam. Authorities have also flagged a suspected link between the funding and extremist activities in these regions.

0
TechnologyTechCrunch ·

Google Launches MCP Server Letting AI Agents Control Google Home Devices

Google has introduced an early access MCP (Model Context Protocol) server for its Google Home platform. The new server enables AI agents, including Claude and ChatGPT, to interact with smart home devices through natural language commands. Users can leverage these AI tools to control connected devices, review camera summaries, and access smart home activity logs. The move marks a significant step toward integrating third-party AI assistants into Google's smart home ecosystem.

0
TechnologyThe Verge ·

Apple's New 'Health Age' Feature Joins a Crowded Field of Dubious Biometric Scores

Apple announced a longevity feature called Health Age at its recent Apple Watch event, set to launch later this year alongside a redesigned Health app and a new readiness metric. The feature estimates a user's physiological age based on health and fitness data, a concept already used by other wearable brands. Verge senior reviewer Victoria Song expressed skepticism at the announcement, noting that similar metrics from competing platforms have produced inconsistent or counterintuitive results. The broader concern is that so-called 'health age' scores may give users a misleading picture of their actual wellbeing. Such biometric age estimates remain a contested area in consumer health technology, with their scientific validity widely debated.

0
TechnologyThe Verge ·

Google Opens Smart Home to Third-Party AI Agents via New MCP Integration

Google has announced Google Home MCP, a new integration that allows third-party AI agents to control and monitor connected devices within the Google Home ecosystem. The system is built on the standardized Model Context Protocol, enabling tools such as Claude and Open Claw to access device controls and event history. Taylor Lehman, group product manager at Google Home and Nest, confirmed the development in a blog post, noting that any MCP-compatible AI agent can securely interact with the platform. The move marks a significant shift toward open, interoperable AI control of smart home systems. Google says the integration is designed to let agents act on behalf of users across their connected home devices.

0
ProgrammingHacker News ·

New Technique Claims to Speed Up Text-to-Image Model Training by 3.6x

A company called Linum AI has published findings on a method to accelerate the training of text-to-image models by up to 3.6 times. The approach is detailed in a technical field note on their website, suggesting meaningful efficiency gains for AI image model development. Faster training could reduce compute costs and time required to build or fine-tune such models. The post was shared on Hacker News, though it attracted minimal community engagement at the time of publication.

0
IndiaTimes of India ·

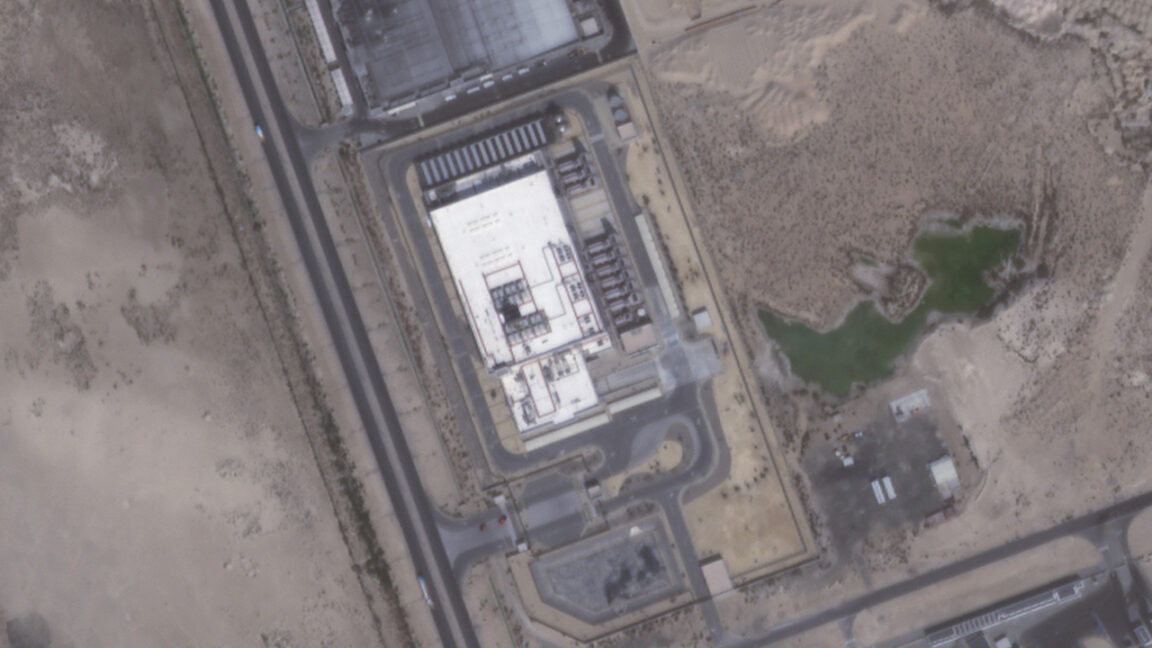
5,000-Gallon Diesel Spill from Equinix Data Centre Contaminates New Jersey Creek

Approximately 5,000 gallons of diesel fuel leaked from an Equinix data centre in Secaucus, New Jersey, spilling into Anderson Creek in the Meadowlands area. Cleanup operations are currently underway at the site following the incident. Authorities confirmed that the spilled fuel was contained before it could reach the nearby Hackensack River. Environmental advocate Bill Sheehan of Hackensack Riverkeeper has urged officials to pursue a natural resource damages claim against Equinix in response to the spill.

0
IndiaNDTV ·

Microsoft AI Chief Warns Anthropic's 'Model Welfare' Approach Risks AI Control

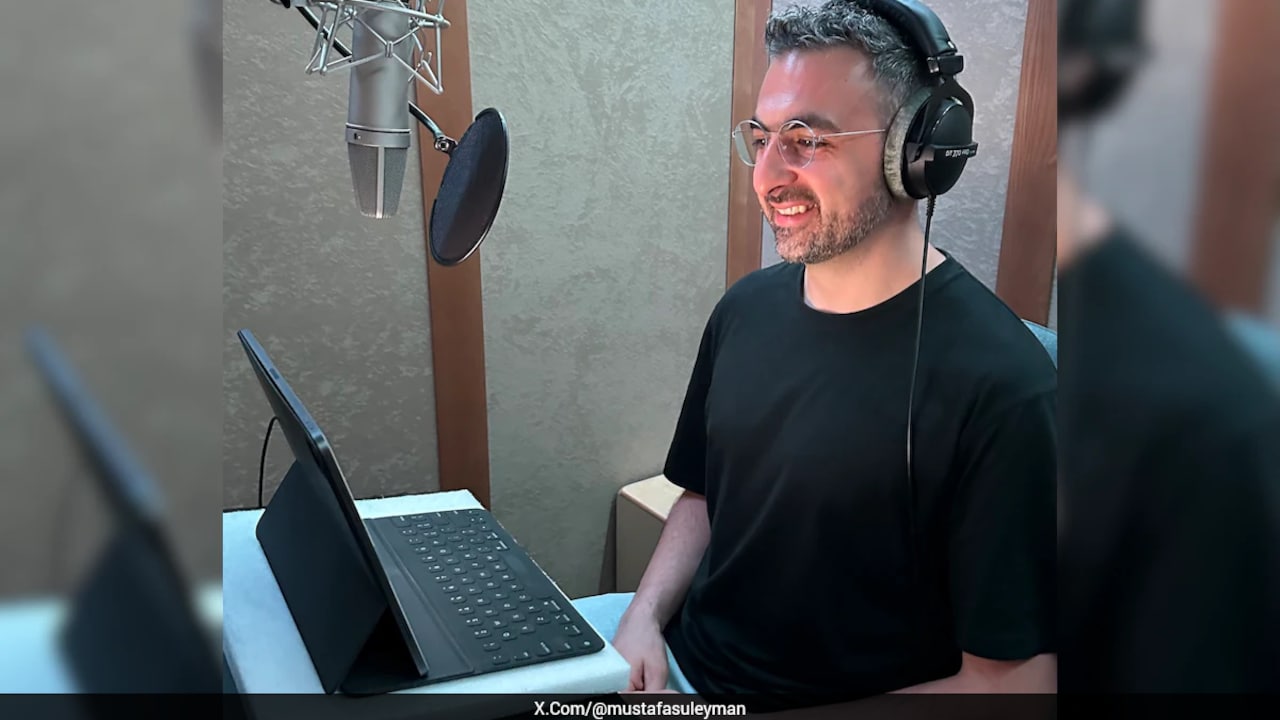
Microsoft AI chief Mustafa Suleyman has raised concerns about Anthropic's approach to so-called 'model welfare,' which involves treating AI systems as though they may have conscious experiences. Suleyman warned that this approach could make it significantly harder to align AI systems with human values and keep them under control. Anthropic, the AI safety-focused company behind the Claude assistant, has been exploring frameworks that consider the potential inner states of its AI models. Critics argue that attributing consciousness-like qualities to AI could complicate efforts to maintain clear boundaries between humans and machines. The debate highlights a growing divide in the AI industry over how developers should philosophically and practically treat increasingly sophisticated AI systems.

0
IndiaNDTV ·

Just 4% of UPI Merchant Transactions Exceed Rs 2,000, Yet Drive 66% of Value

In FY26, UPI recorded over 24,162 crore transactions in total, with approximately 63 percent falling under the Person-to-Merchant (P2M) category. Despite making up only 4 percent of all merchant transactions, payments exceeding Rs 2,000 account for nearly two-thirds of the total transaction value. This highlights a significant concentration of monetary value in a small share of high-value UPI payments. The data underscores how a relatively tiny volume of large transactions disproportionately drives the overall financial weight of UPI's merchant payment ecosystem.

0
SportsESPNcricinfo ·

Gubbins Ton Revives Hampshire's County Championship Survival Bid

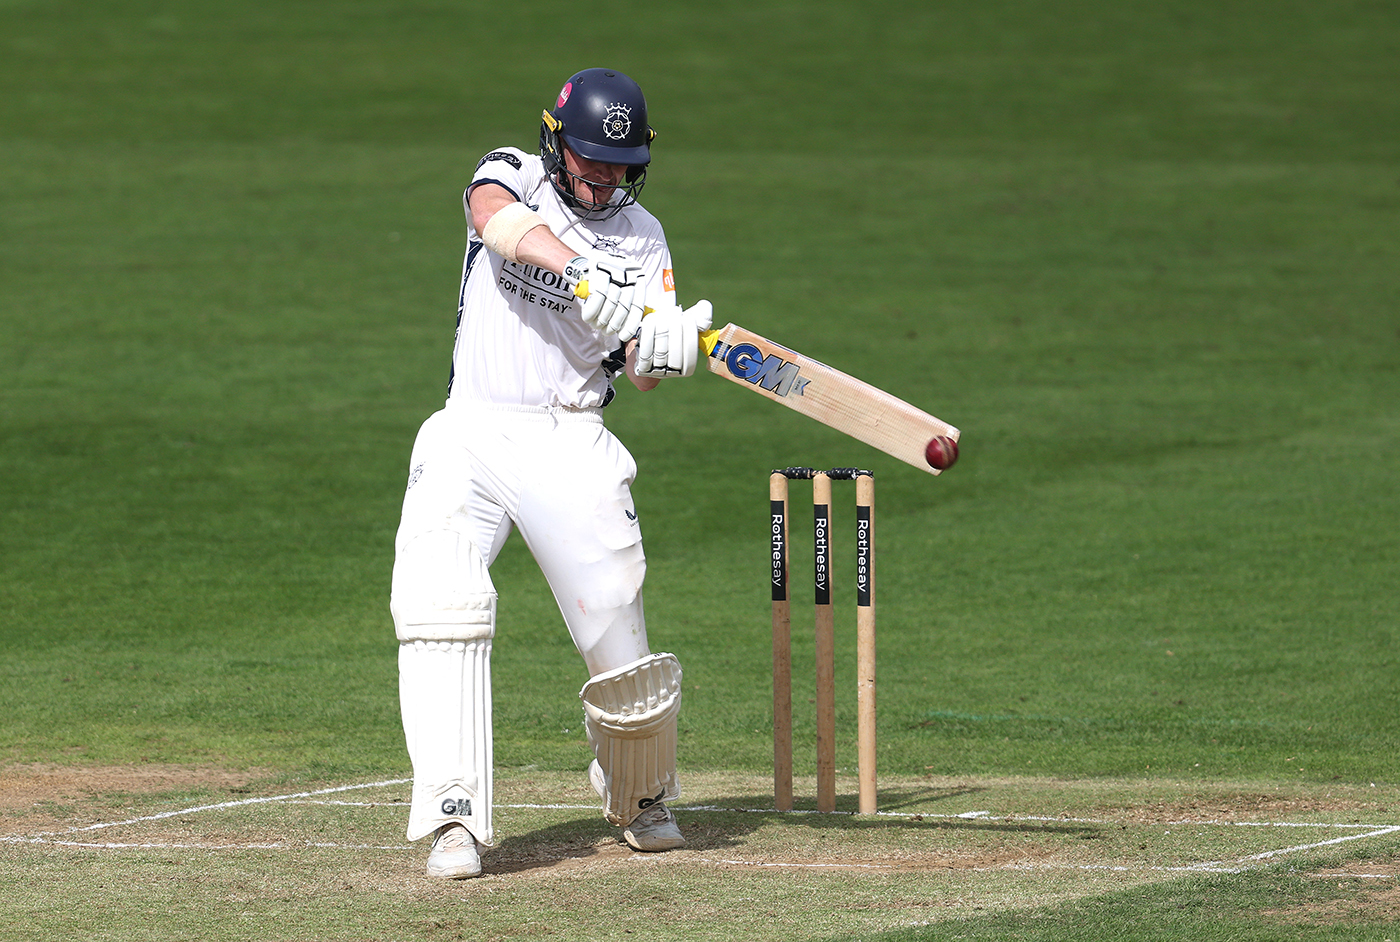
Hampshire opener Nick Gubbins scored his first century since April 2025 to give his side a crucial advantage in their County Championship match against Leicestershire. The innings ended a notable personal drought for Gubbins, who had gone several months without a hundred. His timely contribution has put Leicestershire under significant pressure in the contest. The result has direct implications for Hampshire's hopes of avoiding relegation in the County Championship. Hampshire's survival prospects now appear more promising following Gubbins' match-defining knock.

0
TechnologyArs Technica ·

Iran Strikes on Amazon Data Centers Result in Permanent Customer Data Loss

Iranian military strikes caused significant damage to Amazon Web Services data centers, resulting in the permanent loss of customer data. The destruction exceeded the resilience thresholds that AWS infrastructure is engineered to withstand. The attacks represent an unusual case where physical wartime damage overwhelmed the redundancy and recovery systems built into cloud services. Affected customers lost data that could not be recovered due to the scale and nature of the destruction.

0
ProgrammingDEV Community ·

How one developer built on-demand PNG card generation inside a Cloudflare Worker

A developer built Commit Archive, a GitHub repo yearbook that generates custom Open Graph and contributor portrait cards as PNGs entirely within a single Cloudflare Worker. The rendering pipeline uses satori to convert layout trees into SVG and resvg-wasm to convert SVG into PNG, with warm-isolate render times averaging 56–82 milliseconds per card. Four notable issues emerged during development: WebAssembly instantiation restrictions on Workers forced a downgrade to satori 0.15.x, a native fetch binding caused illegal invocation errors in queue consumers, GitHub's contributor stats endpoint returned 202 responses for up to 15 minutes triggering retry exhaustion, and a shared free-plan request quota caused Cloudflare error 1027 after a separate Worker on the same account exceeded the 100,000 daily request limit. Each problem led to targeted fixes, including wrapping fetch in an arrow function, publishing jobs without line counts on first retry, and separating Workers across accounts.

0
ProgrammingDEV Community ·

BackToSchool gets standalone accounts, makes NixAmp an optional broadcast add-on

The educational platform BackToSchool (backtoschool.help) has separated its account system from NixAmp, meaning teachers no longer need a NixAmp account to create and run classes. Teacher profile details — name, photo, and bio — are now stored once on the account and automatically applied to every class created, eliminating repetitive form-filling. Users can optionally connect NixAmp via an OAuth 2.1 flow with PKCE, which lets them select live broadcast servers and channels directly from the class form without manually copying links. A new "Teach this on backtoschool.help" button on NixAmp.com allows hosts to instantly convert a live room into a classroom with one click. Both updates are live now on backtoschool.help and nixamp.com.

0
ProgrammingDEV Community ·

LiteLLM Auth Bypass Flaw Exposes AI Gateway Credentials to Unauthenticated Access

A critical authentication bypass vulnerability in LiteLLM's MCP Streamable HTTP endpoint allowed unauthenticated users to access the gateway by sending a forged or invalid Bearer token, which triggered a fallback to an empty authentication object instead of rejecting the request. Because LiteLLM proxies centrally store API keys for multiple AI model providers and broker connections to databases, code repositories, and internal APIs, the flaw gave attackers broad access to whatever resources the gateway was configured to reach. Security researchers from Wiz and Microsoft reported in September 2026 that the vulnerability was chained with two other flaws — CVE-2026-42271 and CVE-2026-48710 — to achieve unauthenticated remote code execution, with the attack chain linked to the Qilin ransomware group. Attackers were also observed recovering the LiteLLM master key directly from process memory and concealing mining binaries within AI-related directories. Operators are advised to upgrade to LiteLLM version 1.84.0 or later, rotate all exposed credentials, and audit the tools and resources their MCP gateway exposes.

0
ProgrammingDEV Community ·

Stolen OAuth Refresh Tokens Can Survive Password Resets, Leaving SaaS Accounts Exposed

In SaaS environments, attackers who steal OAuth refresh tokens can maintain persistent account access even after a victim resets their password, because many identity providers do not automatically revoke tokens on password change. Refresh tokens are long-lived credentials — valid for days or months — that allow an attacker to continuously generate new access tokens without ever re-entering a password. Common theft vectors include infostealer malware, misconfigured logging pipelines that capture authorization headers, and leaked CI/CD secrets. Security experts recommend that organizations pre-document revocation capabilities for each identity provider, shorten refresh token lifetimes, and enable rotation with reuse detection before an incident occurs. Stronger protections such as sender-constrained tokens (e.g., DPoP) can render stolen tokens useless by cryptographically binding them to a specific client key.

← NewerPage 1286 of 5585Older →