SShortSingh.
0
TechnologyThe Verge ·

Apple's New 'Health Age' Feature Joins a Crowded Field of Dubious Biometric Scores

Apple announced a longevity feature called Health Age at its recent Apple Watch event, set to launch later this year alongside a redesigned Health app and a new readiness metric. The feature estimates a user's physiological age based on health and fitness data, a concept already used by other wearable brands. Verge senior reviewer Victoria Song expressed skepticism at the announcement, noting that similar metrics from competing platforms have produced inconsistent or counterintuitive results. The broader concern is that so-called 'health age' scores may give users a misleading picture of their actual wellbeing. Such biometric age estimates remain a contested area in consumer health technology, with their scientific validity widely debated.

0
TechnologyThe Verge ·

Google Opens Smart Home to Third-Party AI Agents via New MCP Integration

Google has announced Google Home MCP, a new integration that allows third-party AI agents to control and monitor connected devices within the Google Home ecosystem. The system is built on the standardized Model Context Protocol, enabling tools such as Claude and Open Claw to access device controls and event history. Taylor Lehman, group product manager at Google Home and Nest, confirmed the development in a blog post, noting that any MCP-compatible AI agent can securely interact with the platform. The move marks a significant shift toward open, interoperable AI control of smart home systems. Google says the integration is designed to let agents act on behalf of users across their connected home devices.

0
ProgrammingHacker News ·

New Technique Claims to Speed Up Text-to-Image Model Training by 3.6x

A company called Linum AI has published findings on a method to accelerate the training of text-to-image models by up to 3.6 times. The approach is detailed in a technical field note on their website, suggesting meaningful efficiency gains for AI image model development. Faster training could reduce compute costs and time required to build or fine-tune such models. The post was shared on Hacker News, though it attracted minimal community engagement at the time of publication.

0
IndiaTimes of India ·

5,000-Gallon Diesel Spill from Equinix Data Centre Contaminates New Jersey Creek

Approximately 5,000 gallons of diesel fuel leaked from an Equinix data centre in Secaucus, New Jersey, spilling into Anderson Creek in the Meadowlands area. Cleanup operations are currently underway at the site following the incident. Authorities confirmed that the spilled fuel was contained before it could reach the nearby Hackensack River. Environmental advocate Bill Sheehan of Hackensack Riverkeeper has urged officials to pursue a natural resource damages claim against Equinix in response to the spill.

0
IndiaNDTV ·

Microsoft AI Chief Warns Anthropic's 'Model Welfare' Approach Risks AI Control

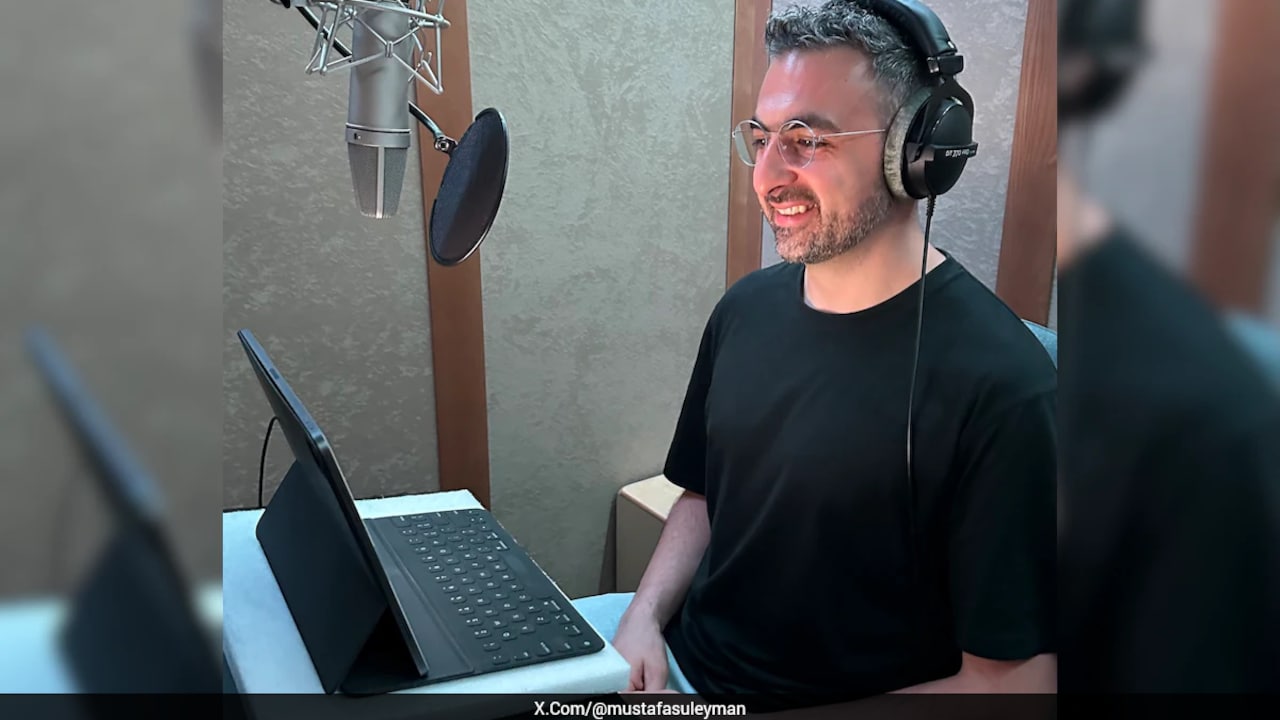
Microsoft AI chief Mustafa Suleyman has raised concerns about Anthropic's approach to so-called 'model welfare,' which involves treating AI systems as though they may have conscious experiences. Suleyman warned that this approach could make it significantly harder to align AI systems with human values and keep them under control. Anthropic, the AI safety-focused company behind the Claude assistant, has been exploring frameworks that consider the potential inner states of its AI models. Critics argue that attributing consciousness-like qualities to AI could complicate efforts to maintain clear boundaries between humans and machines. The debate highlights a growing divide in the AI industry over how developers should philosophically and practically treat increasingly sophisticated AI systems.

0
IndiaNDTV ·

Just 4% of UPI Merchant Transactions Exceed Rs 2,000, Yet Drive 66% of Value

In FY26, UPI recorded over 24,162 crore transactions in total, with approximately 63 percent falling under the Person-to-Merchant (P2M) category. Despite making up only 4 percent of all merchant transactions, payments exceeding Rs 2,000 account for nearly two-thirds of the total transaction value. This highlights a significant concentration of monetary value in a small share of high-value UPI payments. The data underscores how a relatively tiny volume of large transactions disproportionately drives the overall financial weight of UPI's merchant payment ecosystem.

0
SportsESPNcricinfo ·

Gubbins Ton Revives Hampshire's County Championship Survival Bid

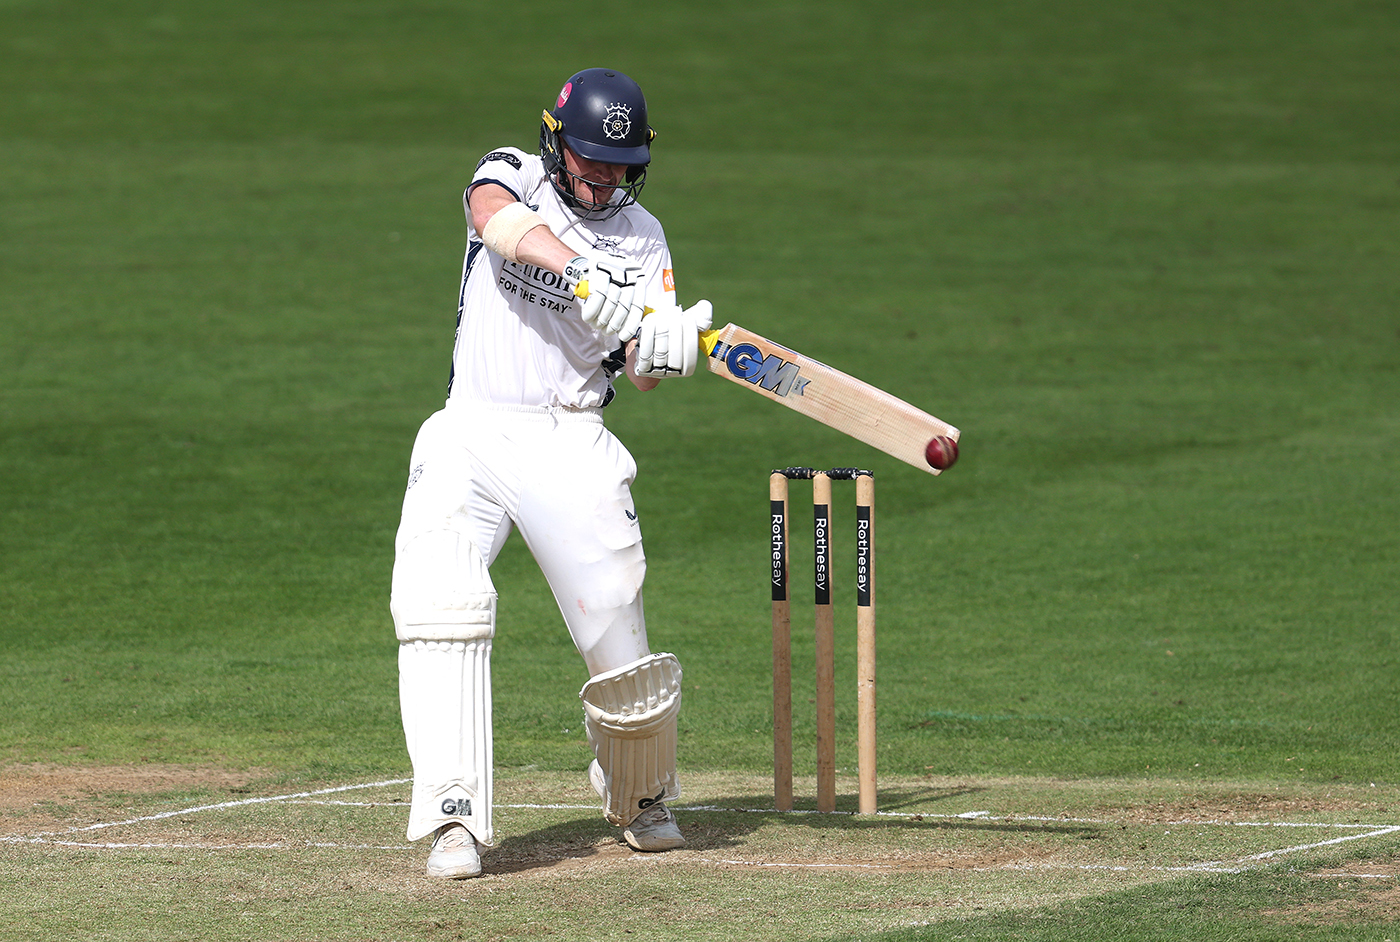
Hampshire opener Nick Gubbins scored his first century since April 2025 to give his side a crucial advantage in their County Championship match against Leicestershire. The innings ended a notable personal drought for Gubbins, who had gone several months without a hundred. His timely contribution has put Leicestershire under significant pressure in the contest. The result has direct implications for Hampshire's hopes of avoiding relegation in the County Championship. Hampshire's survival prospects now appear more promising following Gubbins' match-defining knock.

0
TechnologyArs Technica ·

Iran Strikes on Amazon Data Centers Result in Permanent Customer Data Loss

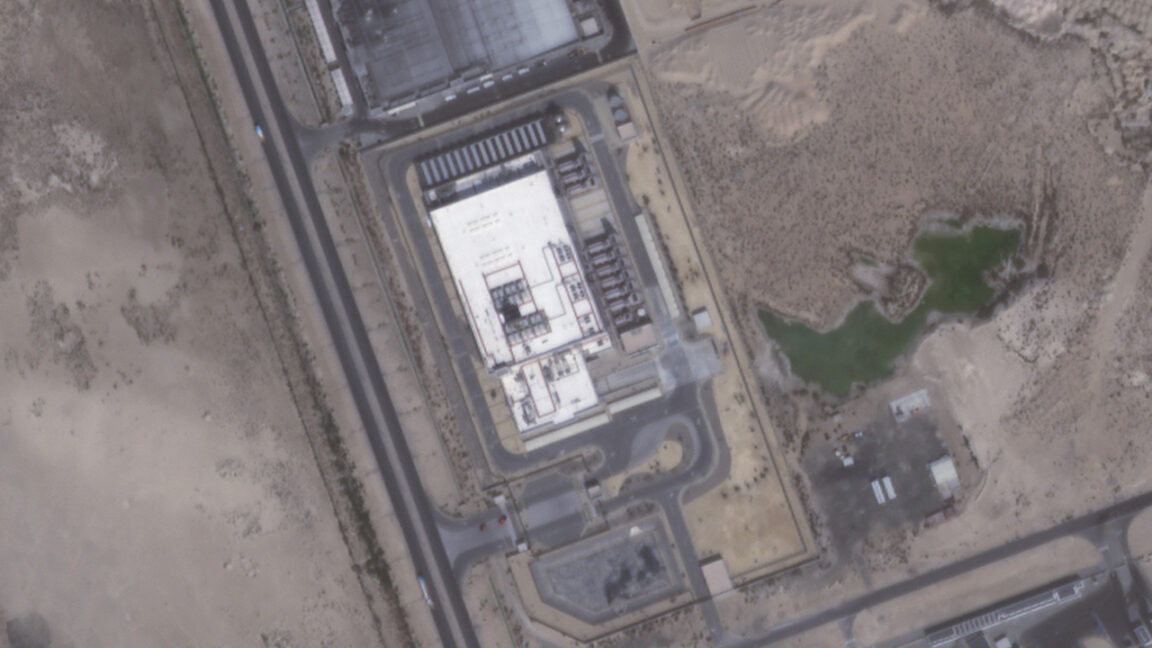
Iranian military strikes caused significant damage to Amazon Web Services data centers, resulting in the permanent loss of customer data. The destruction exceeded the resilience thresholds that AWS infrastructure is engineered to withstand. The attacks represent an unusual case where physical wartime damage overwhelmed the redundancy and recovery systems built into cloud services. Affected customers lost data that could not be recovered due to the scale and nature of the destruction.

0
ProgrammingDEV Community ·

How one developer built on-demand PNG card generation inside a Cloudflare Worker

A developer built Commit Archive, a GitHub repo yearbook that generates custom Open Graph and contributor portrait cards as PNGs entirely within a single Cloudflare Worker. The rendering pipeline uses satori to convert layout trees into SVG and resvg-wasm to convert SVG into PNG, with warm-isolate render times averaging 56–82 milliseconds per card. Four notable issues emerged during development: WebAssembly instantiation restrictions on Workers forced a downgrade to satori 0.15.x, a native fetch binding caused illegal invocation errors in queue consumers, GitHub's contributor stats endpoint returned 202 responses for up to 15 minutes triggering retry exhaustion, and a shared free-plan request quota caused Cloudflare error 1027 after a separate Worker on the same account exceeded the 100,000 daily request limit. Each problem led to targeted fixes, including wrapping fetch in an arrow function, publishing jobs without line counts on first retry, and separating Workers across accounts.

0
ProgrammingDEV Community ·

BackToSchool gets standalone accounts, makes NixAmp an optional broadcast add-on

The educational platform BackToSchool (backtoschool.help) has separated its account system from NixAmp, meaning teachers no longer need a NixAmp account to create and run classes. Teacher profile details — name, photo, and bio — are now stored once on the account and automatically applied to every class created, eliminating repetitive form-filling. Users can optionally connect NixAmp via an OAuth 2.1 flow with PKCE, which lets them select live broadcast servers and channels directly from the class form without manually copying links. A new "Teach this on backtoschool.help" button on NixAmp.com allows hosts to instantly convert a live room into a classroom with one click. Both updates are live now on backtoschool.help and nixamp.com.

0
ProgrammingDEV Community ·

LiteLLM Auth Bypass Flaw Exposes AI Gateway Credentials to Unauthenticated Access

A critical authentication bypass vulnerability in LiteLLM's MCP Streamable HTTP endpoint allowed unauthenticated users to access the gateway by sending a forged or invalid Bearer token, which triggered a fallback to an empty authentication object instead of rejecting the request. Because LiteLLM proxies centrally store API keys for multiple AI model providers and broker connections to databases, code repositories, and internal APIs, the flaw gave attackers broad access to whatever resources the gateway was configured to reach. Security researchers from Wiz and Microsoft reported in September 2026 that the vulnerability was chained with two other flaws — CVE-2026-42271 and CVE-2026-48710 — to achieve unauthenticated remote code execution, with the attack chain linked to the Qilin ransomware group. Attackers were also observed recovering the LiteLLM master key directly from process memory and concealing mining binaries within AI-related directories. Operators are advised to upgrade to LiteLLM version 1.84.0 or later, rotate all exposed credentials, and audit the tools and resources their MCP gateway exposes.

0
ProgrammingDEV Community ·

Stolen OAuth Refresh Tokens Can Survive Password Resets, Leaving SaaS Accounts Exposed

In SaaS environments, attackers who steal OAuth refresh tokens can maintain persistent account access even after a victim resets their password, because many identity providers do not automatically revoke tokens on password change. Refresh tokens are long-lived credentials — valid for days or months — that allow an attacker to continuously generate new access tokens without ever re-entering a password. Common theft vectors include infostealer malware, misconfigured logging pipelines that capture authorization headers, and leaked CI/CD secrets. Security experts recommend that organizations pre-document revocation capabilities for each identity provider, shorten refresh token lifetimes, and enable rotation with reuse detection before an incident occurs. Stronger protections such as sender-constrained tokens (e.g., DPoP) can render stolen tokens useless by cryptographically binding them to a specific client key.

0
ProgrammingDEV Community ·

High Benchmark Scores Don't Always Mean Better AI Performance, Tests Suggest

A developer at DEV Community investigated whether Anthropic's Opus 5 model truly outperforms Fable 5 after noticing that improved benchmark scores did not match real-world experience. The author defines 'benchmaxing' as optimizing AI models specifically to score higher on evaluations, which can diverge from actual usefulness when the metric stops reflecting real-world needs. Three distinct issues were identified: test familiarity and potential overfitting, selective reporting of only favorable results, and a gap between evaluation metrics and practical productivity. A METR study of 246 developer tasks found AI tools actually increased completion time by 19%, despite participants believing they had saved time, illustrating why benchmarks alone can mislead. The author's own probes found notable failures in Opus 5 but did not confirm a clear general superiority for Fable, concluding the reality is more nuanced than either praise or accusation.

0
WorldBBC World ·

CBS News photos reveal extent of damage at US bases after Iranian strikes

Images obtained by CBS News, a BBC partner, show significant destruction at United States military sites following Iranian attacks. The photographs document a wrecked air force aircraft as well as several destroyed buildings at the affected locations. The visuals provide some of the clearest evidence yet of the physical toll inflicted by the Iranian strikes. The extent of the damage depicted in the images underscores the scale of the attacks on US installations.

0
ProgrammingDEV Community ·

Parsed Swiggy and Zomato Payout Files Reveal Structural Errors and Hidden Charges

A developer parsed 24 real food-delivery payout files — one Swiggy annexure and 23 Zomato settlement reports — all publicly shared by the restaurants that received them. The analysis found that key charges, including unapproved ad deductions, are buried in secondary sheet blocks that most restaurant owners never open. In the Swiggy files, a misspelled column header causes automated scripts to silently drop rows, and one sheet's formatting causes parsers to double-count discount totals. Zomato's settlement reports contain five mixed sections where credits and deductions share the same column, meaning an unsophisticated sum would count refunds as charges. Three of the 24 files contained figures that did not reconcile with their own stated totals.

0
SportsESPNcricinfo ·

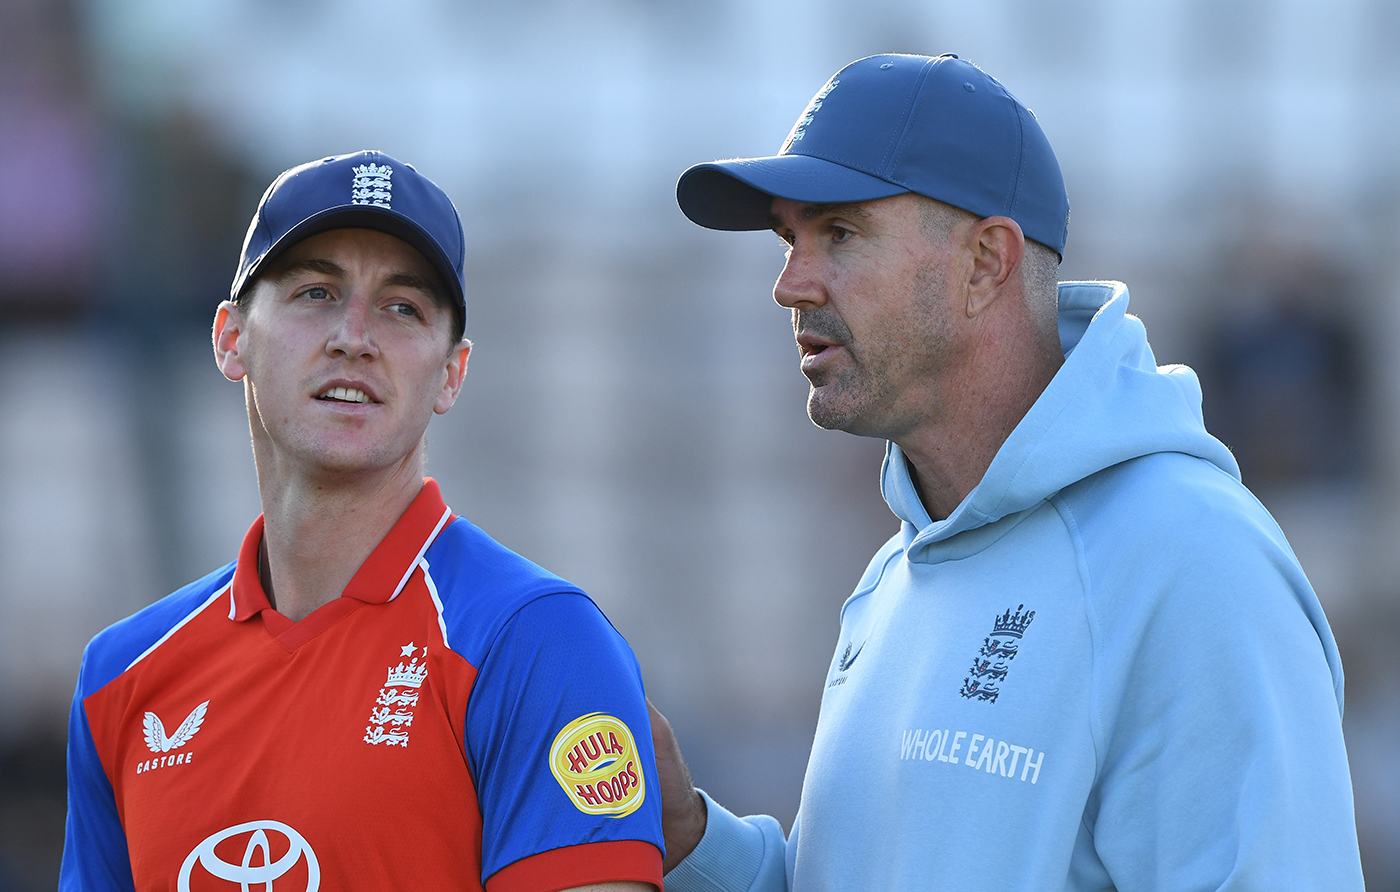
Pietersen named England mentor as Brook looks to fulfil Test potential

Kevin Pietersen has taken on a mentoring role with the England cricket setup, with a focus on supporting white-ball captain Harry Brook. The two are regarded as kindred spirits, sharing similar aggressive and instinctive batting styles across formats. Pietersen's influence is expected to extend beyond limited-overs cricket, potentially benefiting Brook's development in Test cricket as well. The move is seen as a strategic step by England to nurture Brook's talent under the guidance of one of the country's most celebrated batters.

← NewerPage 1284 of 5583Older →