GitHub Security Lab Launches AI-Powered Fuzzing via Taskflow Agent
0
·1 views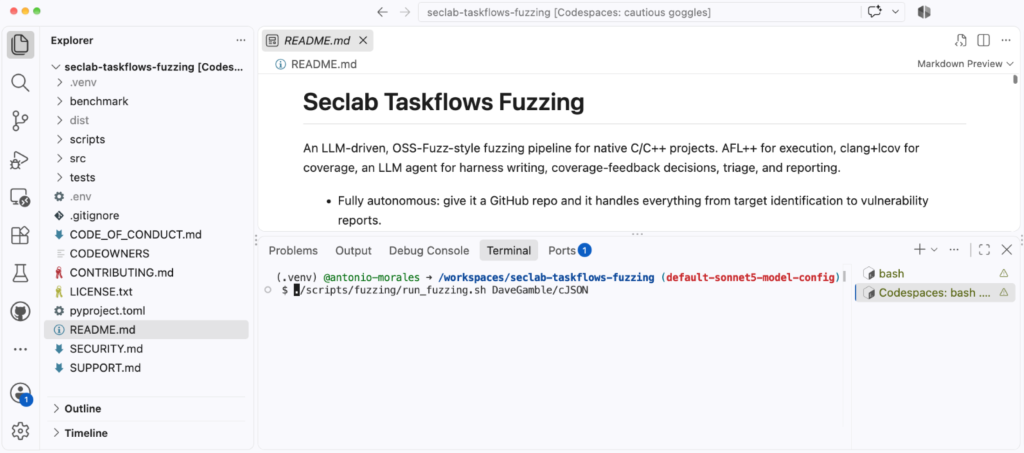
GitHub Security Lab has introduced a new AI-driven fuzzing capability built on its Taskflow Agent framework. The feature was announced through an official GitHub Blog post detailing how developers can use the new fuzzing taskflow. Fuzzing is a software testing technique that feeds random or unexpected inputs to programs to uncover security vulnerabilities. The Taskflow Agent framework serves as the underlying AI infrastructure powering this automated security testing workflow. The development reflects GitHub's broader push to integrate AI tools into software security and vulnerability discovery processes.
This is an AI-generated summary. ShortSingh links to the original source for the complete article.
Discussion (0)
Log in to join the discussion and vote.
Log in