0
0
ProgrammingDEV Community ·
Developer adds free in-browser auto captions to YouTube Shorts converter using Whisper AI
A developer has integrated automatic caption generation into Convert to Shorts, a free browser-based tool that reformats horizontal videos to the 9:16 YouTube Shorts aspect ratio without server uploads. The feature was the most-requested after the tool's launch, driven by the fact that most Shorts viewers watch without sound and manual captioning is time-consuming. To preserve the tool's privacy-first design, the developer ran OpenAI's Whisper Tiny speech recognition model entirely in the browser using Transformers.js and WebAssembly, avoiding any video upload to external servers. Audio is extracted and resampled to 16kHz mono using the Web Audio API before being passed to Whisper, which returns timestamped transcript segments. Captions are then burned into the video using ffmpeg.wasm with the ASS subtitle format, after simpler approaches like chained drawtext filters proved unreliable.
0
ProgrammingDEV Community ·
Developer shares workflow for turning Figma Make exports into real apps using Claude Code
A developer launched four web apps between February and April 2026, each starting from front-end code bundles generated by Figma's AI tool, Figma Make. The generated exports shared common limitations: exact-pinned dependencies, no data layer, and mock data with no persistence or authentication. Using Anthropic's CLI coding agent Claude Code, the developer worked to transform these static outputs into functional products. Progress varied by project — a beauty-curation site was deployed as a static site on AWS Amplify, while a UI mock for an AI tool was intentionally left as-is. The developer reflects that deciding not to develop a project further is itself a valid product decision.
0
ProgrammingDEV Community ·
Dev builds demo platform to donate surplus solar credits to low-income families in Brazil
A developer created Community Solar Energy Bank, a demonstration platform that allows solar panel owners in Brazil to redirect their unused net-metering credits to low-income families via NGOs connected to local utility companies. The project was built for the DEV Community Weekend Challenge: Generosity Edition hackathon. It uses real utility company data for several Brazilian states but features entirely fictional NGOs, and no actual money or energy is transferred at any point. Users can select their state, choose a utility, pick an NGO, and specify surplus kWh to donate, with Google Gemini providing an AI-generated checklist of utility requirements and an impact summary. The platform was built using Next.js, TypeScript, Prisma, PostgreSQL, and Google Gemini, with a live demo hosted on Vercel.

0
ProgrammingDEV Community ·
How 131 Process Restarts Silently Broke a Failure-Escalation Guard
A software engineer discovered that a self-healing daemon restarted 131 times in 24 hours, resetting its in-memory failure counter to zero each time and making its escalation threshold permanently unreachable. The guard was designed to alert a human after three consecutive failed self-heal rounds, but because the counter lived inside the process itself, every restart wiped the tally clean. Across 1,501 daemon starts, zero escalations were ever triggered, and unit tests gave no warning since restarts do not occur in that environment. The root cause is that an in-process counter cannot distinguish between a failure never occurring and a failure being forgotten due to a restart. The recommended fix replaces counters with an externally written timestamp file, whose age can be checked independently of process state, making restarts structurally invisible to the alerting logic.
0
ProgrammingDEV Community ·
Why PostgreSQL's COUNT(*) Stays Slow Even With an Index Added
A technical deep-dive explains why COUNT(*) queries in PostgreSQL can be slow on large tables, despite the operation appearing simple. PostgreSQL uses Multi-Version Concurrency Control (MVCC), which means it cannot rely on a stored row counter and must instead evaluate row visibility at query time. Adding an index does not automatically speed up COUNT(*), as the query planner chooses access paths based on row distribution, statistics, and estimated cost. An Index Only Scan — which can reduce heap visits — is only possible when the visibility map marks relevant pages as all-visible, a state maintained through regular VACUUM operations. Developers are advised to use EXPLAIN with ANALYZE and BUFFERS to understand actual scan behavior before assuming an index will resolve the performance issue.
0
ProgrammingDEV Community ·
XopProtector Offers Lightweight Android App Protection Without Performance Penalties
XopProtector is an open-source Android application protection framework designed to deliver strong security without the typical trade-offs of larger APK size, slower builds, or sluggish startup times. The tool combines multiple protection technologies including DEX encryption, method-level protection, PVM2 virtualization, native runtime protection, and runtime risk detection such as Frida and hook detection. According to the developers, a 300MB APK can be protected within approximately five minutes, making it more practical for frequent builds and automated CI/CD pipelines. XopProtector employs caching mechanisms to differentiate between cold and warm starts, aiming to prevent protection overhead from becoming a noticeable bottleneck for end users. The project positions itself as a complete Android protection framework and a developer-friendly alternative to commercial solutions that may impose high costs, longer build times, or significant APK size increases.
0
IndiaTimes of India ·
Supriya Sule asks public to stop discussing cousin Ajit Pawar's fatal accident
NCP leader Supriya Sule has announced she will no longer speak about the death of her cousin Ajit Pawar. She urged the public to also refrain from further discussion of the incident, citing concerns over growing misunderstandings. Ajit Pawar died in an accident near Baramati airport on January 28. Sule's appeal appears aimed at preventing misinformation or controversy surrounding the tragic event.
0
ProgrammingDEV Community ·
Anthropic adds watermark to Claude outputs to flag AI-generated text
Anthropic has introduced a watermarking system for text generated by its Claude models, using a deterministic, private-key-based method to select tokens without adding latency or consuming extra tokens. The move aligns with the EU Artificial Intelligence Act, passed in 2024, which mandates machine-readable labelling of AI-generated content for systems operating in Europe from August 2026. Despite several major tech companies signing on to related commitments, practical implementation across the industry remains limited. Key concerns holding companies back include potential revenue losses estimated at up to 30%, text traceability risks, and technical weaknesses such as reduced output creativity and vulnerability to rewriting attacks. Currently, the watermark can only confirm whether content was AI-generated or AI-altered, not trace it back to a specific author.

0
ProgrammingDEV Community ·
Why Your RAG System Gives Wrong Answers Even When All Metrics Look Fine
Many AI observability setups track model-level metrics like latency, token usage, and errors but fail to monitor the retrieval pipeline that feeds the model its information. A typical RAG system passes a user query through multiple stages — including query rewriting, search, extraction, deduplication, and reranking — each of which can silently introduce errors. Because standard LLM traces only capture the final prompt and response, they cannot reveal whether the model received outdated, duplicate, or simply wrong evidence. OpenTelemetry's generative AI conventions and tools like LangSmith are beginning to treat retrieval as a distinct, traceable component with its own metadata. Experts argue that production teams should measure retrieval-specific signals such as source freshness, citation coverage, and duplicate evidence to reliably diagnose why grounded answers go wrong.
0
ProgrammingDEV Community ·
Attackers Exploit Langflow 12 Times in 2026, Targeting AI and Cloud API Keys
Threat intelligence firm VulnCheck recorded over 360 exploitation attempts against Langflow between August 29 and 30, 2026, with most traffic traced to Russia. The attacks targeted CVE-2026-0768, a critical unauthenticated remote code execution vulnerability scoring 9.8 on the CVSS scale. Rather than deploying ransomware, attackers focused on harvesting environment variables containing OpenAI API keys, AWS access credentials, and Langflow superuser tokens. According to the Cloud Security Alliance, this is the twelfth Langflow vulnerability exploited in the wild this year, with total exploitation attempts across its 2026 CVE portfolio exceeding 15,000. Security researchers warn that AI development frameworks like Langflow, originally built for speed and demos, are increasingly being deployed in production environments without adequate security hardening.
0
ProgrammingHacker News ·
Virginia Mother Convicted After 5-Year-Old Walked Alone to Nearby Pond
A Virginia mother has been convicted following an incident in which her 5-year-old child walked unaccompanied to a pond located a short distance from their home. The case drew public attention as it took place within a gated community, raising questions about what constitutes adequate parental supervision. The mother was subsequently sentenced, though details of the penalty were not fully disclosed in the available information. The case has reignited debate around so-called 'free-range parenting' and the extent to which authorities should intervene in parenting decisions. Critics argue that prosecuting parents for brief lapses in supervision of young children may be an overreach of the legal system.
0
IndiaTimes of India ·
MP Student Who Cleaned River Solo Gets Job Offer From Ocean Cleanup NGO
A young student from Biaora, Madhya Pradesh, known as 'Bittu Tabahi', has received a job offer from The Ocean Cleanup, a Netherlands-based environmental NGO. His solo river-cleaning initiative drew widespread attention after former England cricketer Kevin Pietersen publicly praised his efforts. Impressed by his dedication, the global organization reached out with an employment opportunity. The student is currently awaiting further details about the specific role and responsibilities offered to him.
0
0
ProgrammingDEV Community ·
Study Finds No Single Mechanism Causes Neural Network Training Loss Spikes
A controlled experiment testing four competing theories about loss spikes in neural network training found that none of the proposed mechanisms — edge-of-stability thresholds, weight-norm collapse, numerical precision, or non-normal amplification — is sufficient on its own to trigger spikes. The study used a standardized MLP benchmark across 60 runs to measure each mechanism's proposed trigger simultaneously, something prior 2026 papers had not done. Results showed that weight-norm collapse occurred in runs with zero spikes, and crossing the sharpness threshold was statistically no better than a coin flip at predicting spikes. A freezing experiment revealed that spikes require both a sharp training regime and ongoing adaptation of scale-invariant hidden projection weights — remove either condition and spikes cease. The findings, currently under peer review, are limited to a toy MLP under plain SGD and have not yet been validated in larger transformer or AdamW settings.
0
ProgrammingDEV Community ·
Lambda Language Uses Four Backends to Cross-Check Program Correctness
A project called 'lm' (lambda-language) compiles code through four independent backends — C, WebAssembly, ARM64, and a bytecode VM — using the same typed AST as input. Its correctness model relies on all four backends producing identical output, with the VM's different internal machinery serving as especially strong corroborating evidence. However, the project explicitly documents four known divergence points where backend agreement is not guaranteed: division by zero, out-of-range float-to-integer casts, out-of-bounds memory access, and edge-case floating-point printing. These divergences stem from each backend deferring to its target platform's native instruction behavior rather than enforcing a unified specification. The divergence list is treated as a design document, keeping the four-way comparison meaningful by ensuring known exceptions are small, well-defined, and confined to the edges of the language's guarantees.
0
IndiaNDTV ·
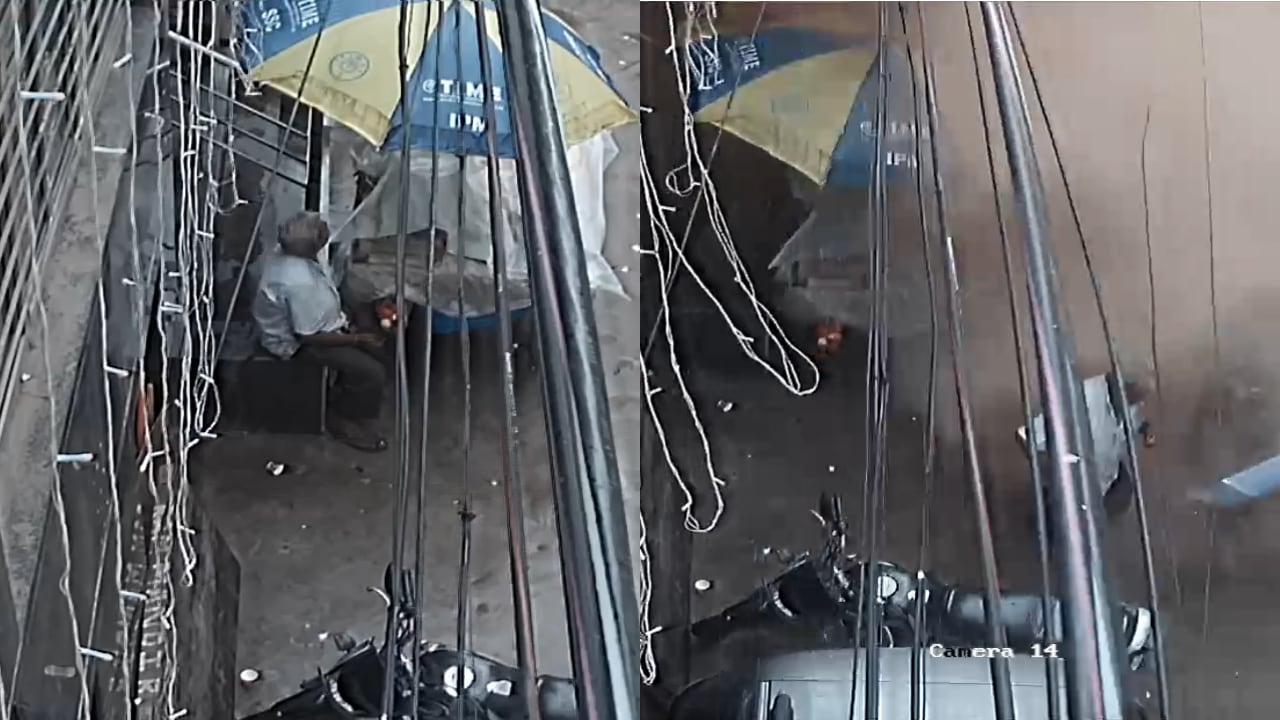
Delhi Building Collapse Kills 6, Rescuers Pull 13 Survivors from Rubble
A nearly 50-year-old building in Delhi collapsed, trapping multiple people under its debris. Rescue teams managed to pull out 13 survivors from the wreckage. Five victims were found dead and brought to AIIMS, while a sixth critically injured person succumbed during treatment. The incident has raised concerns about the structural safety of aging buildings in the city.
0
0
IndiaTimes of India ·
AfD wins 44% in Saxony-Anhalt, marking far-right milestone in German politics
Germany's far-right Alternative für Deutschland (AfD) party has achieved a historic electoral result in the state of Saxony-Anhalt, securing approximately 44% of the vote according to projections. The result places the AfD well ahead of the mainstream conservative CDU party, representing a significant shift in German post-war political history. The outcome is being described as a breakthrough moment for the far-right in Germany. Despite the strong showing, the AfD is expected to face difficulties forming a government as it falls short of an outright majority. The result has drawn varied reactions internationally, with observers noting the unexpected scale of the party's support.