SShortSingh.
0
ProgrammingDEV Community ·

CrowdStrike Falcon Zero-Day PoC Enables SYSTEM Privilege Escalation on Windows

Security researchers have published a proof-of-concept exploit, dubbed FalconFlank, that abuses CrowdStrike Falcon Sensor's Microsoft Office macro removal feature to escalate privileges from a low-privileged user to SYSTEM on Windows endpoints. The PoC works by manipulating file operations during Falcon's macro remediation process to write a malicious DLL to a protected system path, specifically C:\Windows\System32\WindowsPowerShell\v1.0\bcrypt.dll, which is then loaded with elevated privileges. Exploitation requires the attacker to already have low-privileged local code execution on the target machine and the Falcon Sensor's Office macro removal setting to be active. No active in-the-wild attacks leveraging this technique have been observed as of the disclosure date of September 4, 2026. CrowdStrike has issued interim guidance recommending that administrators disable the Windows policy setting for Microsoft Office File Suspicious Macro Removal while a full fix is pending.

0
ProgrammingDEV Community ·

Google Patches Actively Exploited Chrome Zero-Day Flaw in V8 Engine

Google has released an emergency security update for Chrome to address CVE-2026-85046, a critical type confusion vulnerability in the V8 JavaScript engine that is being actively exploited in the wild. The flaw allows a remote attacker to trigger arbitrary code execution within the browser sandbox by directing a user to a specially crafted HTML page. CISA has added the vulnerability to its Known Exploited Vulnerabilities catalog, signaling urgency for organizations to act. Users on Windows and macOS should update to Chrome version 152.0.7977.82 or 152.0.7977.83, while Linux users should update to 152.0.7977.82, and restart the browser to complete the patch. Operators of Chromium-based browsers are also advised to check for available updates and restrict access to untrusted sites in the interim.

0
ProgrammingDEV Community ·

Cline VS Code Extension Turns AI Coding Into a Human-Approved Execution Loop

Cline is a TypeScript-based VS Code extension that transforms an IDE into an iterative AI-driven coding loop, where the model inspects files, proposes changes, runs commands, and observes failures in sequence. A key design feature is mandatory human approval at each meaningful step—such as file writes and shell commands—ensuring the agent cannot act silently on the entire system. Performance on focused tasks is fast, but context costs grow significantly as command outputs, diffs, and errors accumulate across longer or broader refactoring sessions. The extension is particularly suited to scoped implementation and debugging work, though large monorepos can cause noticeable spikes in both latency and token usage. The author recommends keeping destructive commands like Docker deployments guarded and reviewing every diff, emphasizing that human engineering judgment remains essential even with AI assistance.

0
ProgrammingDEV Community ·

Why Pasting Secrets Into Your Browser Console Is a Security Risk

Developers commonly paste API tokens, JWTs, and environment keys into the browser console for debugging, but this practice carries two distinct security risks. First, browser consoles store history locally, meaning pasted secrets persist on the machine until manually cleared. Second, using third-party websites to decode tokens effectively transmits those credentials to external servers, where they may be logged. The recommended fix is to avoid pasting secrets into the console entirely and to use local, browser-based JWT decoders that process tokens without any external transmission. Adopting these habits replaces a common but risky workflow with a secure alternative that requires no additional tools or setup.

0
ProgrammingDEV Community ·

Study of 1,000 Repos Reveals git blame Misses Team Process Patterns

A large-scale analysis of over 1,000 code repositories, spanning personal projects, client work, and public codebases, uncovered consistent patterns that challenge common assumptions about repository health. The study found that a small fraction of files consistently accounted for the majority of code churn across nearly all repositories, regardless of team size or tech stack. Commit patterns were found to correlate more strongly with team size than with team quality, while branch ratios proved to be the most stable metric observed. The research concluded that git blame reveals who touched the code but obscures the underlying team processes that shaped it. These findings directly informed the design of gitpulse, an open-source CLI tool built to provide a more complete weekly repository health check covering both structural and security concerns.

0
ProgrammingDEV Community ·

internetspeedtest.net releases open dataset of global speed test results by country and ISP

The operator of internetspeedtest.net has open-sourced aggregated internet speed data collected from the site's free, LibreSpeed-based tool. The first release covers January through August 2026 and includes average, median, and percentile statistics for download speed, upload speed, and latency, grouped by country and ISP. Data is published as monthly JSON files on GitHub, Zenodo, Kaggle, and Hugging Face under a CC BY 4.0 license. The creator cautions that the sample is self-selected and uneven, with country and ISP derived from IP lookup rather than verified sources. Minimum sample thresholds — 200 tests globally, 30 per country, and 20 per ISP — are enforced before any aggregate is published.

0
ProgrammingDEV Community ·

Bifrost Open-Source AI Gateway Streams LLM Audit Logs to Enterprise SIEMs

Security teams face a growing blind spot as LLM traffic often bypasses corporate monitoring by flowing directly from microservices to third-party model providers. Bifrost, an open-source AI gateway built in Go by Maxim AI, addresses this by centralizing multi-provider model routing and generating immutable, HMAC-signed audit trails. The gateway natively exports structured telemetry to major SIEM and log platforms including Splunk, Datadog, Microsoft Sentinel, Kafka, and cloud storage services. Granular content controls allow organizations to sanitize sensitive prompt data while retaining searchable metadata, supporting compliance with regulations such as HIPAA and PCI DSS. The solution aims to give security operations teams real-time visibility into prompt injection attempts, unauthorized data egress, and agent behavior across enterprise AI deployments.

0
ProgrammingDEV Community ·

CLI Tool gitpulse Maps Real Codebase Ownership Using Git History and Impact Scores

A developer tool called gitpulse claims to identify who truly maintains a codebase by analyzing git history rather than relying on org charts or ownership files. Instead of counting raw commits, it measures contributor impact by weighing lines changed across distinct files, with extra weight given to frequently modified 'hotspot' files. Running a single command over a quarterly period can reveal who owns high-churn files, which contributors are ramping up, and who may be becoming a single point of failure. The tool also surfaces patterns such as late-weekend commit clusters that may indicate a team under stress, insights that raw git logs alone do not provide. The article positions gitpulse as a practical, terminal-based analytics instrument distinct from version control systems, offering actionable decisions rather than just event logs.

0
ProgrammingDEV Community ·

How to Add Automated Secret Scanning to GitHub Actions Using Dotguard

Developers can integrate the open-source tool Dotguard into GitHub Actions using a single YAML block to automatically scan repositories for exposed secrets on every pull request or push. The tool checks .env files, config files, and source code for leaked credentials, including cloud keys, tokens, and high-entropy strings tied to sensitive variable names. When a secret is detected, the CI build fails and generates a JSON report pinpointing the exact file and line, making remediation straightforward. False positives can be handled through documented exceptions rather than disabling the scanner entirely, preserving the integrity of the security check. The article argues that the cost of running such a scan is negligible compared to the potential six-figure financial and reputational damage caused by a leaked credential.

0
IndiaTimes of India ·

Ex-cricketer backs Sanju Samson to replace Ruturaj Gaikwad as CSK captain

Discussions are underway about a potential captaincy change at Chennai Super Kings ahead of the 2027 IPL season. Ruturaj Gaikwad's performances have drawn scrutiny, prompting questions about his suitability to continue leading the side. Former cricketer Sadagoppan Ramesh has publicly endorsed Sanju Samson as a strong replacement, citing his experience and a notable 50% win rate as an IPL captain. Beyond the captaincy question, CSK also faces decisions regarding the future of their coaching staff. The role of franchise icon MS Dhoni in the team's setup remains another key matter for the organisation to resolve.

0
IndiaTimes of India ·

Delhi influencer Swatantra Bhardwaj detained after viral video of assault boast

Social media influencer Swatantra Bhardwaj was detained by Delhi Police after a video of him boasting about assaulting a protester's father spread widely online. In the video, he claimed responsibility for causing severe injuries to the victim, reportedly requiring multiple stitches. His social media profiles drew additional scrutiny, revealing provocative content and claims of closeness to political figures. The detention came after Delhi Police assured protesters that action would be taken against him.

0
ProgrammingDEV Community ·

Developer Shares Lessons on Secret Detection Rules and Real-World Coding Habits

A developer building Dotguard, an open-source secret-scanning tool, documented how writing each detection rule revealed distinct habits developers have around handling sensitive credentials. Common patterns observed included pasting authentication tokens into code for debugging and generating strong keys but storing them in plaintext files with obvious variable names. The project was designed with zero external dependencies and no network calls, making it fully auditable and suitable for restricted or air-gapped environments. False-positive suppression logic highlighted the challenge of balancing detection sensitivity with team trust, since a scanner that triggers too many false alarms risks being disabled entirely. The developer recommends distributing scanner hooks through version-controlled repository files so every new contributor automatically inherits the security behavior on first clone.

0
IndiaNDTV ·

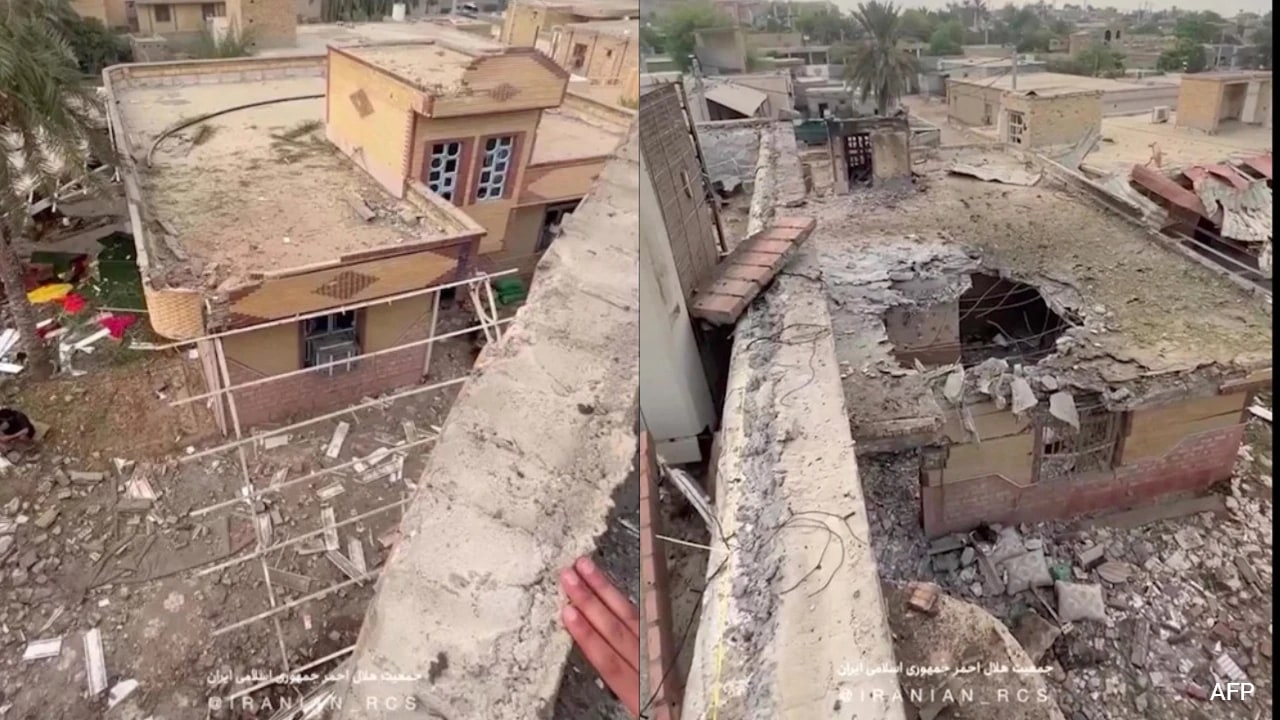
US Strike on Iran Kills 5, Injures 60 at Wedding in Hormozgan Province

A US military strike hit two residential homes in Iran's southern Hormozgan province during a wedding celebration. The attack killed at least five people and left more than 60 others injured. Witnesses described the moment of impact, recounting how celebratory ululations were suddenly interrupted by a loud explosion. The strike targeted a gathering of families in what was otherwise a festive occasion.

0
ProgrammingDEV Community ·

Developer Builds Free Client-Side SEO and Social Media Preview Tool

A developer has launched OmniSEOtools, a free, open-source suite of SEO and meta tag testing utilities that runs entirely in the browser with no server-side processing. The tool includes previews for Twitter/X cards, Google SERP snippets, and LinkedIn post displays. Built with Next.js App Router and Tailwind CSS, it aims to address the slowness and paywalls common in existing social preview debuggers. Because all processing happens client-side, users get instant feedback without waiting on remote servers. The project is publicly available on GitHub, and the developer is seeking community input on additional SEO utilities to include.

← NewerPage 791 of 4469Older →