SShortSingh.
0
ProgrammingDEV Community ·

How to Design Secure Server-Rendered Login Sessions for EdTech Apps

A software developer has outlined a structured approach to handling authentication in server-rendered educational applications, emphasizing that session creation, verification, refresh, and logout should each be treated as distinct state transitions. The design recommends issuing a short-lived session cookie only after a phone verification code is confirmed, with the server maintaining full control over the session lifecycle and audit trail. A key concern addressed is account recovery in school settings, where a learner may lose their phone while a parent, teacher, or administrator still needs safe access to recover the account. The browser receives only an opaque HttpOnly cookie, keeping the underlying session store — whether SQL, Redis, or another service — invisible to the client. The article also provides a Python transport adapter that centralizes endpoint logic and ensures the application, not the auth provider, determines when each session transition is permitted.

0
ProgrammingDEV Community ·

Why Security Teams Must Shift From Gut Instinct to Metrics-Driven Decisions

Security programs have long relied on intuition rather than measurable outcomes, but growing attack surfaces and tighter budgets are forcing a change in approach. Metrics-driven security means defining success numerically before deploying controls, tracking the same data consistently over time, and actually letting those numbers drive program decisions. Common pitfalls include measuring activity instead of outcomes, using vanity metrics, and tracking too many numbers without clear ownership. Key areas worth monitoring include mean time to detect and respond to incidents, vulnerability patching speed, privileged account MFA coverage, and phishing simulation trends. Organizations are advised to select a small set of metrics aligned to their specific threat model and business priorities rather than adopting a one-size-fits-all list.

0
ProgrammingDEV Community ·

Cloudflare silently injects analytics beacon; developer's CSP blocks it at the edge

A developer discovered that Cloudflare's Web Analytics feature automatically injects a tracking beacon script into HTML responses at the edge, without modifying the origin source files or build output. The script, beacon.min.js, is added by default when a site is connected to Cloudflare, and does not appear in any local templates, dependencies, or compiled files. The site's Content Security Policy blocked the script before it could execute, returning a status of -1 with zero bytes transferred. Rather than whitelisting the Cloudflare analytics host — which would have contradicted the site's stated privacy policy of running no analytics — the developer disabled Web Analytics directly from the Cloudflare dashboard. The developer also flagged an unresolved issue: Cloudflare's Network Error Logging headers still reference an external reporting endpoint, meaning some data may leave the browser even without the beacon script running.

0
ProgrammingDEV Community ·

Founder Grows SaaS Product Buildside to 130 Users in Two Weeks via Public Building

Entrepreneur Uriel Bitton shared how he grew his SaaS product Buildside to 130 users within just two weeks of launch. His primary growth strategy centered on building in public, openly documenting his development journey on social media. The approach attracted an early user base without relying on traditional paid marketing. Bitton published his experience on DEV Community in early September, tagging it under topics including SaaS, founder journeys, and social media growth. His story highlights how transparency and community engagement can serve as effective tools for early-stage startup traction.

0
ProgrammingDEV Community ·

Measure Your Team's Code Review Limits Before AI Pull Requests Overwhelm Them

Researcher Margaret-Anne Storey recently introduced the concept of 'cognitive debt' — the gradual erosion of shared understanding about how a system works — during a DORA community session. A software developer writing on DEV Community argues this debt is quietly accumulating in teams that review AI-generated pull requests at scale, without realising their review process has become ineffective. The author warns that standard delivery metrics like merge rate and time-to-approve can appear healthy even as review quality collapses, masking real risk behind green dashboards. Drawing a parallel to mutation testing in software quality assurance, they propose seeding review queues with known-defective 'canary' pull requests to measure how reliably reviewers catch real problems. They recommend starting with one canary per twenty pull requests, tracked over four-week windows, to establish a statistically meaningful detection rate before cognitive debt causes a serious incident.

0
ProgrammingHacker News ·

Developer Shares Week 6 Progress Building an MMO Through Vibecoding

An independent developer has reached the sixth week of building a massively multiplayer online game using a vibecoding approach, documenting progress on their project called Eldermyr. Vibecoding refers to a development style where code is generated largely through AI assistance with natural language prompts. The project update was shared on Hacker News, attracting community attention. The developer has been providing regular weekly updates on the game's development at eldermyr.com.

0
ProgrammingDEV Community ·

Founder grows Buildside to 130 users in two weeks through building in public

Buildside, a platform for SaaS founders, attracted 130 users within two weeks of launch without a paid advertising budget or large email list. The founder credited the growth to consistently sharing the product's development journey on X and LinkedIn before and after launch, which built an audience invested in the idea before it went live. Rather than waiting for a polished product, early posts focused on the problem being solved, small progress updates, and honest accounts of setbacks, which helped establish trust with potential users. Direct conversations with early users provided feedback that shaped the product through a repeating cycle of sharing, listening, and improving. The experience reinforced a widely cited startup principle — that early, transparent communication with potential customers produces better products and more committed early adopters.

0
IndiaNDTV ·

Rubio Warns All Nations Against Helping Iran Evade US Sanctions

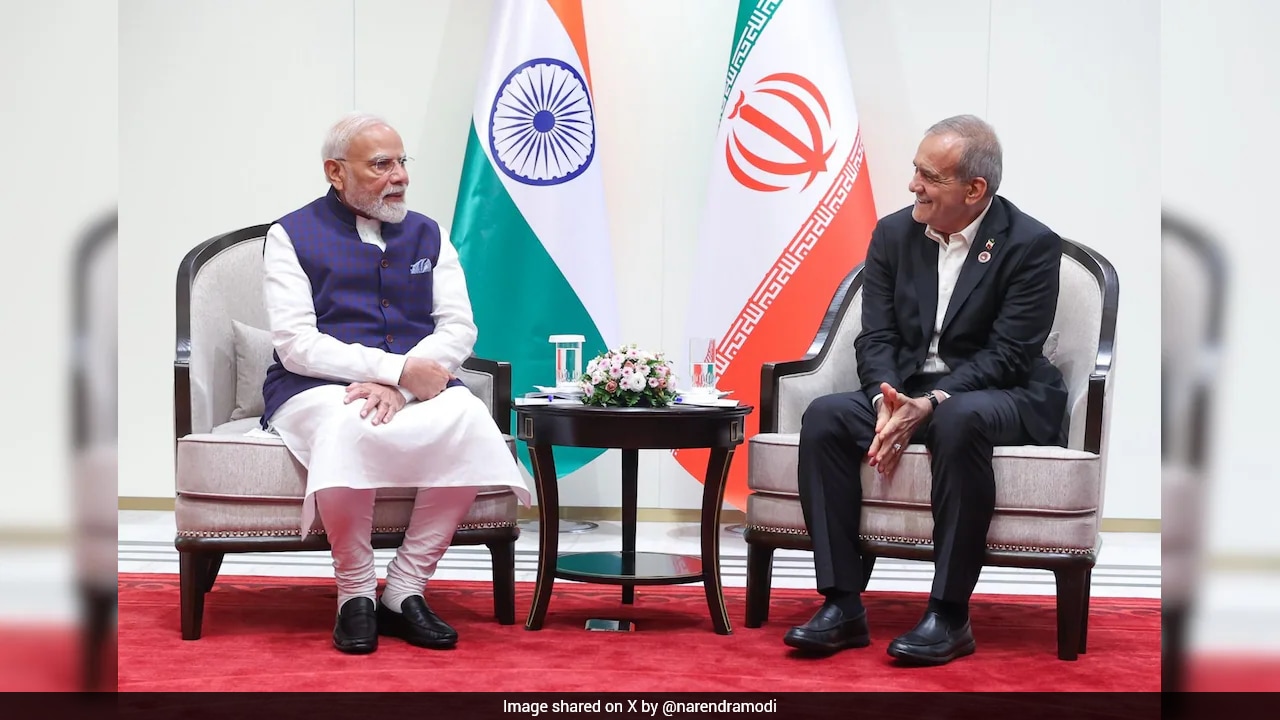
US Secretary of State Marco Rubio issued a stern warning that no country should assist Iran in circumventing American sanctions. The warning came after Indian Prime Minister Narendra Modi met with Iranian President Masoud Pezeshkian. Rubio reiterated a position previously stated by President Donald Trump, signaling a firm US stance on Iranian economic isolation. Washington is particularly concerned about efforts by any nation to help Tehran establish alternative revenue channels. The warning appears directed broadly at countries maintaining diplomatic and economic ties with Iran.

0
ProgrammingDEV Community ·

A Simple CSS Pattern to Style HTML Dividers Consistently Across Browsers

The HTML <hr> element renders as a horizontal rule by default, but browser-default styling often produces inconsistent or unintended results when developers try to customize it. A reliable fix involves resetting the default border to zero before applying a custom border-top, which gives developers precise control over the divider's appearance. Additional properties like width, max-width, and margin help keep the divider proportional and centered on both narrow and wide screens. The <hr> tag also carries semantic meaning, representing a thematic break in content, making it preferable to empty <div> elements when separating distinct sections. Developers are advised to use <hr> only when content genuinely shifts topic, reserving styled divs or CSS pseudo-elements for purely decorative lines.

0
ProgrammingDEV Community ·

JWKS vs Session Verification: How API Trust Boundaries Affect Account Recovery

JWKS verification and session verification serve distinct roles in securing API requests, particularly in customer support and account recovery scenarios. JWKS verification validates a token's signature using a public key set, making it suitable for high-volume, distributed systems without exposing private key material. Session verification goes further by confirming whether a specific session remains valid at the moment of the request, accounting for revocation or policy changes since the token was issued. Most customer-support systems require both methods, with a clear recovery policy defining when each applies — such as requiring session verification for password resets or agent-assisted recoveries. Proper key rotation management, including bounded caching, refresh triggers, and failure telemetry, is essential to maintaining both security and availability in production environments.

0
ProgrammingDEV Community ·

Developer Ditches AI Shortcuts to Build Arch Linux Workspace From Scratch

A developer chose to learn Arch Linux manually as a deliberate effort to rekindle a passion for learning that he felt was eroding due to over-reliance on AI tools. He installed Arch Linux alongside Windows 11 in a dual-boot setup on his gaming PC, which is equipped with an Nvidia RTX 5050 GPU and an AMD Ryzen 5 CPU. Key challenges included configuring Windows Secure Boot and installing the correct GPU and CPU drivers using the pacstrap utility. After a successful installation, he opted for the Hyprland compositor over a traditional desktop environment, drawn by its tiling window management and modern animations. The project serves as a personal learning exercise rather than a tutorial, with the author pointing readers to existing Arch Wiki resources for installation guidance.

0
ProgrammingDEV Community ·

Developer Builds Python Static Analysis Tool Using Only Standard Library

A developer created Proofline, a pure Python static analysis tool, as an entry for the Zero Dependency Hackathon 2026, using no third-party libraries whatsoever. The tool parses Python code via the built-in AST module to map functions, classes, call graphs, and file changes, aiming to assess the potential impact of code modifications. Instead of GitPython, it detects file changes using SHA-256 hashing via pathlib and hashlib, and replaces NetworkX with a simple adjacency list to model function call relationships. A built-in HTTP server with Server-Sent Events powers the dashboard, while a custom Git pre-commit hook automates verification without the pre-commit package. The project highlighted key limitations of static analysis, particularly around dynamic dispatch patterns like getattr calls, which AST alone cannot fully resolve at runtime.

0
ProgrammingDEV Community ·

Developer discovers 8 months of browser memory benchmarks were measuring wrong process

A developer behind the Kestrel browser project has disclosed that memory usage figures published eight months ago were fundamentally flawed due to a faulty measurement instrument. The original post claimed Kestrel held 121.7 MB versus an unmanaged browser's 319.9 MB; corrected figures show 345.9 MB against 255.3 MB, with the tool exceeding its memory budget in 85% of samples. The error stemmed from using ps output to attribute memory per browser tab, which inadvertently captured WebContent processes belonging to unrelated apps like Safari or Electron. A single Jira page was logged at 52 MB when the actual rendering process consumed 511 MB — the recorded figure belonged to a completely different application. The fix now tracks all WebContent processes younger than the current browser session, eliminating the need for per-tab attribution entirely.

0
ProgrammingDEV Community ·

How to Read an ER Diagram: Tables, Keys, and Relationships Explained

An entity-relationship (ER) diagram visually represents a database's tables, columns, and the connections between them. In such diagrams, boxes denote tables, bold headings indicate table names, and lines between boxes represent foreign-key relationships. Symbols at each end of a line specify the cardinality — one-to-one, one-to-many, or many-to-many — with the last type typically resolved using a join table. Common pitfalls include assuming all relationships are one-to-many, overlooking nullable columns, and misreading the direction of foreign keys. Tools like dbdiagram.io can auto-generate ER diagrams from a database connection string, making schema visualization accessible without manual effort.

← NewerPage 776 of 4332Older →