0
0
0
ProgrammingHacker News ·
Open-source 15 MB self-hosted media server offers Netflix- and Spotify-style streaming
A developer has shared a self-hosted project called HolyArrs on Hacker News, positioning it as a lightweight alternative to commercial streaming services. The tool is described as roughly 15 MB in size and is designed to run on a user's own media server. It aims to provide video and music playback experiences comparable to Netflix and Spotify. The post, which was shared as a Show HN submission, gathered 9 points and 2 comments at the time of reporting. The source material available does not include further technical details about features or supported platforms.
0
IndiaNDTV ·
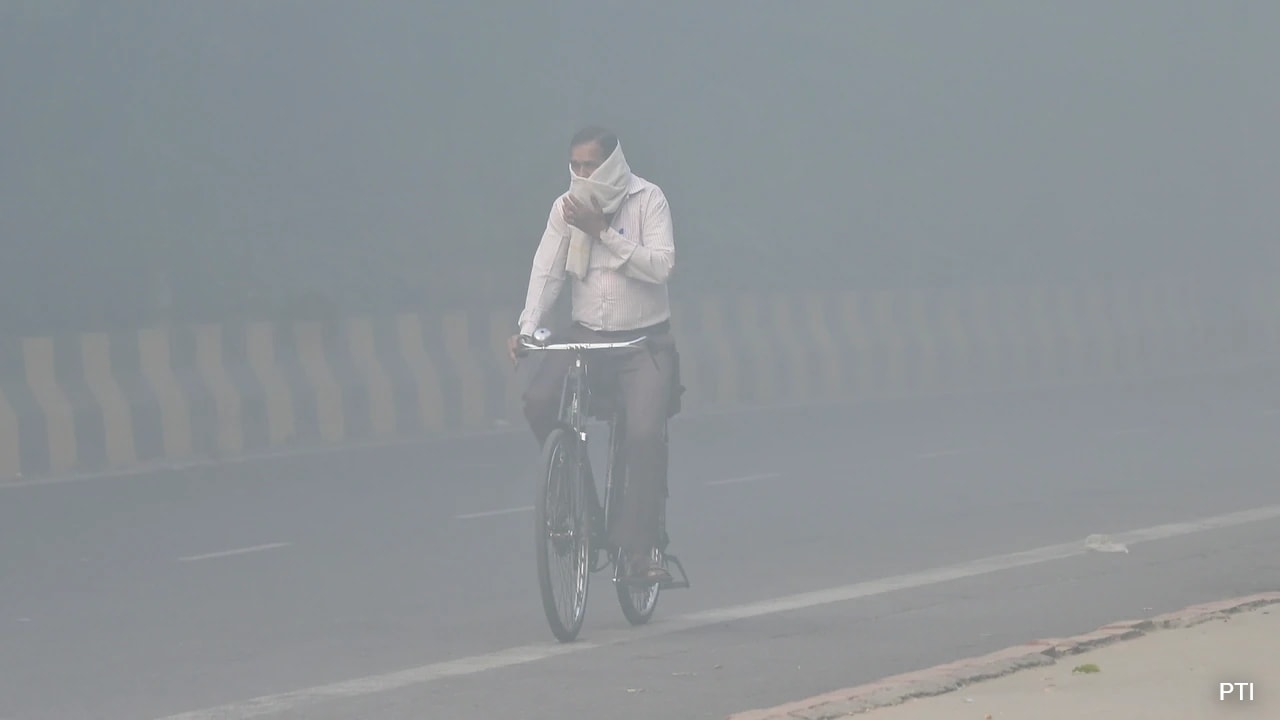
Delhi's Annual Clean Air Battle Exposes Data Gaps and Weak Rules
Diwali this year ranked as the fourth most polluted day of the entire year in Delhi. Daily average PM2.5 concentration reached 257 micrograms per cubic metre on that day. The report points to blindspots in air quality data and weaknesses in current regulations. Together these gaps are hindering efforts to tackle the city's recurring pollution crisis.
0
ProgrammingDEV Community ·
Capgo, Expo EAS and Codemagic lead 2026 options for solo mobile app deployment
A roundup of 2026 mobile deployment platforms for solo developers ranks tools on building iOS and Android apps, submitting them to app stores, and pushing live updates. The article, written by Capgo's founder, names Capgo as the top all-in-one choice for Capacitor and Ionic apps, starting at $14 a month, and notes it needs no Mac for iOS builds. Other options covered include Expo EAS for React Native, Codemagic's free macOS minutes, Capawesome Cloud, Bitrise, and GitHub Actions. Several services are being retired, including Ionic Appflow for new apps and App Center/CodePush, which shut down in March 2025. The author states that prices were checked on each vendor's pricing page in November 2026.
0
0
ProgrammingDEV Community ·
Keeva Uses Client-Side Encryption and Walrus Memory to Persist a Credential Vault
A developer has written up Keeva, a credential vault built for the Total Recall hackathon, which stores passwords, API keys, and private notes. The design encrypts records in the browser so that storage only ever receives ciphertext, with decryption possible only after explicit user authorization. Keeva divides responsibilities among a Sui wallet for authorization, Walrus Memory for persistent encrypted storage, and Tatum for blockchain reads and transaction checks. Encryption relies on AES-256-GCM with per-operation random IVs, PBKDF2-SHA256 key derivation, and context binding so that mismatched records fail to decrypt. The article also addresses harder persistence problems, such as password changes, conflicting edits across devices, and unacknowledged storage writes.
0
ProgrammingDEV Community ·
Wrong Instance Family Wastes Cloud Spend Even When Correctly Sized
Right-sizing tools typically focus on whether cloud resources are too big or too small, but a third kind of mismatch, using the wrong instance family for a workload's resource profile, is often overlooked. An instance can show reasonable utilization numbers while its CPU-to-memory ratio is wrong for what the workload actually does. For example, a memory-heavy workload on a compute-optimized instance can waste money on unused compute capacity while delivering weaker memory performance. Catching this requires understanding the application's access patterns rather than relying solely on usage history. The article notes that family selection is the step most commonly skipped by teams that simply apply recommender suggestions.
0
ProgrammingDEV Community ·
Using DevTools Event Listener Breakpoints to Trace Elusive UI Bugs
A developer describes debugging a web app where a menu click caused unexpected modal behavior, with no console errors and handlers scattered across dynamic and third-party code. Regular breakpoints and logging proved ineffective because the relevant event handlers were hard to locate. The author turned to Chrome DevTools' event listener breakpoints, which pause execution whenever a chosen event type's listener is invoked, regardless of where the handler lives. The feature is found in the Sources panel's sidebar, organized by event category with a filter for quick lookup. In one case involving a hover tooltip, setting breakpoints on mouseenter and mouseleave revealed a cleanup timer that was never cleared, explaining the lingering tooltip. The article recommends combining this technique with call stack inspection to understand event propagation.
0
ProgrammingDEV Community ·
Tamper-evident track record uses SHA-256, git and Bitcoin timestamps
A team needed a way to show its forecasts were made before outcomes were known, without requiring readers to take its word for it. Each night, the day's scores are saved to a CSV file before the next market open, and the file's SHA-256 fingerprint is logged with a publication time. The file and ledger are pushed to a public git repository, and the file is also timestamped via OpenTimestamps, which anchors its hash in a Bitcoin transaction independent of GitHub. Any alteration to the file would change its fingerprint, while corrections are added as new entries in a public log rather than edits to existing data. The article notes a practical pitfall, where git line-ending normalisation can alter file bytes, and suggests a .gitattributes rule to prevent this. The approach is presented as an educational, not investment-advice, transparency method.
0
ProgrammingDEV Community ·
NestJS Core Architecture: Modules, Controllers, Providers and Dependency Injection
NestJS is a Node.js framework that uses a modular architecture to build scalable, maintainable backend applications. Its code is organized into Modules, Controllers and Providers, with Dependency Injection handling dependency creation so developers don't instantiate objects manually. Modules, decorated with @Module(), group related functionality such as users, posts or authentication, and each declares its controllers, providers, imports and exports. Controllers handle incoming HTTP requests through decorator-defined routes and delegate work to services, which hold the business logic and are injected into other components. Separating controllers from services improves reusability, maintainability and unit testing.
0
ProgrammingDEV Community ·
A small serverless SaaS on AWS cost 74 cents in October, mostly fixed fees
A developer running a small SaaS on AWS with Lambda, DynamoDB and CloudFront shared the real bill for October, the product's launch month. The total was $0.74, filtered by a resource tag, with Route 53 and KMS fixed charges making up most of it. Compute, database and CDN usage all fell within free tiers, and the largest variable cost was S3 requests, largely from the owner's own deployments and log downloads. Email and AI summary costs were not visible under the tag, since SES had no line item and Bedrock calls were untagged. The author notes that most costs scale with usage, while the hosted zone and encryption key charge regardless of traffic.
0
ProgrammingDEV Community ·
Kubernetes Pods Can Run Without Being Ready: A Hands-On Troubleshooting Lab
A Kubernetes Pod can be in the Running phase while its readiness condition is False, meaning the container is alive but not yet fit to receive traffic. A hands-on experiment using an NGINX Deployment, a ConfigMap, a readiness probe, and a Service was run in an isolated Minikube environment on Kubernetes v1.30.0 to demonstrate this. The setup used an exec readiness probe that checks a mounted file for the exact value 'ready', so changing that value to 'blocked' causes the probe to fail without stopping or restarting the container. The author's goal was to observe how Kubernetes responds to a Pod becoming unready and then restore readiness without a container restart. The lab also points out why this distinction matters in production, since a running container does not guarantee a ready application.
0
ProgrammingDEV Community ·
Developer details moving email domain from DMARC monitoring to quarantine without breaking mail
A developer whose app sends invitation, password-reset and alert emails found that a DMARC policy of p=none left the domain open to forged messages, since receivers were told to take no action on failures. Setting up SPF, DKIM and DMARC together required fixing an SPF record that exceeded the ten-lookup limit by one, which was flattened to five lookups. Signing was added to the Nodemailer transport using a private key stored base64-encoded, with the new public key published in DNS before the private key was deployed during rotation. After confirming the key pair matched, the policy was raised to p=quarantine on 12 September, sending failing mail to spam rather than rejecting it. The author chose to hold off on configuring the subdomain policy tag.

0
BusinessEconomic Times ·
Sonia Gandhi calls 1984 anti-Sikh riots a shameful chapter in India's history
Congress leader Sonia Gandhi has described the 1984 anti-Sikh riots as a shameful chapter in the country's history. The remarks reflect the party's continued acknowledgment of the violence that followed the assassination of Prime Minister Indira Gandhi. Gandhi's statement comes amid ongoing political discussion about accountability for the riots. The article text provided was empty, so the summary is based only on the original headline.
0
0
BusinessEconomic Times ·
Lori Huang's $9.1B Foundation Expands Charitable Giving
Lori Huang, the wife of Nvidia CEO Jensen Huang, is associated with a foundation valued at $9.1 billion. The foundation supports a range of charitable initiatives. Details about the specific programs and recipients are central to understanding its reach. The article examines how the foundation's resources are being deployed for philanthropic causes.
0
ProgrammingHacker News ·
Anthropic Begins Investor Roadshow for Proposed IPO
Anthropic has launched a roadshow to present its proposed initial public offering to prospective investors. The announcement was posted on the company's official news page. The source material gives few additional details about the offering's size, timing, or valuation. The news drew modest attention on Hacker News, where it received 15 points and 13 comments.
0
0
IndiaTimes of India ·
Former Navy SEAL pays $1,000 fine after felony charges over lakefront tree removal are dropped
A retired Navy SEAL commander in New Hampshire has paid a $1,000 fine. Two felony charges tied to the removal of a boundary hemlock tree were dropped as part of the outcome. Neighbours had valued the hemlock and a nearby stump at $11,259. An assessment commissioned by the accused, Hayes, concluded that the remaining trees had no positive market value.