SShortSingh.
0
ProgrammingDEV Community ·

Anthropic Launches Claude Opus 5.5 at 40% Lower Cost With Improved Performance

Anthropic released Claude Opus 5.5 on September 22, positioning it as their most capable model to date while cutting overall task costs by approximately 40 percent compared to its predecessor. The price reduction stems from both lower per-token rates and the model's ability to complete tasks using fewer tokens. Cache read pricing dropped sharply from $0.50 to $0.20 per million tokens, a change seen as especially significant for long-running agent workflows that repeatedly access large contexts. On the same day, OpenAI also launched two lower-cost models, signaling that competition in the AI industry has shifted toward cost-efficiency per completed task rather than benchmark scores alone. Opus 5.5 is available via Anthropic's API as well as on AWS, Google Cloud, and Microsoft platforms, though teams running production agent systems are advised to test thoroughly before upgrading due to several behavioral changes in the model.

0
ProgrammingDEV Community ·

Anthropic and OpenAI Cut AI Prices on the Same Day in Rare Pricing Showdown

On September 22, 2026, Anthropic and OpenAI released competing AI models within hours of each other, both accompanied by significant price reductions — an unprecedented same-day rivalry. Anthropic launched Claude Opus 5.5 at $4 per million input tokens and $20 per million output tokens, a 20% drop from its predecessor, with cache read costs slashed by 60%. OpenAI countered with GPT-6 Sol at $2 input and $10 output per million tokens, and the budget-tier GPT-6 Luna at just $0.10 input and $0.50 output — roughly half the cost of the GPT-5.6 models they replace. For a typical cache-heavy agentic workload, GPT-6 Sol works out to roughly 47% cheaper than Opus 5.5, while Luna is nearly negligible in cost. Both companies described their new prices as permanent, signaling a broader industry shift toward competing on cost rather than benchmark performance alone.

0
ProgrammingDEV Community ·

AI Video Avatars Set to Replace Webcams in Meetings and Streams by 2026

Real-time AI video avatars that mirror a user's facial expressions are becoming mainstream across platforms like Zoom, Microsoft Teams, and Discord in 2026. Advances in hardware — including Apple M2-Pro, Nvidia RTX 4090, and AMD MI300 chips — now allow neural rendering at 60 frames per second on consumer laptops. Both commercial tools such as Meta Avatar Studio and Ready Player Me, and open-source options like Avatarify, support integration with major video-call apps via virtual webcam drivers. Privacy regulations are also evolving, with the EU Digital Identity Act of 2025 requiring explicit user consent and on-device biometric processing where possible. Growing interest has been further fueled by the upcoming FIFA World Cup 2026, where broadcasters are deploying multilingual AI presenters using the same underlying technology.

0
ProgrammingDEV Community ·

CLOSEDQUORUM Malware Uses Four AI Models to Vote on Attack Actions Against Windows

Cisco Talos researchers have statically analyzed a Go-based Windows implant called CLOSEDQUORUM, which sends host information to up to four commercial large language models — DeepSeek, Qwen, Mistral, and Google Gemini — and executes whichever attack action receives the most votes. Capabilities built into the implant include credential theft from LSASS memory, browser data and cryptocurrency wallet harvesting, process injection, and persistence via Registry Run keys, scheduled tasks, or WMI subscriptions. Collected data is encrypted with AES-256-GCM, split into segments, and exfiltrated to a Discord webhook. The publicly available version contains placeholder API keys and webhooks, meaning it is non-functional as distributed, and no real-world deployment has been confirmed. The threat actor behind CLOSEDQUORUM remains unidentified, and no CVEs are associated with this implant.

0
ProgrammingDEV Community ·

On-Device AI Hits Real-Time Speed, Challenging Cloud-First Smartphone Model

A proof-of-concept system has demonstrated that a full Gemma 4 language model can run entirely on an Android handset without any server connection, using Google's LiteRT-LM runtime and a .litertlm container format. The prototype was tested on a OnePlus 15 in airplane mode and sustained generation at roughly 40 tokens per second, a rate researchers describe as feeling instant to human users. The system works by loading the model into shared memory and exposing it as a private inference service available to all apps on the device, eliminating repeated cloud calls. Key enabling techniques include quantization, pruning, distillation, and a Matryoshka Transformer architecture that reduces effective memory use without cutting parameter count. The researchers argue this shifts the main bottleneck in on-device AI from hardware capability to software architecture, raising fresh questions about cloud dependency, data privacy, and inference costs at scale.

0
ProgrammingDEV Community ·

Oracle SQL Pseudo-Columns Explained: Types, Uses, and Key Limitations

Oracle SQL pseudo-columns behave like table columns but are not physically stored on disk, meaning they can be queried with SELECT but cannot be modified via INSERT, UPDATE, or DELETE. Built-in pseudo-columns include ROWID for unique physical row addressing, ROWNUM for sequential row numbering, NEXTVAL and CURRVAL for sequence management, and ORA_ROWSCN for tracking data changes via System Change Numbers. For hierarchical queries using CONNECT BY, Oracle provides additional pseudo-columns such as LEVEL, CONNECT_BY_ISLEAF, CONNECT_BY_ISCYCLE, and SYS_CONNECT_BY_PATH to navigate and inspect tree structures. A common pitfall involves ROWNUM, which is assigned after the WHERE clause but before ORDER BY, making direct filters like ROWNUM > 1 unreliable without using a subquery. Unlike ROWNUM, ROWID is a permanent physical address that persists across transactions, and while ROWID cannot be indexed directly, ROWNUM cannot be indexed at all; custom pseudo-columns are not supported, though Oracle 11g introduced virtual columns as a logical alternative.

0
ProgrammingDEV Community ·

Developer builds policy-as-code audit tool to verify if AI agent runs were permitted

A developer has added a policy-as-code audit feature to the open-source project agent-lab-trust, designed to check whether AI agent runs complied with declared rules — not just whether they succeeded. The tool evaluates cost caps, call limits, required output artifacts, and forbidden markers, then generates a canonical audit hash for each run. Testing across 13 archived synthetic GenMentor runs showed that a mismatched default contract failed all 13, while the correctly declared GenMentor contract passed all 13 — with the underlying data unchanged. The project distinguishes between operational dashboards that show what happened and governance tooling that shows what was permitted under a specific policy. The tool is reproducible via Docker and is the third installment in a series on making AI agent behavior verifiable and auditable.

0
ProgrammingDEV Community ·

D-Link DIR-822A Router Hit by Two High-Severity Flaws, Patches Pending

D-Link has disclosed two critical vulnerabilities in its DIR-822A router running firmware A_101, assigned CVE-2026-86296 (CVSS 10.0) and CVE-2026-86510 (CVSS 9.9). The first flaw allows an unauthenticated attacker on the local network to trigger a stack-based buffer overflow via a crafted DHCP packet, while the second enables a low-privileged user to cause an out-of-bounds write through L2TP processing. Both vulnerabilities could lead to router crashes, memory corruption, or potential loss of confidentiality and integrity. Public proof-of-concept code exists for both flaws, though real-world exploitation and stable code execution have not yet been confirmed. D-Link is investigating the scope and developing firmware fixes, urging users in the meantime to restrict remote access, block untrusted local devices, and disable L2TP/L2TPv6 WAN connectivity if not needed.

0
ProgrammingDEV Community ·

Tool 'didrun' Exposes Silent CI Failures When Exit Code 0 Masks Empty Test Runs

A developer tool called 'didrun' addresses a longstanding gap in test automation where exit code 0 is returned even when no tests actually ran, giving a false green signal. The tool introduces four distinct exit states — ran-and-passed, ran-and-failed, did-not-run, and ran-and-failed-wrongly — to separately answer whether a check ran, failed, or failed for the right reason. A concrete example shows that running 'go test ./...' on a directory with no test files exits 0 by default, but wrapped with didrun it exits 3, explicitly flagging that nothing was verified. Additional predicates like '--expect-count' and '--wrote PATH' guard against subtler false positives, such as a test suite printing '0 passed' or a stale output file left over from a previous run. The project argues that silently falling back to forwarding an exit code is itself the defect these tools are meant to catch.

0
IndiaNDTV ·

UK Plans to Centre AI Safety Standards at G20 During 2027 Presidency

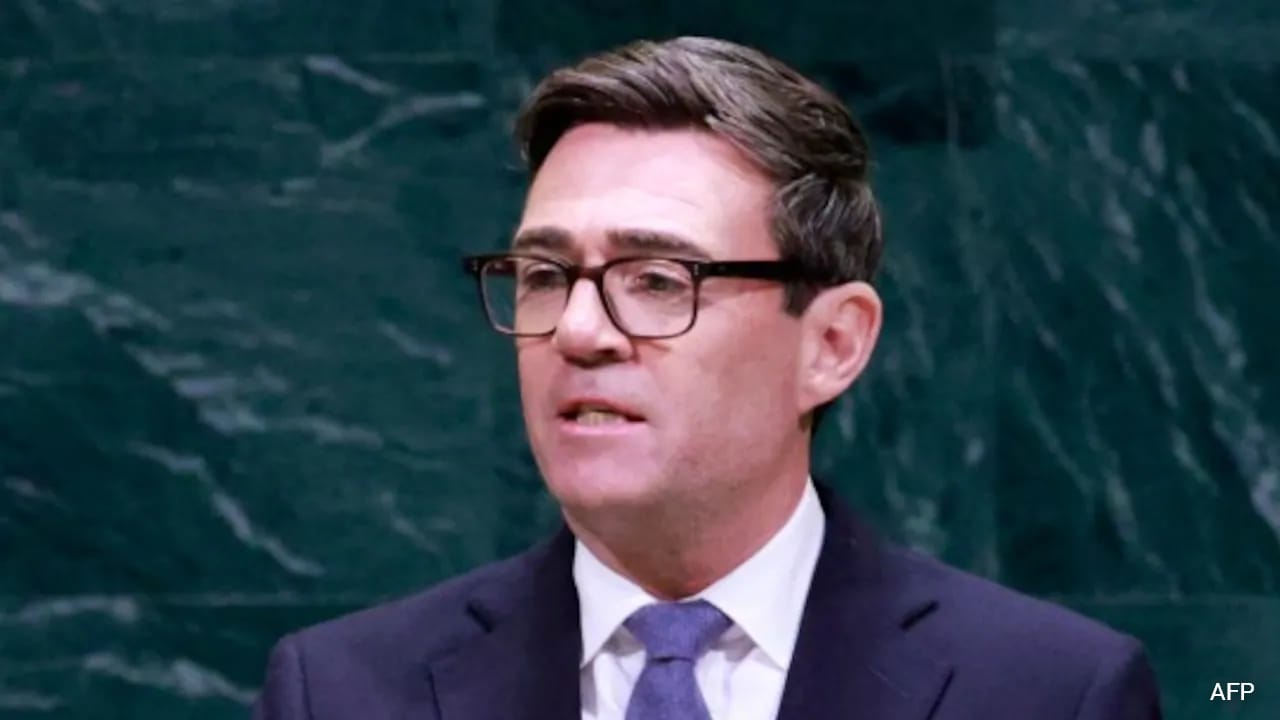
British Prime Minister Andy Burnham has announced that artificial intelligence will be a central focus of the UK's G20 presidency in 2027. The UK intends to use its leadership of the G20 bloc to drive the development of international AI safety standards. Burnham made the announcement highlighting the importance of coordinated global action on AI governance. The G20 groups together the world's major economies, making it a significant platform for shaping global technology policy.

0
IndiaNDTV ·

Trump Holds First Meeting with Venezuela's Interim Leader at UN

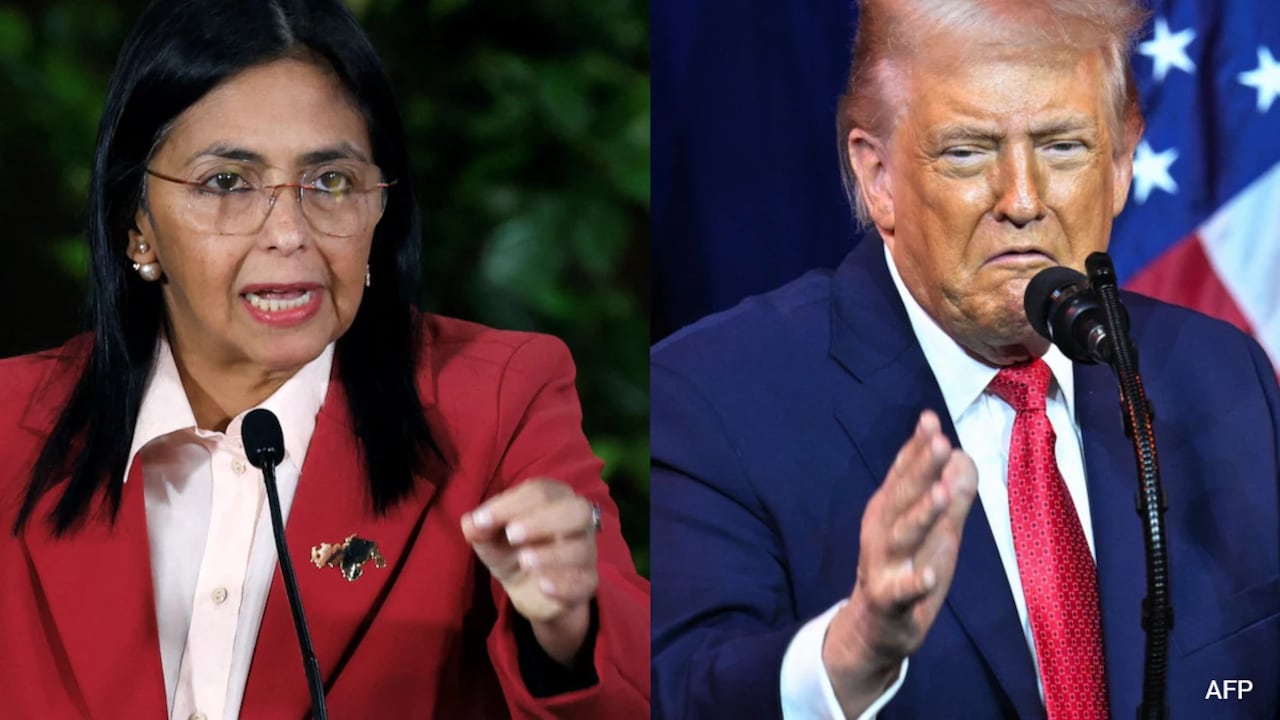
US President Donald Trump met with Venezuelan interim leader Delcy Rodriguez on the sidelines of the United Nations, marking a significant diplomatic encounter. This was the first meeting between a US president and a Venezuelan head of state since former president Nicolas Maduro was captured in a US military raid in January. Rodriguez became Venezuela's acting leader following Maduro's removal from power. The meeting signals a potential shift in relations between Washington and Caracas after years of deep political tensions.

0
ProgrammingDEV Community ·

Kapibala Hackers Steal 18,500+ Government Records via WordPress and Zyxel Flaws

A threat actor tracked as Kapibala, suspected to be Chinese-speaking, breached a Western government organization's database by exploiting a WordPress vulnerability chain combining CVE-2026-63030 and CVE-2026-60137, deploying custom web shells to harvest credentials and access internal SQL databases. The attackers exfiltrated at least 18,566 records containing account details, plaintext passwords, and personally identifiable information linked to government and law-enforcement agencies. Separately, the same actor exploited a stack-based buffer overflow vulnerability in Zyxel GS1900 switches (CVE-2026-7273) to steal device configurations, hashed root credentials, and network data from 996 devices across 48 countries. GreyNoise, which published its findings on September 21, 2026, noted the campaign leveraged shared external infrastructure for continuous scanning and exploitation. CISA has added the relevant CVEs to its Known Exploited Vulnerabilities catalog, and administrators are urged to patch affected systems and monitor for anomalous PHP files, bulk SQL authentication attempts, and unauthorized configuration retrievals.

0
TechnologyBBC Tech ·

Trump allies push 'super intelligence' label for AI, but experts are skeptical

People in Donald Trump's inner circle have begun using the term 'super intelligence' as an alternative label for artificial intelligence. The rebranding effort appears to be driven by those close to the president rather than the broader tech or research community. However, AI experts have expressed doubt that the new terminology will gain widespread traction. The established term 'artificial intelligence' remains deeply entrenched across industry, academia, and public discourse.

0
IndiaNDTV ·

Canada PM Carney Eyes Trade Deal With India, Plans to Host Modi

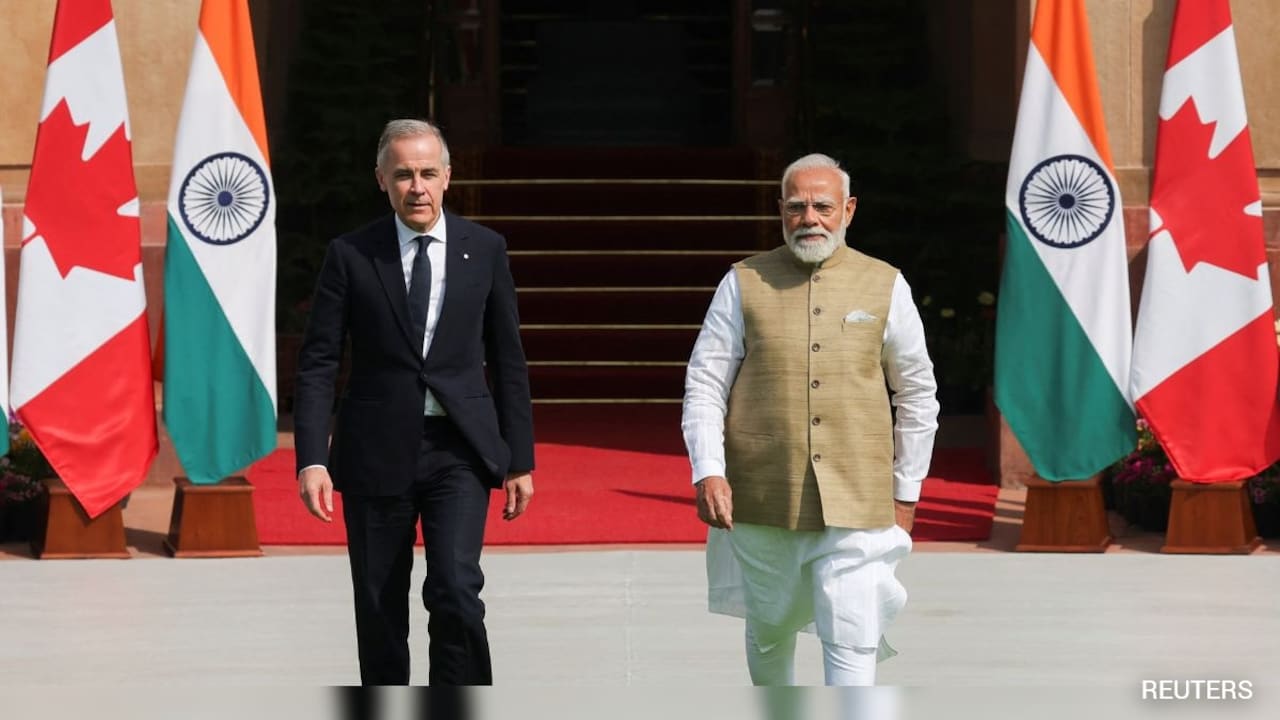
Canadian Prime Minister Mark Carney has expressed eagerness to host Indian Prime Minister Narendra Modi as part of broader trade engagement between the two nations. Carney has set an ambitious goal of doubling Canada's non-US trade over the next decade. India features prominently in Canada's strategy to diversify its trade relationships away from the United States. This push comes amid deteriorating Canada-US relations under President Donald Trump, prompting Ottawa to seek stronger ties with alternative partners.

0
WorldBBC World ·

Hurricane Polo reaches Category 5 strength off Mexico's Pacific coast

Hurricane Polo has rapidly intensified into a Category 5 storm off the coast of Mexico, making it an unusually powerful system for the region. The US hurricane monitoring agency described the storm's sudden strengthening as 'truly remarkable.' Category 5 is the highest classification on the Saffir-Simpson scale, indicating sustained winds exceeding 157 mph. The development raises significant concerns for coastal communities in the storm's potential path.

0
ProgrammingHacker News ·

Waymo Launches Transit Rewards Program Paying Users to Take the Train

Waymo has introduced a Transit Rewards program that incentivizes users to take public transit by offering them payments or credits. The initiative reflects a broader push by the autonomous vehicle company to integrate with existing public transportation networks rather than compete with them. Details of the program, including reward amounts and eligible routes, were outlined on Waymo's official blog in September 2026. The move signals a shift in how ride-hailing and robotaxi companies position themselves within urban mobility ecosystems.

0
ProgrammingDEV Community ·

TrustSink Attack Lets Rogue MFA Providers Steal Passwords in Microsoft Entra ID

Security firm Varonis has disclosed a technique called TrustSink that exploits Microsoft Entra ID's External Authentication Methods feature to steal user passwords during sign-in. An attacker with sufficient privileges, such as a Global Administrator, can register a malicious external MFA provider that intercepts the authentication flow and presents a fake Microsoft password screen to the target user. The rogue provider captures the plaintext password, then returns a valid signed token to Entra so the login completes successfully without raising any visible alert to the user. Varonis demonstrated the attack in a test tenant, though no real-world exploitation has been confirmed as of the disclosure date of September 16, 2026. Recommended mitigations include restricting authentication method modification privileges, monitoring policy changes and consent grants, and adopting phishing-resistant credentials such as FIDO2 or Windows Hello for Business.

← NewerPage 1453 of 6089Older →