SShortSingh.
0
ProgrammingDEV Community ·

FortiGate Central NAT Must Be Configured Before Building Firewall Policies

When migrating firewall policies to FortiGate from Cisco ASA or Palo Alto, administrators must decide between central NAT and per-policy NAT before writing any rules, as FortiOS does not allow switching modes once policies referencing VIPs or IP pools exist. Per-policy NAT is the FortiGate default, but it poorly mirrors the separate NAT table structure used by ASA and PAN-OS, often requiring duplicate translation entries across many policies. Central NAT more closely replicates the source architecture, using a single ordered SNAT and DNAT table independent of firewall allow/deny rules. Attempting to enable central NAT on a box with existing VIP or IP pool references will fail with an error, forcing administrators to dereference every such object before the mode toggle is accepted. Additionally, central NAT changes how destination addresses must be written in policies — rules must reference the internal mapped address rather than the public VIP address, a distinction that can cause hard-to-diagnose failures during cutover.

0
TechnologyTechCrunch ·

Apple Store Creator Ron Johnson Skeptical of AI's Role in Retail Shopping

Ron Johnson, the architect behind Apple's iconic retail stores, has expressed doubt about Silicon Valley's growing confidence in AI-driven shopping experiences. Johnson believes that the true strength of Apple's retail success was never technology alone, but rather its people and human connection. His comments come as major tech companies increasingly bet on artificial intelligence to transform the future of retail. Johnson's perspective offers a contrarian view to the prevailing industry narrative that AI will redefine how consumers shop.

0
ProgrammingDEV Community ·

rekuiper 0.500 moves metadata to RAM, hits 200k msg/s on single core at edge

The rekuiper project, a Rust-based reimplementation of LF Edge eKuiper for IoT edge gateways, has released version 0.500-beta with a major architectural overhaul. Earlier benchmarks showed the engine handling 100,000 messages per second on a single CPU core, but performance degraded at 200,000 msg/s, leaving the true throughput ceiling unknown. Profiling revealed the bottleneck was disk I/O — specifically SQLite metadata lookups and flash storage stalls on embedded devices like industrial gateways — rather than CPU or parsing logic. To fix this, developers rebuilt the engine's internal catalog as an in-memory structure, hydrating all stream and rule metadata from SQLite once at startup and serving subsequent reads entirely from RAM with no filesystem calls. Hierarchical benchmarking at 1,000 msg/s resolution then allowed the team to identify the exact single-core physical throughput limits across multiple real-world MQTT workloads, reaching up to 200,000 messages per second.

0
WorldBBC World ·

India reopens 2020 death case of Bollywood manager Disha Salian

Indian authorities have reopened the 2020 death case of Disha Salian, a celebrity manager in the Bollywood entertainment industry. Salian died in 2020 under circumstances that were initially treated as a suicide or accidental death. Her father has disputed the official account, alleging that his daughter was gang-raped and murdered. The case has attracted renewed public and legal attention following his persistent claims. The reopening signals that investigators are taking a fresh look at the evidence surrounding her death.

0
IndiaNDTV ·

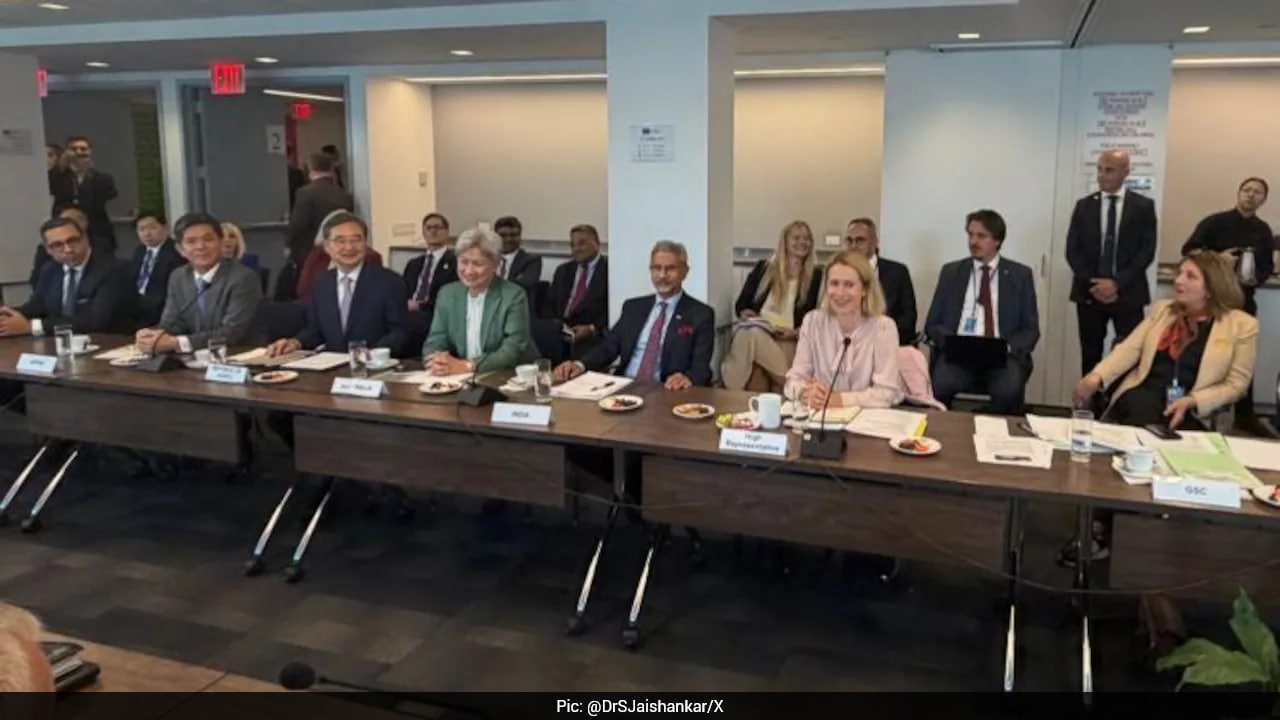
Jaishankar Holds Talks on Ukraine, Gulf Crisis and UN Reform at UN Meet

Indian External Affairs Minister S Jaishankar engaged in diplomatic discussions on the sidelines of the United Nations. The talks covered pressing regional and global concerns, with a particular focus on the ongoing conflicts in Ukraine and the Gulf region. Jaishankar also exchanged views with foreign ministers on key multilateral matters. A significant topic of discussion was the long-debated reform of the United Nations Security Council.

0
ProgrammingDEV Community ·

Developer Builds Zero-Dependency Node.js Tool to Block Secrets Before Git Commits

A developer has released Secret-Scrub, an open-source Node.js CLI tool designed to prevent accidental exposure of API keys and credentials in Git repositories. The tool uses two detection layers: regex-based signature matching for known token formats such as AWS, GitHub, Stripe, and OpenAI keys, and Shannon entropy analysis to catch high-randomness strings without vendor prefixes. It integrates directly as a Git pre-commit hook, automatically blocking any commit that contains a suspected secret before it can be pushed. A staged-only scan mode limits checks to files currently queued for commit, completing the process in under 40 milliseconds to minimise disruption to developer workflows. Secret-Scrub is available on GitHub under the MIT licence and can be installed via a single npx command.

0
ProgrammingDEV Community ·

QuickShare-QR lets developers transfer files to phones via terminal QR codes

A developer has built QuickShare-QR, an open-source Node.js CLI tool that enables instant local file transfers from a computer to a smartphone without cloud services. The tool spins up a temporary HTTP server on the local network, generates a scannable ASCII QR code in the terminal, and begins streaming the file as soon as the phone's camera scans it. Files never leave the local Wi-Fi network, with transfer speeds reaching up to 80 MB/s depending on bandwidth. Security features include path confinement against directory traversal attacks, dynamic ephemeral ports, and optional single-use tokens to restrict download access. The tool requires no permanent installation and can be run directly via npx, with the server automatically shutting down once the transfer completes.

0
ProgrammingHacker News ·

Git Community Eyes Version 2.56 Features and Plans for Major 3.0 Release

The open-source Git version control system has upcoming releases generating discussion in the developer community. Version 2.56 is anticipated to bring incremental improvements to the widely used tool. Beyond that, developers are also looking ahead to a potential Git 3.0, which would mark a significant major release milestone. The topic has been covered by LWN.net and is drawing early commentary from contributors and users. No official release dates have been confirmed at this stage.

0
TechnologyThe Verge ·

Amazon pledges $20M for Colorado River conservation amid data center water scrutiny

Amazon has announced a $20 million investment in water conservation projects along the Colorado River, a vital water source for 40 million people in the western United States. The initiative, launched under a new Colorado River Basin Collaborative, comes as tech companies face growing pressure over the water consumption of their data centers. Amazon has set a goal to become 'water positive' — replenishing more water than it consumes — by the end of the decade. The company has recently shared some data on its water usage, but critics say the disclosure remains incomplete. The full scope of Amazon's water footprint across its operations is still not publicly known.

0
ProgrammingDEV Community ·

Google Expands Gemini Notebook With Code Execution and Cross-Ecosystem Sync

Google rebranded NotebookLM as Gemini Notebook in July 2026 and announced expanded capabilities including notebook code execution and cross-ecosystem syncing. A separate September 2026 update introduced Notebooks in Gemini as a dedicated workspace for schools and organisations. While Google's Studio materials reference generated artifacts and allow users to select them within the Studio panel, no official documentation confirms a redesign or reorganisation of an artifacts tab. Google has not published a rollout timeline or feature details for any such change, making it premature for teams to plan around it. The confirmed story remains Gemini Notebook's broader evolution into a more connected, cross-ecosystem workspace.

0
ProgrammingDEV Community ·

Developer Builds HashDup, a Memory-Safe Duplicate File Finder CLI in Node.js

A developer has released HashDup, an open-source command-line tool built with native Node.js to find and report duplicate files on a system. The tool addresses two common problems with naive duplicate-detection scripts: wasted CPU and disk I/O from hashing every file, and out-of-memory crashes when loading large files into RAM. HashDup uses a two-phase pipeline that first filters files by size using lightweight metadata checks, discarding unique-sized files before any content is read, then applies chunked SHA-256 streaming hashes only to size-matched candidates. By processing files in 64KB buffers rather than loading them whole, the tool keeps memory usage constant at around 30MB regardless of file size. HashDup is available under the MIT license and can be run immediately via npx from the GitHub repository at github.com/mahdyarmonfared/hashdup-cli.

0
ProgrammingDEV Community ·

Dev.to User Calls Out Surge of AI-Generated Posts on the Platform

A Dev.to community member has voiced frustration over what they describe as a near-total flood of AI-generated content on the developer blogging platform. The user argues that LLM-produced writing is easily identifiable due to its unnatural tone and style. They also criticized the length of many posts, suggesting that ideas worth sharing should be expressible in three to four paragraphs. The comment reflects a broader ongoing debate within online writing communities about authenticity and the growing presence of AI-assisted content.

0
ProgrammingDEV Community ·

CleanDrop: Open-Source Node.js CLI Tool Organizes Downloads Folder Safely

A developer has released CleanDrop, a zero-dependency Node.js command-line utility designed to automatically sort cluttered Downloads folders into categorized subfolders. The tool addresses common risks of ad-hoc scripts by offering a dry-run mode that previews all planned file moves without making any changes to disk. CleanDrop also includes an undo command that reverses a sorting batch using a local history log, and it prevents data loss by renaming duplicate files rather than overwriting them. Built entirely on native Node.js filesystem APIs, it requires no npm dependencies and can be run instantly via npx without a global install. The project is open-source under the MIT license and is available on GitHub at github.com/mahdyarmonfared/cleandrop.

0
ProgrammingDEV Community ·

CVE-2026-17633: Authenticated RCE Flaw Found in Langflow OSS Versions Up to 1.10.3

A high-severity remote code execution vulnerability, tracked as CVE-2026-17633 with a CVSS score of 8.5, has been disclosed in Langflow OSS versions 1.0.0 through 1.10.3. The flaw exists in the POST /api/v1/custom_component endpoint, which allows authenticated users to submit arbitrary Python code when the LANGFLOW_ALLOW_CUSTOM_COMPONENTS setting is enabled. The endpoint's security check only verifies whether a user has permission to create custom components, but never inspects the content of the submitted code for malicious instructions. An attacker can exploit this by placing a system command inside a class body, causing it to execute at class-definition time via an unchecked exec() call in the platform's component-building logic. The vulnerability is classified under CWE-94 (Improper Control of Code Generation) and requires no special encoding or bypass techniques to exploit successfully.

0
IndiaNDTV ·

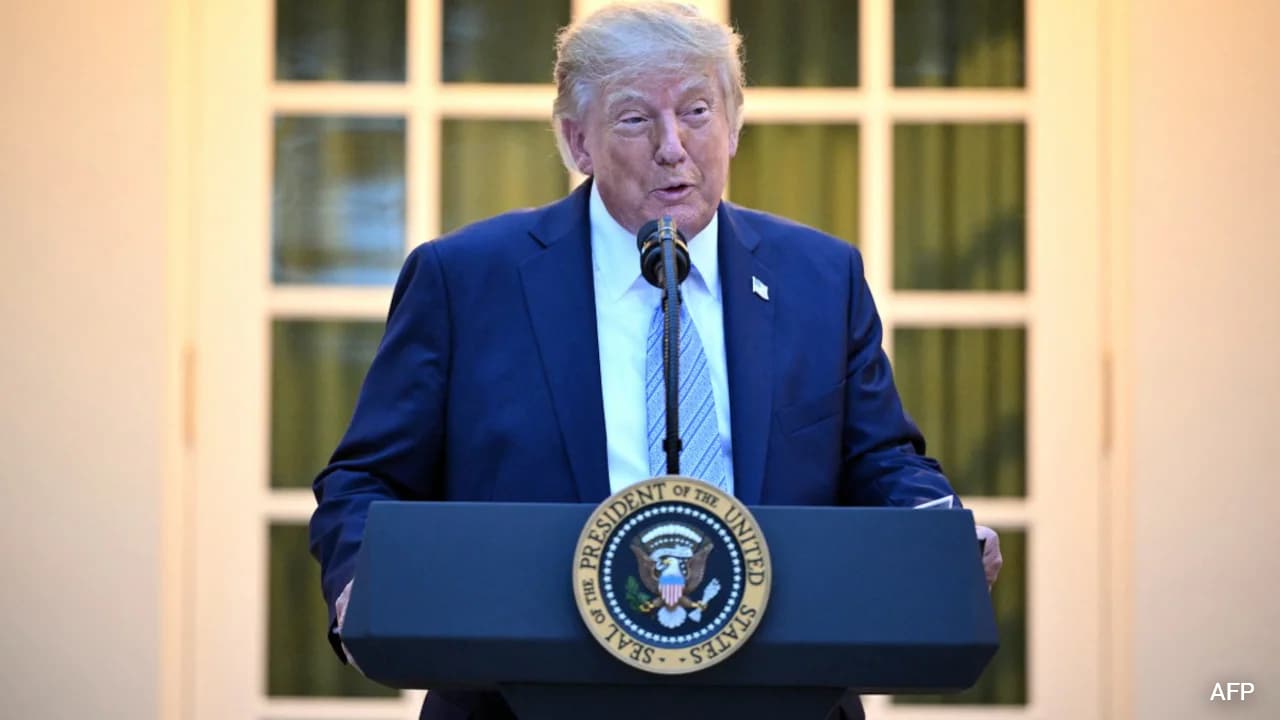
Trump Accuses CNN, Politico of Distorting Coverage, Files White House Lawsuit

President Donald Trump has filed a lawsuit against CNN and Politico, accusing the news organisations of distorting his record and misrepresenting his administration's work. Trump claimed the outlets posed a threat to democracy through their coverage. He insisted that the Oval Office deserves decorum, respect, and dignity, framing the legal action as a defense of presidential integrity. The lawsuit marks an escalation in Trump's long-running conflict with certain mainstream media organisations.

0
ProgrammingHacker News ·

Spymarks: How Digital Watermarks Can Be Used to Track Users

A newly discussed concept called 'spymarks' highlights how digital watermarks, traditionally used to protect intellectual property, can also function as covert tracking tools. Unlike standard watermarks that identify content ownership, spymarks can embed hidden identifiers that reveal information about the recipient or viewer. The article, published on brand.io, raises concerns about the dual-use nature of watermarking technology. The discussion has gained traction on Hacker News, prompting debate around privacy implications of widely used digital marking systems.

0
ProgrammingDEV Community ·

How to prioritize zero-day patching when resources fall short

Most organizations cannot patch every vulnerability immediately due to resource limits, legacy systems, and the risk of patch-induced outages. Zero-day vulnerabilities are especially challenging because they are exploited before vendors release a fix, leaving defenders with incomplete information and a narrow response window. Security experts recommend a risk-based triage approach rather than blanket emergency patching across all infrastructure. The strategy centers on identifying the most critical assets first — such as systems holding sensitive data or public-facing servers — and deploying compensating controls where direct patches are not yet safe to apply. This selective patching framework aims to reduce overall risk exposure while buying time to address less critical systems in a controlled manner.

0
ProgrammingDEV Community ·

GTK's GtkListView Factory Explained: How Setup, Bind, and Unbind Work

A developer tutorial series on GTK widgets has published a detailed guide explaining the full lifecycle of SignalListItemFactory in GtkListView. The factory uses four signals — setup, bind, unbind, and teardown — where setup builds widget trees once per recycled row slot and bind fills them with item-specific data on every reuse. Because GTK recycles row slots during scrolling rather than creating new widgets per item, bind behaves more like an update function than a constructor, a distinction the API does not make obvious. Failing to implement unbind can cause subtle bugs, such as CSS classes accumulating across recycled rows or signal handlers stacking up and firing multiple times. The guide stresses that unbind is the correct place to reverse anything bind applies, rather than patching bind itself to handle both states.

0
ProgrammingDEV Community ·

How Layered Layouts Keep Large JSON Editors Fast During Edits

Editing large JSON documents in browser-based visualizers can cause page freezes when tools recompute the entire layout after every change. Developer Treease, while optimizing for 50 MB documents, identified that separating data, layout, and viewport into distinct layers significantly reduces unnecessary computation. A layered layout approach derives node positions directly from JSON structure and reading order, rather than balancing the whole graph globally. This means adding or modifying a single field only triggers recalculation of the affected subtree, leaving unrelated nodes untouched. The approach preserves full document context for features like search and navigation while keeping incremental and streaming updates efficient.

← NewerPage 1448 of 6019Older →