0
0
WorldBBC World ·
Hyrox athlete forfeits win after completing race despite soiling herself
Polish Hyrox athlete Joanna Wietrzyk has issued a public apology following a controversial incident at a recent fitness competition. She continued racing and crossed the finish line despite having soiled herself during the event. Wietrzyk has since forfeited her winning result from the competition, which took place last week. The incident drew widespread attention and prompted debate about sportsmanship and conduct in competitive fitness events.

0
Crypto & Web3CoinDesk ·
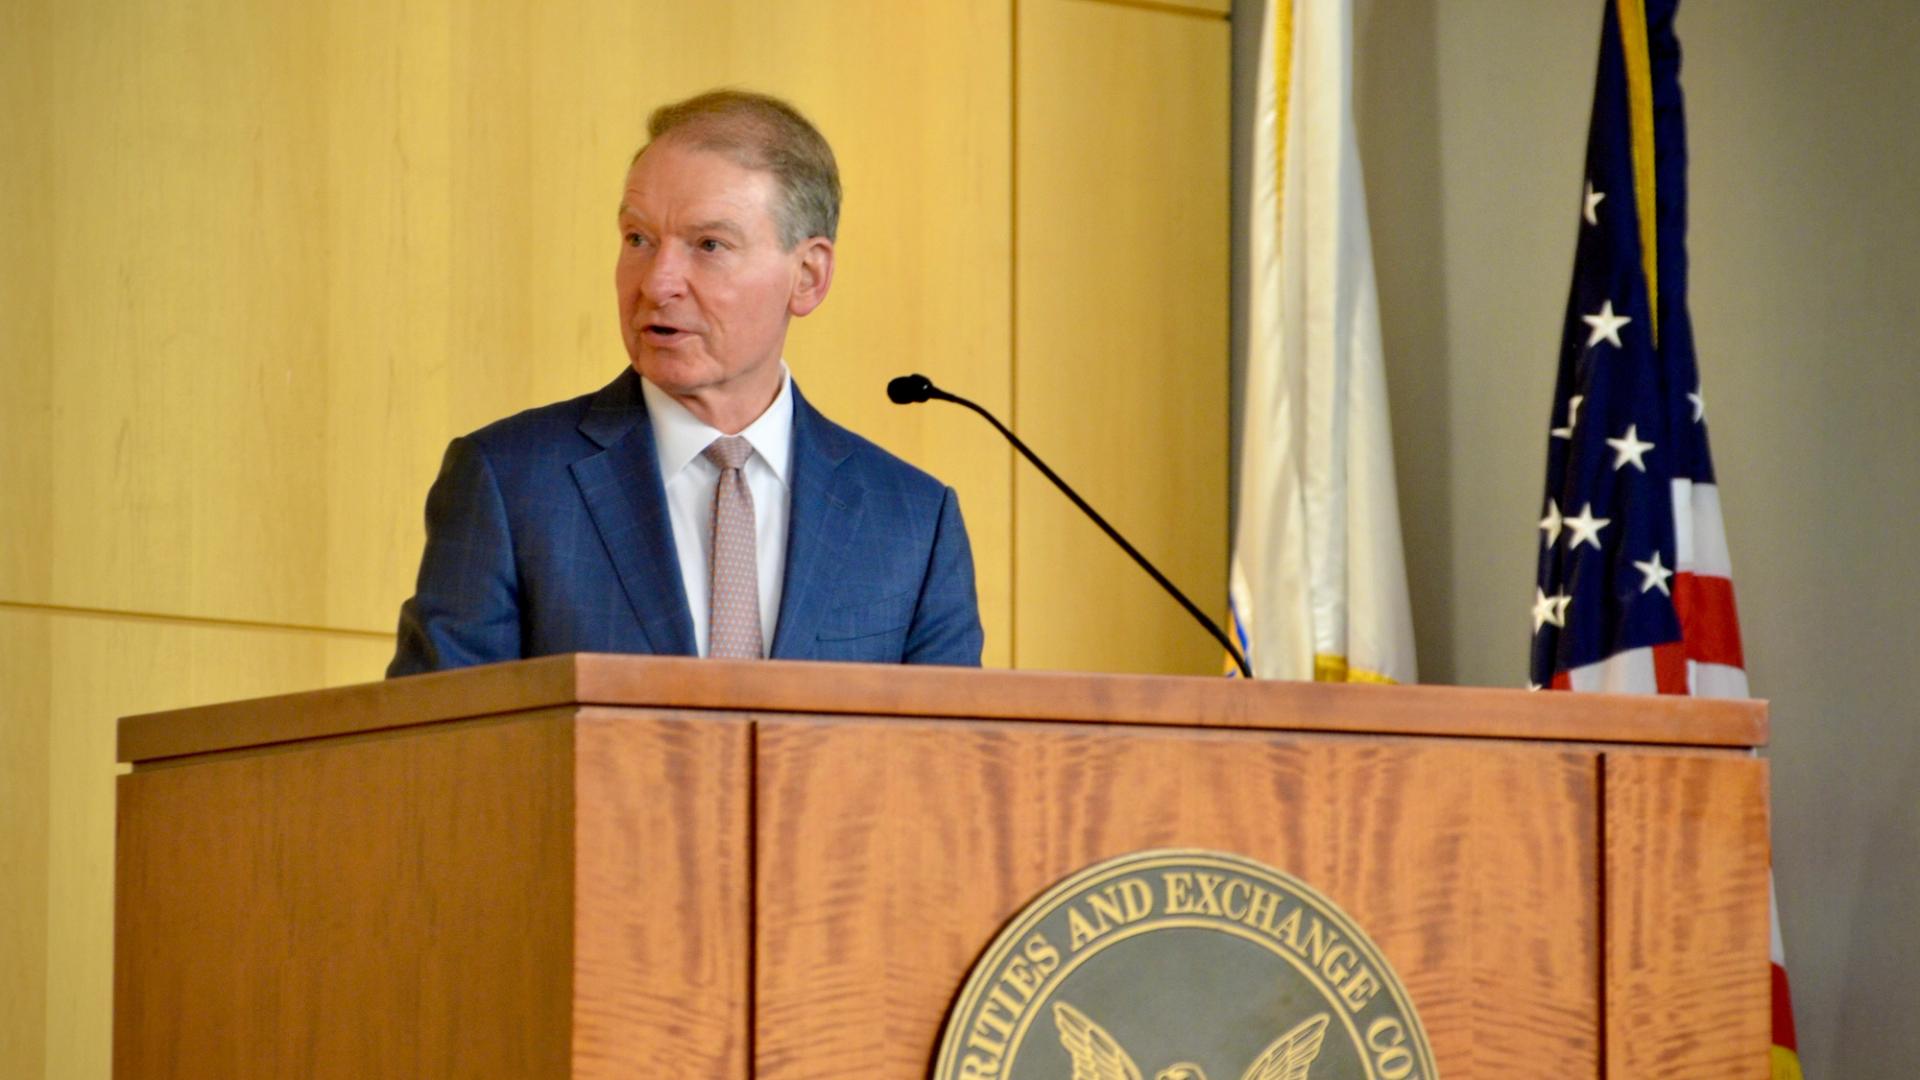
SEC explores 24/7 trading as it greenlights tokenized securities
The U.S. Securities and Exchange Commission has begun laying groundwork for around-the-clock stock trading, a model already standard in cryptocurrency markets. The agency held a dedicated event to discuss the possibility of continuous trading in traditional securities markets. The same morning, the SEC also approved tokenized securities, signaling a broader push toward modernizing market infrastructure. The dual developments suggest regulators are increasingly open to adopting practices long associated with digital asset markets.
0
TechnologyTechCrunch ·
TechCrunch Disrupt 2026 Volunteer Applications Closing Soon
TechCrunch is urging interested individuals to submit their volunteer applications for Disrupt 2026 before the deadline passes. The annual Disrupt event is one of the most prominent gatherings in the tech startup world. Prospective volunteers who have been hesitant are being encouraged to act quickly. The application window is nearing its close, making this a final opportunity for those wishing to participate.
0
ProgrammingDEV Community ·
Interactive Simulators Help Developers Master TLS Handshakes and OAuth Flows
Two free browser-based simulators aim to help backend developers learn the TLS handshake and OAuth authorization code flow by stepping through each sequence interactively, rather than studying static diagrams. The TLS simulator covers both TLS 1.2 and 1.3 protocols, highlighting key differences such as the single round trip and post-ServerHello encryption introduced in 1.3, while also letting users simulate failure scenarios like expired certificates, hostname mismatches, and untrusted certificate chains. The OAuth simulator walks developers through the full authorization code flow with PKCE, covering every party — the app, user, authorization server, and API — and showing exactly what data moves across each channel. A core learning point is understanding which secrets, such as the authorization code versus tokens, are exposed in the browser-facing channel versus the back-channel token exchange. Both tools require no signup and are intended to build the kind of hands-on familiarity that helps developers debug real-world security errors under pressure.
0
TechnologyTechCrunch ·
Tovala Smart Oven Review: Does the QR-Code Meal System Beat Takeout?
Tovala is a company that offers a smart oven paired with a dedicated meal-delivery service. Each delivered meal includes a QR code that users scan through the Tovala app. The scanned code allows the oven to automatically read and execute the correct cooking instructions for that meal. The system is designed to simplify home cooking by removing the need for manual temperature or time settings. A hands-on review evaluated whether the convenience of this setup is a practical alternative to ordering takeout.
0
TechnologyThe Verge ·
Camp Snap 110D brings screenless digital twist to retro 110 film camera design
Camp Snap has announced the 110D, a new screenless digital point-and-shoot camera inspired by the slim 110 film cameras popularized in the 1970s. The pocket-sized device draws design cues from budget cameras by Canon, Minolta, and Pentax that used the 110 film cartridge format Kodak introduced in 1972. The 110D is now available for preorder at $74.95 and comes in two color options — back in black and dreamsicle — along with matching accessories. It is the latest addition to Camp Snap's small but growing lineup of minimalist, display-free digital cameras aimed at casual shooters.

0
TechnologyThe Verge ·
Waymo Robotaxi Detected Firearm, Alerted Police, Leading to Two Teen Arrests
In early September, two teenagers riding a Waymo autonomous vehicle in Los Angeles were arrested after the company detected what it described as a terms-of-service violation involving a firearm. Waymo pulled the car over and alerted emergency services, after which police allegedly found a loaded AR-style ghost gun inside the vehicle. The incident has raised broader questions about privacy expectations for passengers in self-driving cars. Concerns now center on what autonomous vehicles record, how that footage is stored, and under what circumstances it may be shared with law enforcement.

0
ProgrammingDEV Community ·
Why Software Engineering Is a Discovery Problem, Not a Production Line
A widely discussed essay argues that most engineering teams mismanage software delivery by treating it like factory output, pushing for speed through added staff, pressure, or process gates — all of which research shows make delivery slower. Drawing on Fred Brooks' 'Mythical Man-Month' and the State of DevOps Report, the piece contends these traditional management levers consistently backfire. The author proposes reframing engineering as continuous discovery, where the primary goal is minimizing the time it takes to validate a hypothesis rather than maximizing output. Practical recommendations include treating every code change as a testable hypothesis, using automated pipelines to shorten feedback loops, and deploying in small increments to isolate variables. The central argument is that optimizing for learning — not speed — is what organically produces faster, higher-quality software delivery.
0
ProgrammingDEV Community ·
KREMLIN Malware Forges Chrome Integrity Checks to Hijack Brazilian Banking Sessions
Elastic Security Labs has tracked a high-severity malware campaign called KREMLIN across seven operations over 15 months, targeting banking users in Brazil. The attack begins when a user opens a JavaScript file disguised as a bank receipt or invoice, which then silently downloads Node.js and establishes persistence via a scheduled task. KREMLIN uses Ethereum smart contracts as dead-drop resolvers to retrieve payloads and locate malicious browser extensions, which are injected into Chrome or Edge profiles without user consent by forging Chromium's Secure Preferences integrity checks. Once installed, the AVSync extension harvests cookies, session data, keystrokes, and HTTP traffic, and receives attacker commands over WebSocket. At the time of reporting, researchers had identified at least 1,515 infected endpoints, with blocking initial JavaScript execution identified as the most effective prevention measure.
0
ProgrammingDEV Community ·
BragJack Flaw Let Malicious Extensions Hijack AI Agents in Five Major Browsers
Security researchers at Forever Security disclosed a high-severity attack technique called BragJack, which allows a malicious browser extension to hijack built-in AI agents across Chrome, Edge, Opera Neon, Perplexity Comet, and Claude in Chrome. The attack exploits existing extension permissions—such as Declarative Net Request and debugger access—to weaken security policies, inject scripts, and force-send prompts to AI agents without additional user interaction. Affected products included Google Gemini, Microsoft Copilot, Opera Neon, Perplexity Comet, and Claude, with proof-of-concept demonstrations showing unauthorized access to files, emails, camera feeds, and authenticated websites. The vulnerabilities were assigned CVE-2026-0628 and CVE-2026-55945, and all affected vendors have since issued fixes. No exploitation in the wild has been reported by the cited sources.
0
ProgrammingDEV Community ·
Google Patches Actively Exploited Pixel Modem Zero-Day CVE-2026-58704
Google has disclosed a high-severity vulnerability, CVE-2026-58704, affecting the cellular modem in Pixel devices, with evidence of limited targeted exploitation in the wild. The flaw involves a logic error that bypasses permission checks, allowing privilege escalation without requiring prior access or any user interaction. An attacker must be physically nearby or in adjacent range of the target device to exploit the vulnerability. Google addressed the issue in the September 5, 2026 security patch level, released as part of the September 2026 Pixel Update Bulletin. Users are advised to apply the update immediately and verify their device patch level is 2026-09-05 or later.
0
ProgrammingDEV Community ·
Iranian State Hackers Deploy CHOSEN BRICK Malware to Spy on Dissidents via Telegram
A joint advisory from the NCSC, FBI, and AIVD warns that Iranian state-sponsored cyber actors have been targeting dissidents, activists, and journalists worldwide since at least 2025. Attackers pose as trusted contacts or technical support on WhatsApp and Telegram to trick victims into running a malicious Windows file disguised as a legitimate application. Once executed, the CHOSEN BRICK malware silently collects screen activity, audio, emails, and messages, relaying stolen data to attacker-controlled Telegram bots or cloud storage. The malware establishes persistence via Windows registry run keys and evades detection by adding itself to Microsoft Defender exclusions. Capabilities including file deletion and device wiping have been confirmed, raising serious physical safety concerns for targeted individuals.
0
ProgrammingDEV Community ·
Critical WSO2 API Manager Flaw Allows Auth Bypass via Forged JWT Tokens
A critical authentication bypass vulnerability, CVE-2026-5430, has been identified in WSO2 API Manager and related products, carrying a maximum CVSS score of 10.0. The flaw allows unauthenticated attackers to forge JSON Web Tokens using unsupported signing algorithms, bypassing authentication entirely. Security firm watchTowr detected initial exploitation attempts on September 13, 2026, and confirmed the bypass grants access to API backend destinations, credentials, and registered application secrets. Successful exploitation could enable administrator account takeover and serve as a launchpad for lateral movement into internal services. WSO2 has issued a security advisory urging organizations to apply product-specific updates or community edition patches immediately.
0
0
ProgrammingDEV Community ·
Critical RCE Flaws in The Events Calendar Plugin Put 200,000+ WordPress Sites at Risk
Two critical unauthenticated vulnerabilities (CVE-2026-78006 and CVE-2026-78159), each scoring 9.8 on the CVSS scale, have been identified in The Events Calendar WordPress plugin by Wordfence Argus. The flaws allow anonymous attackers to achieve remote code execution by posting a crafted comment on an event page and previewing it via a moderation-hash URL, without requiring login or admin approval. The first attack chain exploits unsafe PHP deserialization to execute OS commands directly on the web server, while the second uses an extract()-based code path to change the administrator password, enabling malicious plugin installation. Both chains are triggered because the plugin incorrectly processes unapproved comments as Gutenberg blocks, passing attacker-controlled data through insufficient security checks. No exploitation in the wild has been reported so far, but sites with comments enabled on public event pages are considered at immediate risk.
0
ProgrammingDEV Community ·
Express Middleware Explained: Key Patterns, Gotchas, and Best Practices
Express middleware consists of a sequential stack of functions that can access request and response objects, execute code, and pass control via next(). Developers can chain single-purpose middlewares — such as authentication and role checks — directly within route definitions instead of bundling all logic into one controller. A common pitfall is forgetting to call next() or send a response, which causes the client browser to hang indefinitely. Error-handling middleware must declare exactly four parameters to be recognized by Express, and in Express 4, async errors must be explicitly forwarded using next(err). Express 5 addresses this by natively catching rejected promises in async middleware.
0
Crypto & Web3CoinDesk ·
U.S. Crypto Industry Faces Setback as Clarity Act Stalls in Congress
The failure of the Clarity Act to advance is expected to put the United States at a competitive disadvantage against foreign crypto markets in the near term. The crypto industry has been seeking clear legal frameworks to operate with greater certainty and confidence. Without dedicated legislation, the sector may look to more crypto-friendly jurisdictions abroad for growth and development. However, existing regulatory oversight from the SEC and CFTC is expected to provide some foundational structure for the industry in the interim.
0
IndiaTimes of India ·
AI Boom Set to Drive 70% of Global Data Centre Demand by 2030
Artificial intelligence is projected to account for up to 70% of global data centre demand by 2030, highlighting the sector's massive growth potential. Despite calls to slow AI development weighing on data centre stocks, broader digital transformation continues to sustain infrastructure requirements. Data centre companies are evolving their funding strategies to keep pace with rising demand. The sector is estimated to represent a $3 trillion opportunity in real estate. Institutional investors continue to show strong confidence in data centre assets as a long-term investment.
0
IndiaTimes of India ·
Abhishek Sharma hits fastest T20I century by Test-nation batter vs Afghanistan
Indian opener Abhishek Sharma scored a stunning century off just 30 balls against Afghanistan in the third T20I on Thursday. The match was played at Arun Jaitley Stadium. His innings is now the fastest T20I hundred by a batter from a Test-playing nation. Sharma's explosive power-hitting set a new benchmark in the shortest format of international cricket.