SShortSingh.
0
ProgrammingDEV Community ·

AI Coding Tools Routinely Ship Broken Access Controls, Open-Source Scanner Aims to Prove Fixes Work

A common security flaw in AI-generated code allows any user to access another user's private data simply by changing an ID in a URL, because AI tools default to using service-role keys that bypass row-level security. This vulnerability has been observed repeatedly in apps built with tools like Lovable, Bolt, v0, Cursor, and Claude Code. An open-source scanner called auditai-scanner was built specifically to detect and verify fixes for this flaw, going beyond flagging potential issues by reproducing them in a sandboxed environment with synthetic test users. Rather than relying on the same AI model to both write and evaluate a fix, the tool independently confirms whether a cross-tenant data leak is actually closed before marking a finding as resolved. The project also generates a regression test from each reproduction, ensuring the vulnerability cannot be silently reintroduced in future code changes.

0
ProgrammingDEV Community ·

Agentic AI Coding Tools Demand Better Design, Tests, and Guardrails: Developers

Software engineers are expressing fatigue over AI hype, job market uncertainty, and the growing push toward agentic coding tools. While AI agents can rapidly modify large codebases, their effectiveness depends heavily on well-documented code, clear requirements, and defined success criteria. Without automated UI and integration tests, validating agent-driven changes at scale remains unreliable, posing risks to production stability. Quality assurance engineers are being urged to upskill in test automation to keep pace with aggressive AI-generated code changes. Despite concerns about an AI bubble, open-source LLMs are expected to persist, with companies increasingly likely to self-host models for internal use.

0
ProgrammingDEV Community ·

Developer Tests Three AI Coding Agents for 30 Days on Real Projects

A software developer spent 30 days evaluating Claude Code, GitHub Copilot CLI, and Cursor in agent mode on real-world projects, including a SaaS API, a data pipeline, and a legacy Node.js service. The tests showed significant time savings for boilerplate tasks, with routine REST endpoint generation dropping from 45 minutes to around 8 minutes. However, complex logic such as multi-step payment flows failed on the first attempt roughly 60% of the time, and agents performed poorly when debugging production-only bugs. Larger codebases caused context-tracking issues across all three tools, with agents occasionally referencing methods or types that no longer existed. The author concluded that AI coding agents offer genuine productivity gains for structured, repetitive work but still require human review for anything beyond straightforward scaffolding.

0
ProgrammingDEV Community ·

Researcher Built a Canary Executable to Spy on VirusTotal Sandboxes

A developer created a Rust-based executable with a fake identity — dubbed 'ZeroToken Engine' — and submitted it to VirusTotal to observe the analysis environments that ran it. The program collected metadata such as OS version, CPU and memory specs, uptime, hostname, and running process names, then reported findings via DNS heartbeats and HTTPS dossiers to the researcher's own infrastructure. It used two reporting channels: compact encoded DNS lookups and fuller CBOR-formatted HTTPS payloads, each tagged with a random eight-byte run ID. The experiment captured 353 event rows across 21 run IDs over a roughly five-hour window on September 12, 2026. The researcher noted that the binary installed nothing, harvested no credentials or documents, and intentionally disclosed the canary's true behavior in the project's README alongside its cover identity claims.

0
ProgrammingDEV Community ·

Safer AI Automations: Why a Validation Layer Should Sit Between AI and Action

A software developer has shared a design pattern aimed at making AI-powered workflows safer and more reliable in production environments. The core idea is to separate the AI's role — understanding unstructured user input and extracting key details — from the workflow's role of enforcing business rules and triggering actions. Under this approach, an AI model never directly executes critical operations; instead, its output is validated against predefined rules before any action is taken. Recommended safeguards include duplicate-action prevention, retry limits, timeouts, and a human handoff option when the AI is uncertain. The pattern can be applied across popular automation platforms such as n8n, Make, or custom API-based systems.

0
ProgrammingHacker News ·

A curated list of sci-fi books exploring how societies are built and justified

A reader has shared a personal selection of science fiction books centered on the theme of how human societies are constructed and rationalized. The list is published on BookDNA, a book recommendation platform. The post appeared on Hacker News, receiving minimal engagement with 4 points and no comments at the time of reporting. The collection appears aimed at readers interested in the sociological and philosophical dimensions of speculative fiction.

0
IndiaNDTV ·

Iran and UAE Hold Bilateral Talks at BRICS Summit with India's Facilitation

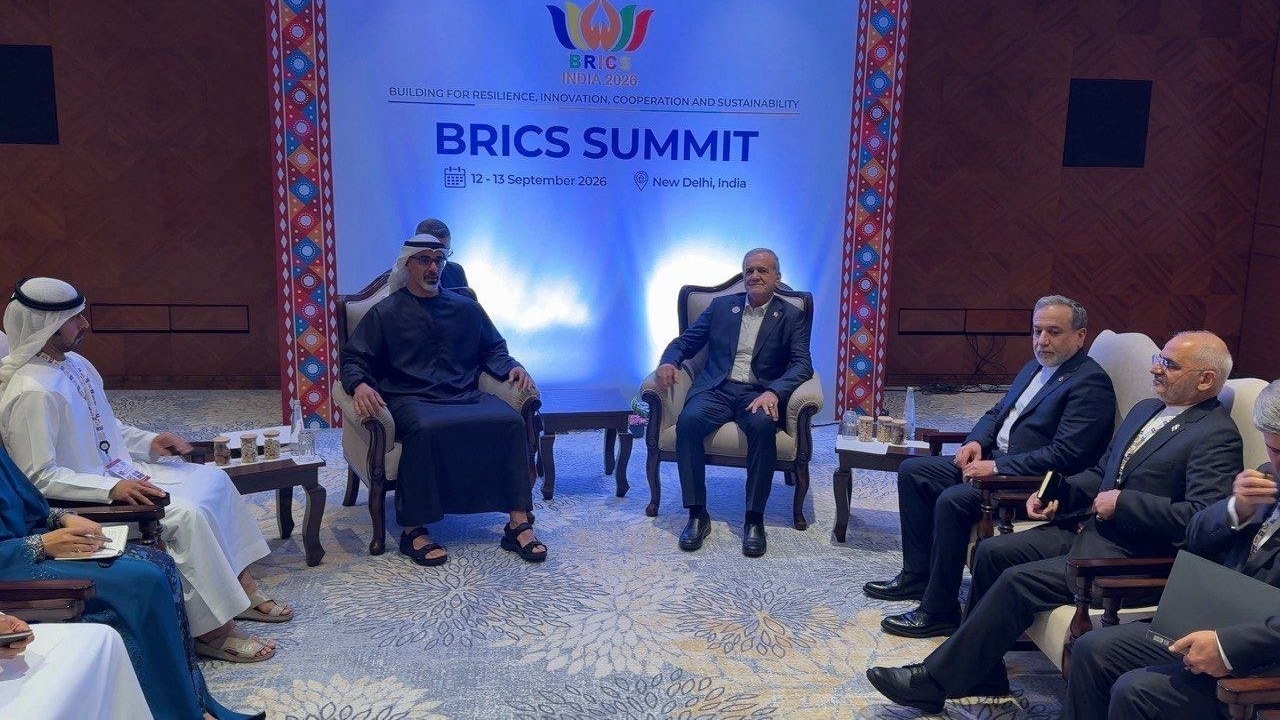
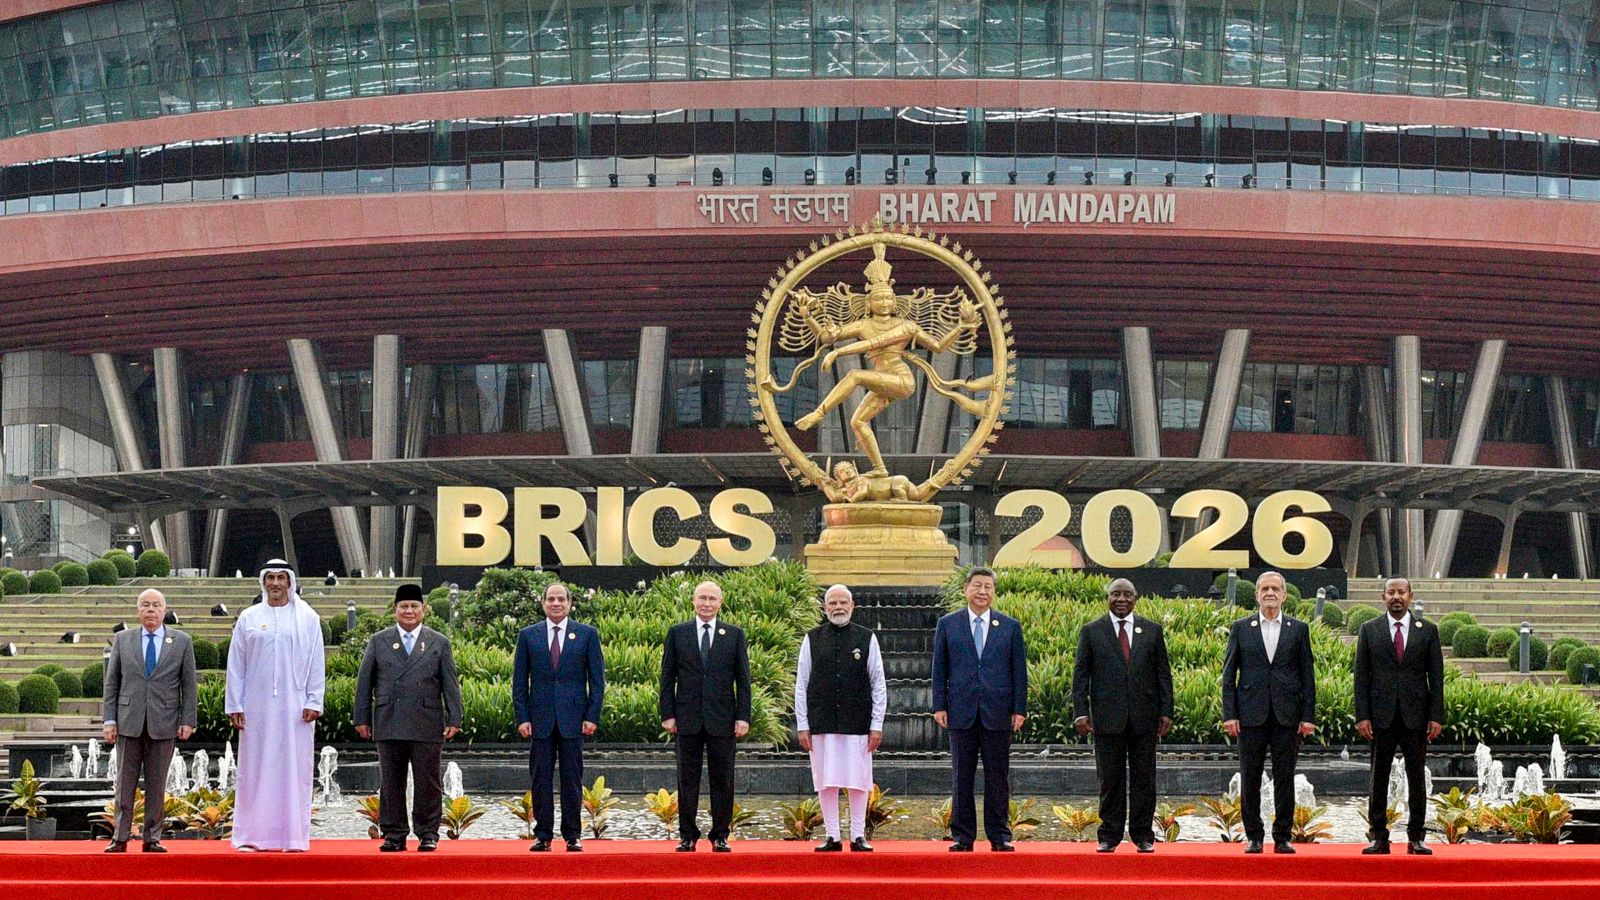
Iranian President Masoud Pezeshkian met Abu Dhabi Crown Prince Khaled bin Mohamed bin Zayed on the sidelines of the BRICS summit on Saturday. The meeting marked a notable diplomatic engagement between the two nations, which have historically had tense relations. India played a facilitative role in bringing the two sides together for the bilateral talks. The encounter took place within the broader diplomatic setting of the BRICS summit.

0
ProgrammingDEV Community ·

Why AI Chat Failover Needs Accessible Origin Announcements, Not Just Spinners

A developer discovered a critical accessibility flaw while conducting a keyboard-only audit of a streaming chat application: when the local inference path failed and silently switched to a remote server, screen readers and keyboard users received no indication of the origin change. The skeleton overlay that appeared during the failover stole focus and marked the main landmark as aria-busy, trapping assistive technology users without any announcement of where their data was being sent. The root cause was a single boolean state variable that treated local and remote streaming as identical, collapsing a meaningful privacy transition into a generic loading animation. The developer argues that the real defect is not the spinner's appearance but the absence of an origin state model that distinguishes on-device processing from remote server calls. A structured state table is proposed — covering idle, streaming-local, needs-consent, streaming-remote, error, and cancelled states — to ensure focus management, live region announcements, and user consent controls are all tied to where tokens actually originate.

0
ProgrammingDEV Community ·

Silent Citation Decay: How a Green Coverage Check Missed 23 Wrong Line Numbers

A developer discovered that all 23 line-number citations in a specification table were incorrect by one or two lines, yet an automated coverage check remained green throughout. The check only counted whether citation cells were non-empty, never verifying whether the references actually pointed to the correct content. The citations had been accurate when first written but silently drifted as other edits shifted line positions in the source file. To fix this, the developer replaced line-number-dependent references with quoted text snippets, allowing the tool to detect whether a citation had moved, gone missing, or remained valid. This shift from positional to keyed checking meant the system could now name the specific failing row rather than simply returning a misleading count of zero uncovered items.

0
ProgrammingDEV Community ·

Prompt Injection Is a Permissions Problem, Not a Model Problem

Prompt injection attacks occur when malicious instructions hidden inside documents — such as PDFs — manipulate an AI assistant into executing unintended actions, like leaking private files. The attack works because language models process user instructions and document content as a single stream of tokens, making it structurally difficult to distinguish intent from data. Common defences like system prompts and refusal training raise the cost of attacks but cannot eliminate the risk, since they operate within the same text-based substrate as the attack itself. The author argues that true security requires placing access controls outside the model entirely — in a permission table that no document content can modify or influence. This approach ensures that blocked files remain invisible to the model, that access decisions are looked up rather than reasoned about, and that every failed injection attempt is logged for review.

← NewerPage 1142 of 5220Older →