0
0
0
ProgrammingHacker News ·
Genuine Creativity Is Your New Moat (2026)
Article URL: https://www.inventbuild.studio/blog/genuine-creativity-is-your-new-moat Comments URL: https://news.ycombinator.com/item?id=49648732 Points: 9 # Comments: 3
0
0
Crypto & Web3CoinDesk ·
SEC Proposal to Overhaul Transfer-Agent Rules May Simplify Tokenized Securities
The U.S. Securities and Exchange Commission has put forward a new proposal to reform existing transfer-agent regulations. The plan targets the issue of duplicate off-chain shareholder records, which currently create significant reconciliation burdens. If adopted, the changes could reduce operational costs for firms dealing in tokenized securities. The proposal also aims to lower the legal uncertainty that has long complicated the tokenized securities space.
0
0
ProgrammingDEV Community ·
Developer builds DeepSeek Harness plugin in a week at zero API cost using free promotion
A developer who set out to review DeepSeek Harness (DSH), an open-source AI tool framework, ended up authoring and shipping a plugin called dsh-model-pricing within a week. The plugin surfaces per-token pricing for 7,178 models across 213 providers, overlays that data against the 788 models the harness can directly invoke, and flags discrepancies rather than averaging them. It also enables same-model, cross-provider cost comparisons and groups subscription plans separately to avoid skewing per-token rankings. The entire project was built using DeepSeek via B.AI's free API promotion, resulting in zero LLM costs across roughly 22 hours of development. The plugin is publicly available under the Apache-2.0 license and installs directly through the harness's own plugin manager without requiring a repository fork.
0
ProgrammingDEV Community ·
Developer Builds Event-Driven Order Processing System Using AWS and Terraform
A developer has published a detailed guide on building a production-style, event-driven order processing system using multiple AWS services and Terraform for infrastructure management. The architecture uses API Gateway to accept incoming orders, which are stored in DynamoDB and queued via Amazon SQS for asynchronous processing by a separate Lambda function. Orders move through three lifecycle states — PENDING, PROCESSING, and COMPLETED — without the API needing to wait for processing to finish. Failed messages are automatically retried, and those exceeding a maximum receive count are routed to a Dead-Letter Queue to prevent data loss. The entire setup is defined as Infrastructure as Code using Terraform, with CloudWatch handling logging and EventBridge firing an OrderCompleted event upon successful processing.
0
ProgrammingDEV Community ·
Google's Gemma 4 AI Model Runs on a 4 GB Laptop GPU Using QAT Compression
A developer has demonstrated that Google's Gemma 4 E2B language model can run on a 2021 Lenovo Yoga 9 laptop equipped with a 4 GB GTX 1650 Ti GPU, using a Quantization-Aware Training (QAT) checkpoint. The model's standard bfloat16 format requires 9.5 GiB of memory, far exceeding the GPU's 4 GB ceiling, but the QAT version reduces the GPU-resident portion to just 1.31 GiB. Unlike standard post-hoc quantization, QAT trains the model with 4-bit storage in mind from the outset, preserving quality while dramatically cutting memory use. The compressed model loaded in 1,618 MiB, left over half the GPU free, and achieved a decode speed of 73.75 tokens per second. The developer also published a suite of Python MCP tools on GitHub to simplify managing the llama.cpp-based local deployment.
0
IndiaNDTV ·
Al Qaeda at 25: Weakened but Still an Ideological Force, Experts Warn
Twenty-five years after the 9/11 attacks, al Qaeda remains a relevant force in global militancy despite significant setbacks over the decades. The group suffered a major blow in 2011 when US forces killed its founder Osama bin Laden. The rise of the Islamic State further weakened al Qaeda by drawing away fighters and attention as a rival extremist organization. However, experts caution that al Qaeda continues to provide support and ideological inspiration to militant groups, particularly across Africa.
0
ProgrammingDEV Community ·
TRIZ Should Follow Diagnosis, Not Replace It, Research Finds
A technical note co-authored by engineer Anton and his AI co-founder Mycroft, cross-validated through four large language models, argues that TRIZ methodology is widely misapplied in software engineering. The research concludes that engineers must first reproduce a failure, gather evidence, and establish a causal chain before reaching for TRIZ's contradiction-solving tools. Using TRIZ before the root cause is known risks reframing an unresolved bug as an 'inventive problem,' leaving the actual fault intact. Of the full TRIZ toolkit, only three approaches — articulating trade-offs clearly, applying the Ideal Final Result, and cautious trimming — showed practical value for everyday engineering work. The study also found notable disagreement among AI models on several of TRIZ's 40 principles, cautioning against wholesale adoption of the complete methodology.
0
IndiaNDTV ·
Zelensky Rules Out Trilateral Peace Talks Before Russian Elections
Ukrainian President Volodymyr Zelensky announced on Thursday that no trilateral peace negotiations would take place before Russia's upcoming elections. The statement signals Ukraine's firm stance on the timing of any diplomatic efforts to resolve the ongoing conflict. Zelensky's remarks effectively put a pause on prospects for a three-way peace dialogue in the near term. The declaration underscores the complex political considerations shaping the path toward potential negotiations between the warring parties.
0
ProgrammingDEV Community ·
SQLFluff Auto-Fixer Corrupted SQL in 2 of 2,249 Test Cases, Developer Finds
A developer systematically ran 2,249 test fixtures from the SQLFluff SQL linter through its auto-fix feature to check whether the fixer ever produced output the tool itself could not parse. Across 28 dialects, the experiment flagged 8 corruption cases and 31 instability cases, but careful triage reduced these to just 2 genuine bugs. One confirmed bug involved whitespace removal causing adjacent tokens to fuse — for example, turning '- -' into '--', which SQL interprets as a line comment, silently discarding data. The second bug involved MySQL and MariaDB account-spec syntax where a formatting rule conflicted with 'user'@'host' expressions. The author emphasizes that distinguishing real bugs from false positives — such as pre-existing parser gaps or expected single-pass instability — was the critical skill in making a credible bug report.
0
ProgrammingDEV Community ·
AI Coding Agents Rely on Human Copy-Paste Instead of Direct Environment Access
AI debugging agents in tools like Claude Code and GitHub Copilot frequently cannot directly access terminals, databases, or CI logs, forcing developers to manually copy and paste output into chat windows. This human relay introduces multiple layers of filtering — from what the developer chooses to copy to what the tooling silently truncates — stripping away details that are often critical to diagnosing bugs. The problem is well-documented in public issue trackers for Claude Code and Copilot, with users reporting that the workaround leads to slower, error-prone 'shotgun debugging' where agents guess solutions without concrete runtime evidence. Tools to fix this already exist, including read-only MCP servers for databases, Kafka, and Kubernetes, yet agents often leave such direct-access capabilities unused. Experts argue the full solution requires not just granting agents environment access, but also maintaining a transparent record of what was queried, what was returned, and how each conclusion was reached.

0
IndiaNDTV ·
Escaped NCB Drug Suspect Rearrested in Jalandhar After Attempted Disguise
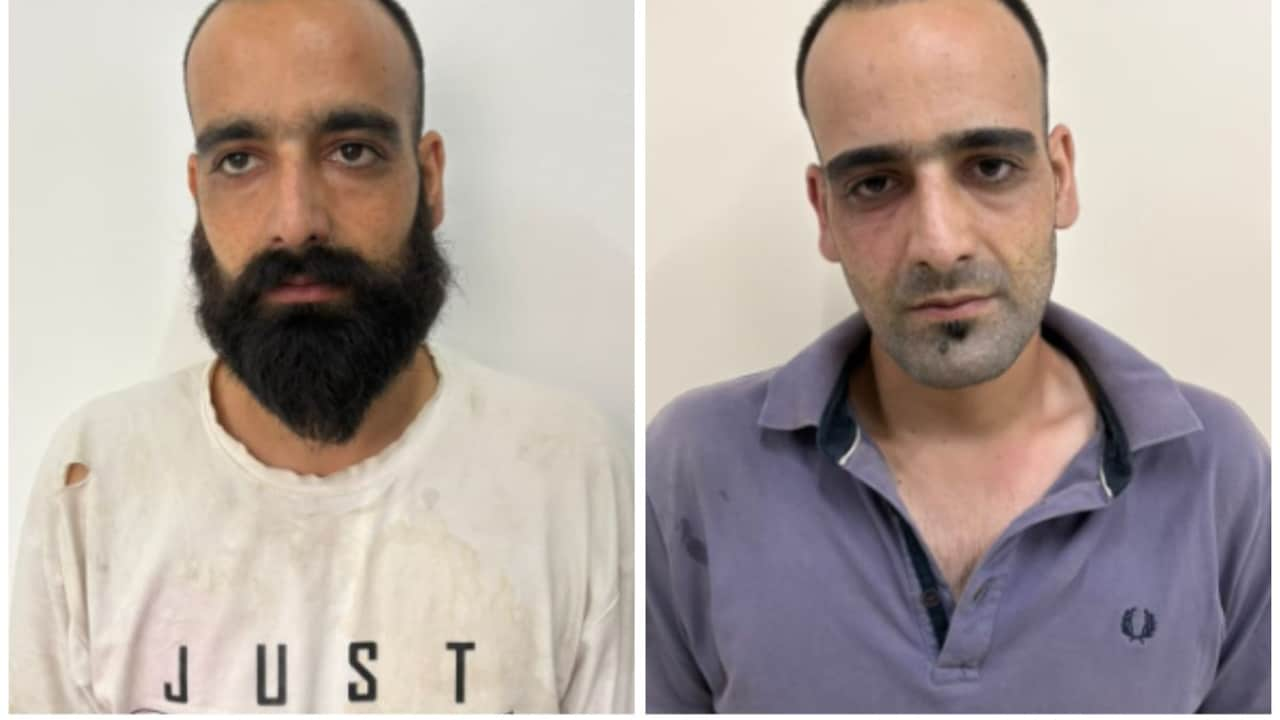
Aqib Bashir, a drug smuggling suspect who had previously escaped from Narcotics Control Bureau custody in Jammu, was recaptured in Jalandhar, Punjab. His rearrest was the result of a coordinated joint operation involving the NCB, Jammu and Kashmir Police, and Punjab Police. Bashir had reportedly attempted to alter his appearance to evade detection by law enforcement. The operation highlights inter-agency cooperation in tracking down fugitives wanted on drug-related charges.
0
IndiaNDTV ·
Assam Police Officer Arrested for Alleged Links to ONGC Pipeline Oil Theft
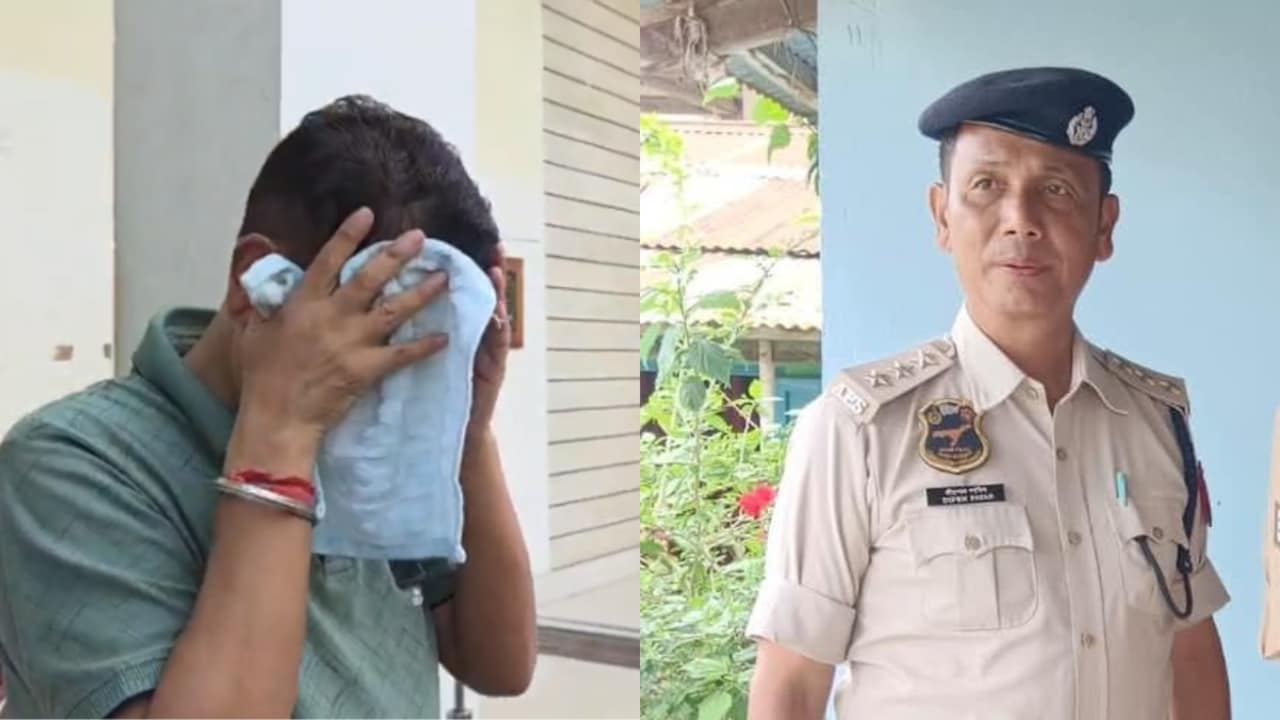
An Assam police officer has been arrested over suspected connections to a crude oil theft racket in the state. The officer, identified as Pator, came under scrutiny during an ongoing investigation into the illegal operation. The racket allegedly involved stealing crude oil by puncturing an ONGC pipeline located in Sarupathar. Authorities uncovered the officer's alleged links to the criminal network as the probe progressed.
0
ProgrammingDEV Community ·
Why AI Agents Need a Governance Layer Between Decisions and Real-World Actions
A developer argues that the AI industry is too focused on model intelligence while neglecting what happens after an AI agent decides to act. The core concern is that authentication and permissions alone do not determine whether a specific autonomous action — such as issuing an $8,500 refund — should actually execute. The author proposes a new architectural pattern where every high-impact AI action passes through a policy decision layer before reaching execution. This governance boundary is not about distrusting AI but about building systems enterprises can reliably operate at scale. The idea is being explored through an open-source project called Ex, designed to sit between AI agents and real-world consequences.
0
IndiaTimes of India ·
Illegal High-Rise PG Buildings in Noida Villages Pose Serious Fire and Safety Risks
Densely packed multi-storey paying guest accommodations have been constructed illegally across villages in Noida, far exceeding permitted floor limits. These buildings routinely violate building codes, featuring weak structural columns and narrow surrounding lanes that block emergency vehicle access. Most structures lack basic fire safety provisions and emergency exits, putting residents at considerable risk. The boom in unsafe construction is largely fuelled by high demand for affordable housing from students and IT professionals in the area. Tenants tend to prioritise low rents over verified safety standards when choosing where to stay.
0
ProgrammingDEV Community ·
Real-world AI agents are mostly retry loops, not autonomous reasoners
A developer who has run automation systems widely marketed as AI agents says the reality of production deployment differs sharply from industry claims. According to their experience across thousands of tasks, roughly a third of runtime is spent re-executing the same actions due to page re-renders, selector changes, or anti-bot barriers like Cloudflare. The most persistent challenges are not reasoning or planning but mundane obstacles such as captchas, cookie banners, and phone verification steps that require human intervention. The developer argues that truly reliable agents are deliberately narrow in scope, with clear success conditions and comprehensive logging, while complex multi-step reasoning agents tend to fail most often. Their key takeaway for builders is to prioritize robust infrastructure and budget heavily for retry logic, as that is where the bulk of actual execution time is spent.
0
TechnologyArs Technica ·
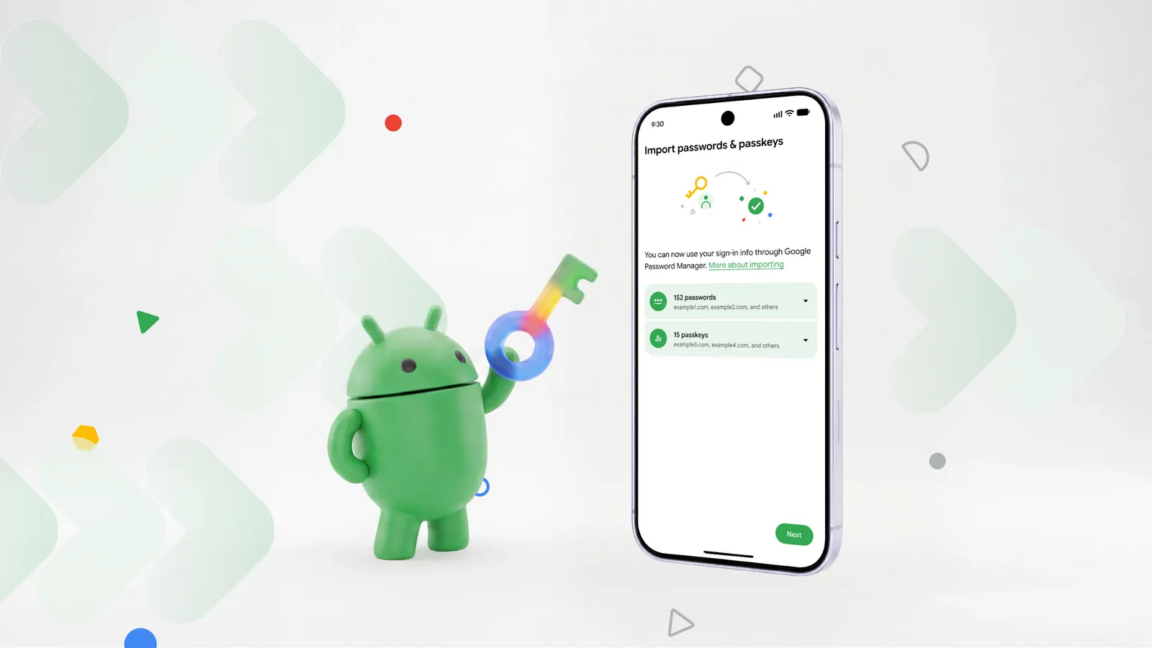
Android Gains Feature to Securely Transfer Logins Between Password Managers
Google has introduced a new Android feature that allows users to securely migrate their saved logins from one password manager to another. The capability aims to reduce friction for users who wish to switch between different credential management apps. App support for the feature is currently limited, with only a handful of compatible applications available at launch. Google has confirmed that support from additional password manager apps is expected to expand in the coming period.